
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Miele Professional PG 8528 washer-disinfector affected by a Web Server Directory Traversal

An Internet-Connected Medical Washer-Disinfector, the Miele’s model Professional PG 8528, is affected by a Web Server Directory Traversal. While the number of IoT devices continue to exponentially increase, the level of security of these smart objects is often not adequate end exposes users at risk of cyber attacks. The news of the say is a […]

Miele Professional PG 8528 washer-disinfector affected by a Web Server Directory Traversal

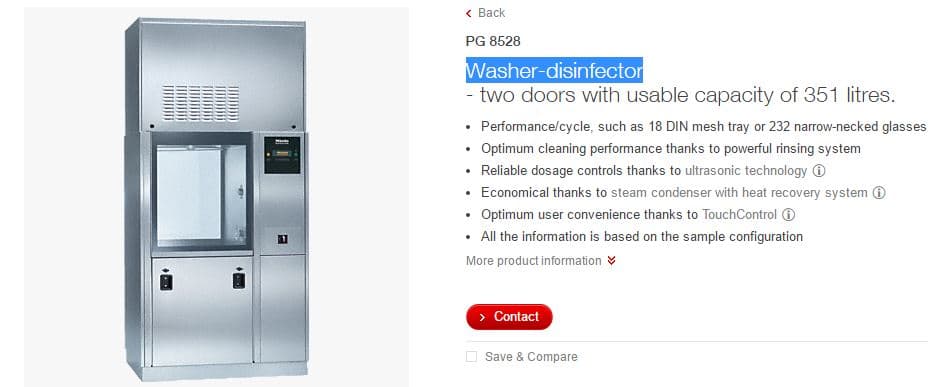
An Internet-Connected Medical Washer-Disinfector, the Miele’s model Professional PG 8528, is affected by a Web Server Directory Traversal.

While the number of IoT devices continue to exponentially increase, the level of security of these smart objects is often not adequate end exposes users at risk of cyber attacks.

The news of the say is a security vulnerability reported at Full Disclosure that affects Internet-connected washer-disinfector appliance manufactured by the Germany-based vendor Miele.

 washer-disinfector

According to the security advisory, the Miele Professional PG 8528 appliance is affected by a Web Server Directory Traversal vulnerability tracked as CVE-2017-7240. The Miele Professional PG 8528 is a medical equipment used to disinfect laboratory and surgical instruments. The flaw could be exploited by an unauthenticated attacker to access any directory on the web server.

“The corresponding embeded webserver “PST10 WebServer” typically listens to port 80 and is prone to a directory traversal attack, therefore an unauthenticated attacker may be able to exploit this issue to access sensitive information to aide in subsequent attacks.” reads the advisory.

The flaw could allow attackers to access sensitive data on the server, to drop and execute malicious code on the web server.

The flaw was discovered by the expert Jens Regel at the German consultancy Schneider & Wulf who reported the issue to Mele in December 2016. Unfortunately, he did not receive the reply from the company, so after four months he decided to publicly disclose it.

Regel also published a proof-of-concept (PoC) exploit code for this flaw, for this reason, it is important that the vendor will fix the issue as soon as possible.

Do you want to hack the Mele washer-disinfector?

It is simple, the PoC exploit code that is used by the expert to request the embedded system’s shadow file and any file on the filesystem.

Proof of Concept:
=================
~$ telnet 192.168.0.1 80
Trying 192.168.0.1...
Connected to 192.168.0.1.
Escape character ist '^]'.
GET /../../../../../../../../../../../../etc/shadow HTTP/1.1 to whatever IP the dishwasher has on the LAN.

Waiting for a patch disconnect the washer-disinfector from the Internet.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – washer-disinfector, hacking)


