
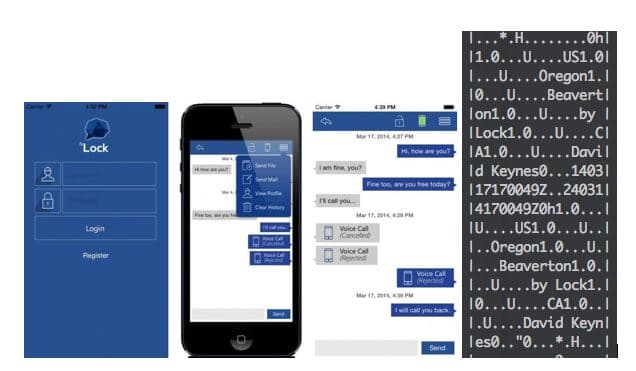
MIT (Turkish Intelligence Agency) has hacked one-single server of a messaging app in Lithuania in order to identify members of an Islamic terrorist group.
Within the harshness of political controversies turned up in Turkey with the recent coup attempt at July of 15th [1], it seems that a cyberwar between MIT [2] (Turkish National Intelligence Agency) and FETO [3] ended up revealing all key member names to the government authorities.
It all started with the release of a mobile messaging app called ByLock which seemed as a simple, ordinary messaging solution with offline mail and online voice calling capabilities developed by a guy named David Keynes from Oregon. But later on, it is understood that there is no one named as mentioned and it was a work of an illegal organization to move its whole daily communication to the underground.
Despite the “next generation of secure communication” slogan on the homepage of ByLock -which is still live at https://bylockapp.wordpress.com/- after months of the release of the application it took attention of MIT due to popularity among FETO members and it was easily decompiled into the pieces and pointed out to a server in Lithuania that all messages, passwords and ip addresses stored in plaintext.

After the hack of a server in Lithuania, security experts downloaded nearly 3.5 million messages revealing ~53000 thousand people relating to the illegal organization. It was a breach which gave a big advantage to the Turkish authorities in the mid of 2015 and after the failed coup attempt.
But this is not the end of the story. Recently, the head of “Ministry of Science, Technology and Industry”, Faruk Ozlu has revealed that there were suspicions that ByLock was the product of the secret members of FETO who were working in TUBITAK [4] (The Scientific And Technological Research Council Of Turkey). “Our investigations are still ongoing in TUBITAK and we are categorizing suspected people in 5 categories. We have taken out their jobs whom are found within 4. and 5. Category by others in 3 categories are getting checked out for evidences.” said Ozlu in September 9 to AA (Anatolian News Agency).
These news with TUBITAK are revealed footprints about another struggle which has been resulted with the wiretaps leaked in 2013 containing Tayyip Erdogan’s conversations [5] on crypto-phones developed by TUBITAK which later denied and called ‘fake’ by the authorities.
References
[1] https://en.wikipedia.org/wiki/2016_Turkish_coup_d%27%C3%A9tat_attempt
[3] https://en.wikipedia.org/wiki/G%C3%BClen_movement
[5] http://www.ibtimes.com/are-erdogan-corruption-tapes-real-1558185
[adrotate banner=”9″]
About the Author Harun Esur
 Harun Esur is founder of Sceptive, a security firm specialized on underground cyberwarfare and services for financial companies. Coding, hacking and protecting padawans in cyberworld since the invention of Commodore 64 and VICMODEM model 1600.
Edited by Pierluigi Paganini
(Security Affairs – terrorism, messaging app)


