
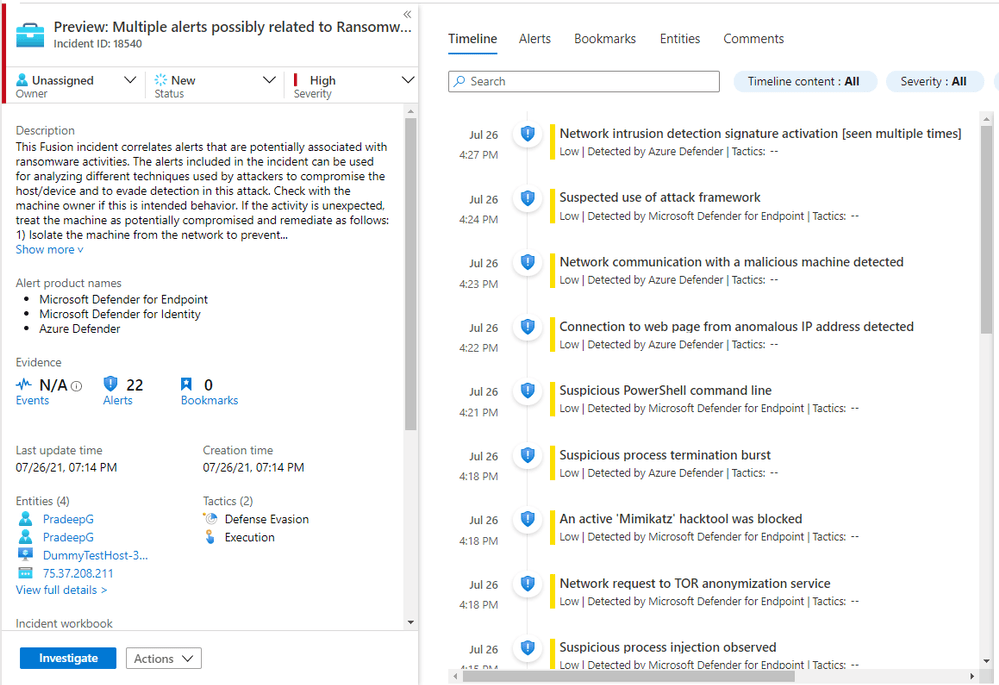
Microsoft Azure Sentinel cloud-native SIEM (Security Information and Event Management) platform used the Fusion machine learning model to detect ransomware attack.
Microsoft Azure Sentinel cloud-native SIEM is using the Fusion machine learning model to analyze data across enterprise environments and detect the activity associated with potential threats, including ransomware attacks.
When a potential ransomware attack is detected by the Fusion machine learning model, a high severity incident titled “Multiple alerts possibly related to Ransomware activity detected” will be triggered in the Azure Sentinel workspace

“In collaboration with the Microsoft Threat Intelligence Center (MSTIC), we are excited to announce Fusion detection for ransomware is now publicly available!” states the announcement published by Microsoft.
“These Fusion detections correlate alerts that are potentially associated with ransomware activities that are observed at defense evasion and execution stages during a specific timeframe.”
According to Microsoft, Fusion detection model for ransomware allows detecting malicious activities at the defense evasion and execution stages of an attack, allowing security analysts to quickly identify the threat and neutralize it.
Fusion correlates signals from Microsoft products as well as signals in network and cloud, it gathers data from the following solutions:
- Azure Defender (Azure Security Center)
- Microsoft Defender for Endpoint
- Microsoft Defender for Identity
- Microsoft Cloud App Security
- Azure Sentinel scheduled analytics rules. Fusion only considers scheduled analytics rules with tactics information.
Early detection of ransomware activity could allow security analysts to prevent the threat from spreading within the target environment and prevent serious damages.
The announcement includes examples of the Fusion detection for ransomware that shows how Fusion technology correlates alerts associated with events that could be indicating an ongoing chain of attacks, such as RDP brute-force attack, the use of a ‘Cryptor’ malware, and potential phishing activities.
Upon receiving an alert related to a potential ransomware attack scenario by Fusion in Azure Sentinel, admins will have to consider their systems as “potentially compromised” and respond to the threat.
Below are the recommendations provided by Microsoft:
- Isolate the machine from the network to prevent potential lateral movement.
- Run a full antimalware scan on the machine, following any resulting remediation advice.
- Review installed/running software on the machine, removing any unknown or unwanted packages.
- Revert the machine to a known good state, reinstalling the operating system only if required and restoring software from a verified malware-free source.
- Resolve recommendations from alert providers (e.g., Azure Security Center and Microsoft Defender) to prevent future breaches.
- Investigate the entire network to understand the intrusion and identify other machines that might be impacted by this attack.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Azure Sentinel)
[adrotate banner=”5″]
[adrotate banner=”13″]


