
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Microsoft Defender can now protect servers against ProxyLogon attacks

Microsoft announced that its Defender Antivirus and System Center Endpoint Protection now protects users against attacks exploiting Exchange Server vulnerabilities. Microsoft announced this week that Defender Antivirus and System Center Endpoint Protection now provide automatic protection against attacks exploiting the recently disclosed ProxyLogon vulnerabilities in Microsoft Exchange. “Today, we have taken an additional step to […]

Microsoft Defender

Microsoft announced that its Defender Antivirus and System Center Endpoint Protection now protects users against attacks exploiting Exchange Server vulnerabilities.

Microsoft announced this week that Defender Antivirus and System Center Endpoint Protection now provide automatic protection against attacks exploiting the recently disclosed ProxyLogon vulnerabilities in Microsoft Exchange.

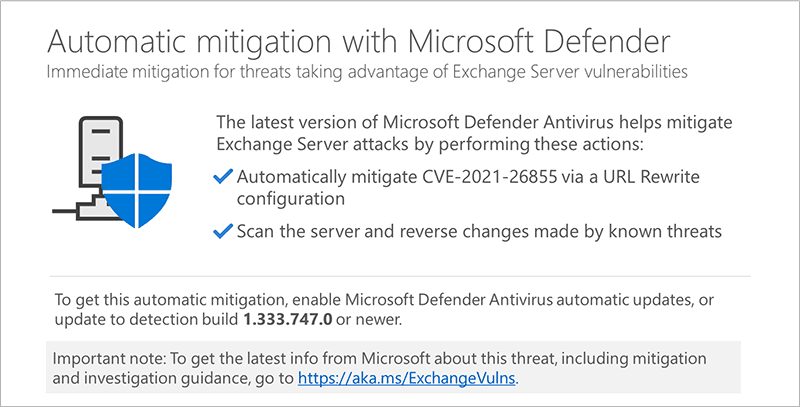
“Today, we have taken an additional step to further support our customers who are still vulnerable and have not yet implemented the complete security update. With the latest security intelligence update, Microsoft Defender Antivirus and System Center Endpoint Protection will automatically mitigate CVE-2021-26855 on any vulnerable Exchange Server on which it is deployed.” reads the announcement published by Microsoft.

Microsoft Defender

The IT giant early this month released emergency out-of-band security updates for all supported Microsoft Exchange versions that fix four zero-day flaws, a week later the company released patches for unsupported Microsoft Exchange versions.

Microsoft reported that at least one China linked APT group, tracked as HAFNIUM, chained these vulnerabilities to access on-premises Exchange servers to access email accounts, and install backdoors to maintain access to victim environments.

Microsoft also updated MSERT to detect web shells used in attacks against Microsoft Exchange installs, released IOC Detection Tool for Microsoft Exchange Server flaws, and released an Exchange On-premises Mitigation Tool (EOMT) tool to allow small businesses to quickly address the vulnerabilities exploited in the recent attacks.

Microsoft has now implemented the ProxyLogon protection in Defender Antivirus and System Center Endpoint Protection allowing to protect unpatched systems running its antimalware solution.

“Microsoft Defender Antivirus will automatically identify if a vulnerable version of Exchange Server is installed and apply the mitigations the first time the security intelligence update is deployed. The mitigation is deployed once per machine,” Microsoft added.

If you want to receive the weekly Security Affairs Newsletter for free subscribe here.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Microsoft Defender)

[adrotate banner=”5″]

[adrotate banner=”13″]


