
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Microsoft confirmed it won’t fix kernel issue that could be exploited to evade antivirus

A design flaw within the Windows kernel could be exploited by attackers to evade antivirus and stop them from recognizing malware. A design flaw within the Windows kernel is the root cause for antivirus stopping from recognizing malware, and the bad news is that Microsoft won’t fix it because the tech giant doesn’t consider it as a […]

PsSetLoadImageNotifyRoutine kernel flaw

A design flaw within the Windows kernel could be exploited by attackers to evade antivirus and stop them from recognizing malware.

A design flaw within the Windows kernel is the root cause for antivirus stopping from recognizing malware, and the bad news is that Microsoft won’t fix it because the tech giant doesn’t consider it as a security issue.

The vulnerability was discovered a few days ago by the security researcher Omri Misgav from enSilo , it affects the system call PsSetLoadImageNotifyRoutine that is still active in the latest builds of Microsoft OSs.

“During research into the Windows kernel, we came across an interesting issue with PsSetLoadImageNotifyRoutine which as its name implies, notifies of module loading.” Misgav wrote in a blog post.

Microsoft kernel issue PsSetLoadImageNotifyRoutine

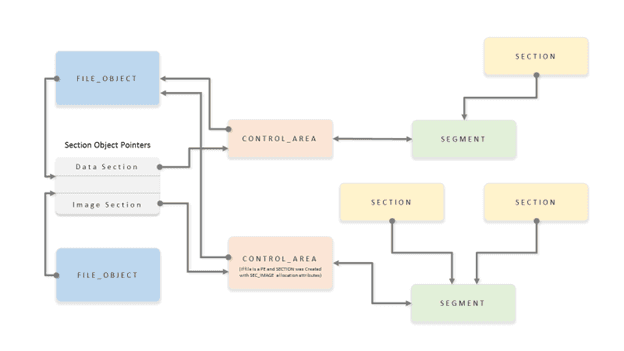
PsSetLoadImageNotifyRoutine is used also by antivirus to check the presence of malware in memory, but the issue could be tricked to deceive the defense solutions.

“The thing is, after registering a notification routine for loaded PE images with the kernel, the callback may receive invalid image names. After digging into the matter, what started as a seemingly random issue proved to originate from a coding error in the Windows kernel itself.” continues the analysis.

The mechanism notifies registered drivers when a PE image file has been loaded into virtual memory (kernel\user space).

The notification routine could be invoked in the following cases:

  • Loading drivers
  • Starting new processes
    • Process executable image
    • System DLL: ntdll.dll (2 different binaries for WoW64 processes)
  • Runtime loaded PE images – import table, LoadLibrary, LoadLibraryEx, NtMapViewOfSection.

The flaw could be exploited by malware to provide antivirus benign executables to inspect rather than their malicious code.executables to inspect rather than their malicious code.executables to inspect rather than their malicious code.

enSilo reported the issue to Microsoft and this is their reply:

“Our engineers reviewed the information and determined this does not pose a security threat and we do not plan to address it with a security update.”

[adrotate banner=”9″]adrotate banner=”9″]adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Microsoft, hacking)

[adrotate banner=”12″]adrotate banner=”12″]adrotate banner=”12″]


