
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Microsoft released out-of-band patch following Hacking Team hack

According to the security experts at FireEye, Microsoft releases out-of-band patch for all Windows version after Hacking Team hack. Microsoft released an out-of-band patch to fix a critical security issue in the Windows Adobe Type Manager Library that could be exploited by attackers to execute arbitrary code remotely on the targeted machine. The exploitation of […]

Microsoft released out-of-band patch following Hacking Team hack

According to the security experts at FireEye, Microsoft releases out-of-band patch for all Windows version after Hacking Team hack.

Microsoft released an out-of-band patch to fix a critical security issue in the Windows Adobe Type Manager Library that could be exploited by attackers to execute arbitrary code remotely on the targeted machine.

The exploitation of the flaw allows attackers gain complete control over the targeted system.

“There are multiple ways an attacker could exploit this vulnerability, such as by convincing a user to open a specially crafted document, or by convincing a user to visit an untrusted webpage that contains embedded OpenType fonts. The update addresses the vulnerability by correcting how the Windows Adobe Type Manager Library handles OpenType fonts,” states the advisory issued by Microsoft.

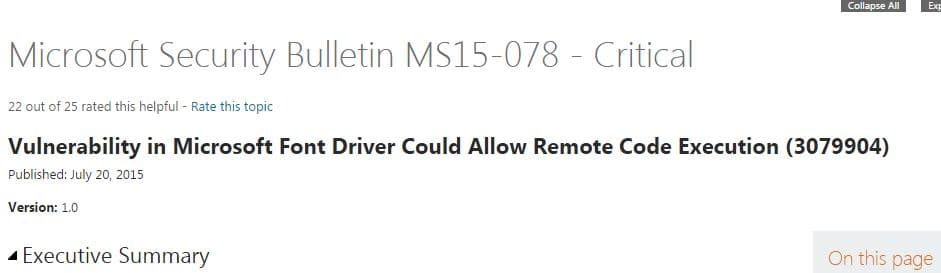
Microsoft has released security patches to fix the vulnerability (3079904) for all supported versions of the Windows OS.

Microsoft bulletin

The advisory confirms that Windows 2003 and Windows XP will not be patched against this vulnerability, only users with extended support will receive the upgrade on these OS.

According to the FireEye firm, the decision to patch all Microsoft OS is a consequence of the disclosure of the exploits used by the Hacking Team.

Pierluigi Paganini

(Security Affairs – out-of-band patch, Hacking Team)


