
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A bug in Microsoft partner portal ‘exposes ‘ support requests to all partners

A bug in Microsoft partner portal ‘exposes ‘ support requests to all partners, fortunately, no customer data was exposed. The Register in exclusive reported that Microsoft partner portal ‘exposed ‘every’ support request filed worldwide.’ Tickets submitted from all over the world were exposed to all Microsoft support partners due to the glitch. “At the moment […]

Microsoft partner

A bug in Microsoft partner portal ‘exposes ‘ support requests to all partners, fortunately, no customer data was exposed.

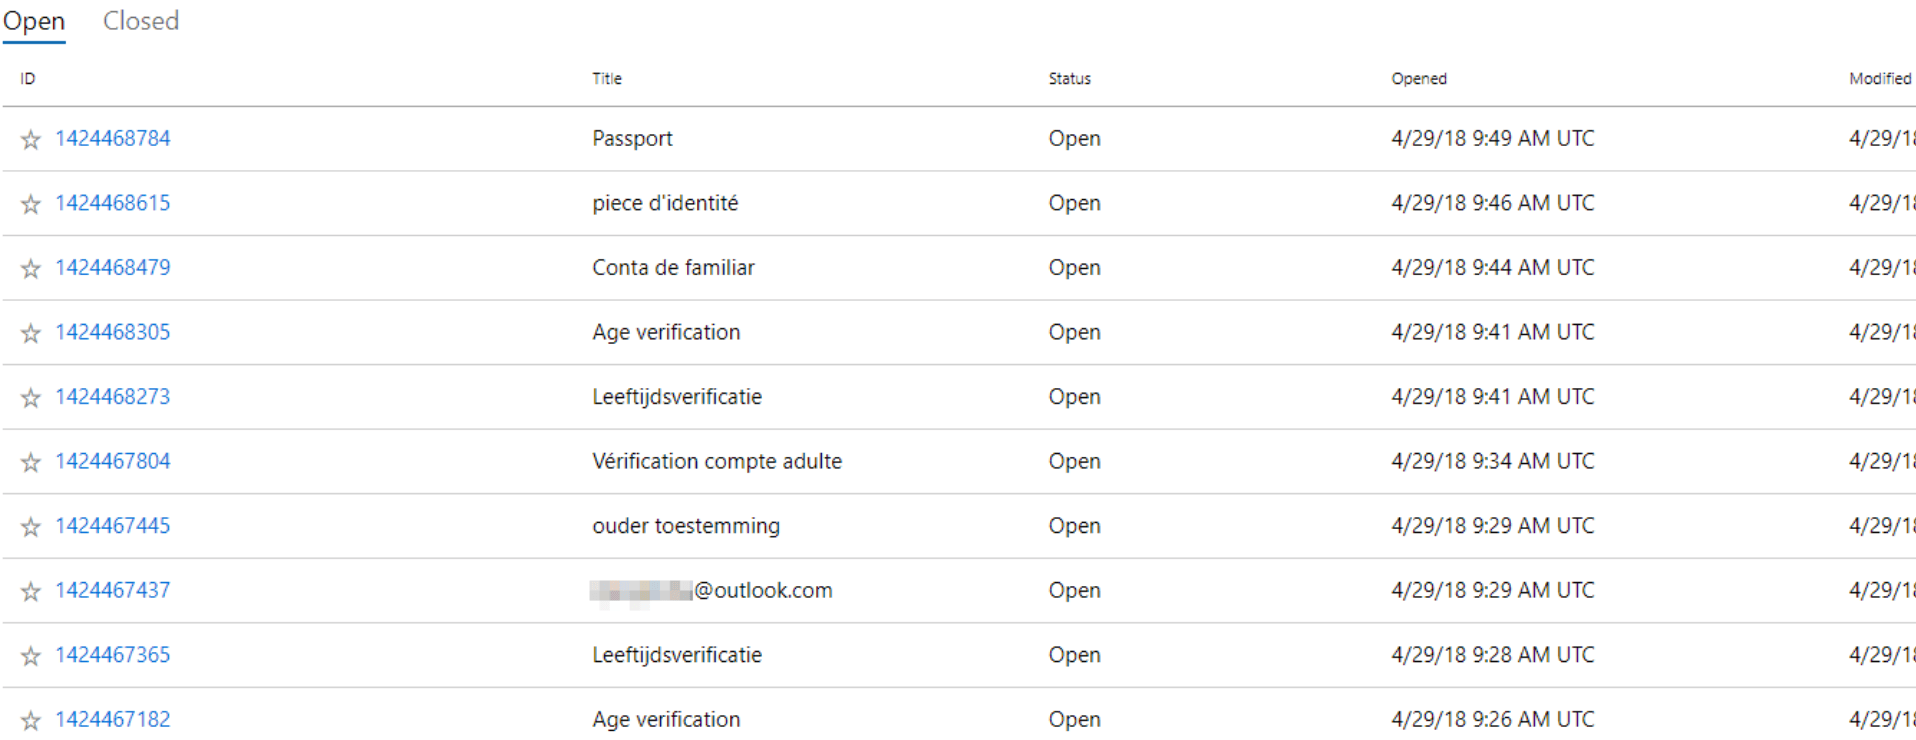
The Register in exclusive reported that Microsoft partner portal ‘exposed ‘every’ support request filed worldwide.’ Tickets submitted from all over the world were exposed to all Microsoft support partners due to the glitch.

“At the moment in the Microsoft Partner Portal you can see every ticket title for every support request worldwide!” Stuart Crane of IT biz Everon told The Register.

Microsoft partner

“Another Microsoft small biz specialist contacted us to say “Logged on to my Microsoft Partner portal to check status of a ticket I have open with them only to see lots of tickets which are not ours”.” reported The Register.

According to another Microsoft partner quoted by The Register, the bug exposed case number and title of the tickers, but not their content. This means that the problem will not cause Microsoft big problems with data protection laws or watchdogs.

Microsoft quickly addressed the flaw and downplayed the issue explaining that only a limited number of features in the Partner Centre portal were affected.

“We’ve addressed an issue that impacted a small subset of functions on our Partner Centre portal and we’re working to restore normal operation.”
said a spokesperson for Microsoft.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Microsoft partner portal, data leak)

[adrotate banner=”5″] [adrotate banner=”13″]


