
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Threat actors target poorly protected Microsoft SQL Servers

Threat actors install Cobalt Strike beacons on vulnerable Microsoft SQL Servers to achieve a foothold in the target network. Researchers from Ahn Lab’s ASEC spotted a new wave of attacks deploying Cobalt Strike beacons on vulnerable Microsoft SQL Servers to achieve initial access to target networks and deploy malicious payloads. The threat actors behind the […]

Microsoft SQL servers

Threat actors install Cobalt Strike beacons on vulnerable Microsoft SQL Servers to achieve a foothold in the target network.

Researchers from Ahn Lab’s ASEC spotted a new wave of attacks deploying Cobalt Strike beacons on vulnerable Microsoft SQL Servers to achieve initial access to target networks and deploy malicious payloads.

The threat actors behind the campaign are targeting poorly secured Microsoft SQL Servers exposed online.

The attack chain starts threat actors scanning for MS-SQL servers which have an open TCP port 1433. Then the attackers carry out brute-forcing and dictionary attacks in an attempt to crack the password.

Upon gaining access to the server, the attackers have been observed deploying crypto-currency miners such as Lemon Duck, KingMiner, and Vollgar. The attackers achieve persistence by installing the post-exploitation tool Cobalt Strike and use it for lateral movement.

“If the attacker succeeds to log in to the admin account through these processes, they use various methods including the xp_cmdshell command to execute the command in the infected system.” reads the analysis published by Ahn Lab’s ASEC. “Cobalt Strike that has recently been discovered was downloaded through cmd.exe and powershell.exe via the MS-SQL process as shown below.”

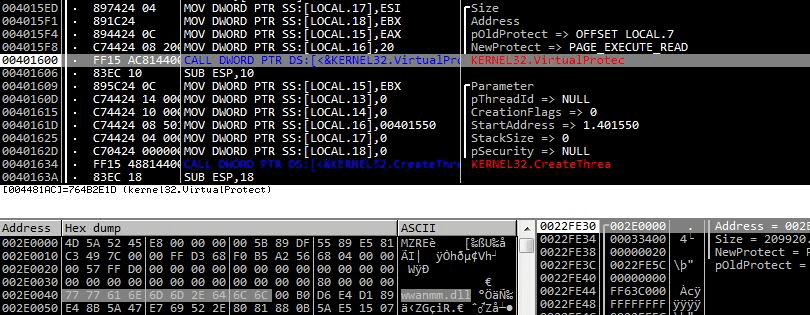
The Cobalt Strike beacon is injected into the legitimate Windows wwanmm.dll process, it waits for the commands of the attackers.

“Cobalt Strike that is executed in MSBuild.exe has an additional settings option to bypass detection of security products, where it loads the normal dll wwanmm.dll, then writes and executes a beacon in the memory area of the DLL.” continues the analysis. “As the beacon that receives the attacker’s command and performs the malicious behavior does not exist in a suspicious memory area and instead operates in the normal module wwanmm.dll, it can bypass memory-based detection.”

MS-SQL Servers beacon injection

At this, it is unclear how attackers installed the malware on the compromised MS-SQL

Although it is not certain in which method the attacker dominated MS-SQL and installed the malware, experts believe that the targeted system had inappropriately managed the account credentials.

AhnLab’s published Indicators of Compromise for these attacks, including download URLs, MD5 hashes for the beacons, and C2 server URLs.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Microsoft SQL Servers)

[adrotate banner=”5″]

[adrotate banner=”13″]


