
Chaos Ransomware operators target gamers’ Windows devices using Minecraft alt lists as a lure and promoting them on gaming forums.
Minecraft is one of the most popular games in the world, it had more than 140 million monthly active players in August 2021. Cybercriminals are attempting to exploit this popularity, the Chaos Ransomware gang is targeting Japanese gamers’ Windows devices through fake Minecraft alt lists promoted on gaming forums.
FortiGuard Labs researchers who reported the attacks noticed that the variant of ransomware employed in the attacks not only encrypts certain files but also destroys others.
“FortiGuard Labs recently discovered a variant of the Chaos ransomware that appears to target Minecraft gamers in Japan. This variant not only encrypts certain files but also destroys others, rendering them unrecoverable. If gamers fall prey to the attack, choosing to pay the ransom may still lead to a loss of data. In this report we will take a look at how this new ransomware variant works.” reads the analysis published by the experts.
Alternative accounts, so-called ‘Alts,’ are created by Minecraft gamers for various purposes such as antagonizing/trolling other players, providing cover for an alternative in-game identity/personality, or to avoid getting their main account banned for using cheats.
Alt lists shared on Minecraft online forums often contain stolen accounts used by gamers for the above purposes.
The variant of Chaos ransomware spotted by the researchers was hidden in a file pretending to contain a list of “Minecraft Alt” accounts.
“In this case, the file is an executable, but it uses a text icon to fool potential victims into thinking it is a text file full of compromised usernames and passwords for Minecraft. While we don’t know how this specific fake list is being distributed, it’s a safe guess that the file is being advertised on Minecraft forums for Japanese gamers.” continues Fortinet.
Upon opening the executable file, the malware will be executed and will search for files smaller than 2,117,152 bytes on the compromised machine to encrypt them. The ransomware appends four random characters, chosen from “abcdefghijklmnopqrstuvwxyz1234567890,” to the filename of the encrypted files.
Files larger than 2,117,152 bytes with specified file extensions are filled with random bytes making it impossible to recover them without paying the ransom. Like other ransomware, this variant of the Chaos ransomware also deletes shadow copies from the compromised machines.
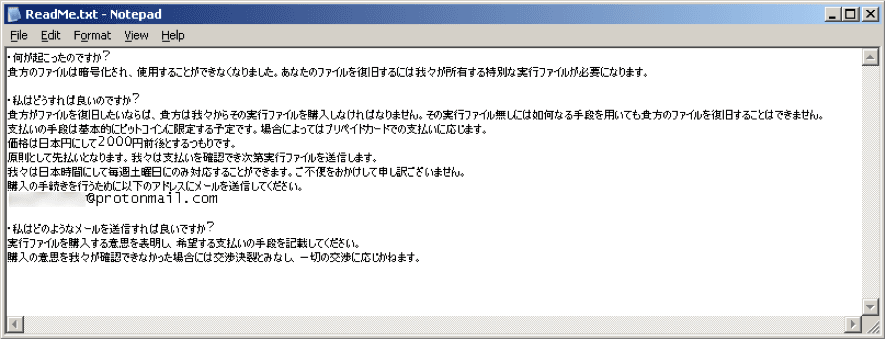
The gang is demanding 2,000 yen (~$17.56) worth of Bitcoin or in pre-paid cards.
The ransom note (ReadMe.txt) dropped on the infected systems does not specify which type of pre-paid card could be used to pay the ransom, all kinds of pre-paid cards (online shopping, gaming, music, mobile phone charge and online streaming services) should be ok.

The ransom note, which is written in Japanese language, also states that the attacker can only be reached on Saturdays and apologizes for any inconvenience caused.
“There is nothing fancy about this Chaos ransomware variant nor its infection vector. However, despite its cheap ransom demand, its ability to destroy data and render it unrecoverable makes it more than a mere prank to annoy Japanese Minecraft gamers. Ransomware is still ransomware, and in this case, the victim may not be able to get their original files back, with or without making a ransom payment.” concludes Fortinet. “The best advice is for players to stay off suspicious gaming cheat sites and simply enjoy the game the way it was meant to be played.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Minecraft)
[adrotate banner=”5″]
[adrotate banner=”13″]


