
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

MITRE adds D3FEND defensive cybersecurity techniques to ATT&CK Framework

D3FEND is a new project promoted by MITRE Corporation to add defensive cybersecurity techniques to the ATT&CK Framework. D3FEND is a new project promoted by MITRE Corporation aimed to add a knowledge graph of cybersecurity countermeasures to the ATT&CK Framework. The project was announced this week by the U.S. National Security Agency (NSA), it proposes […]

D3FEND

D3FEND is a new project promoted by MITRE Corporation to add defensive cybersecurity techniques to the ATT&CK Framework.

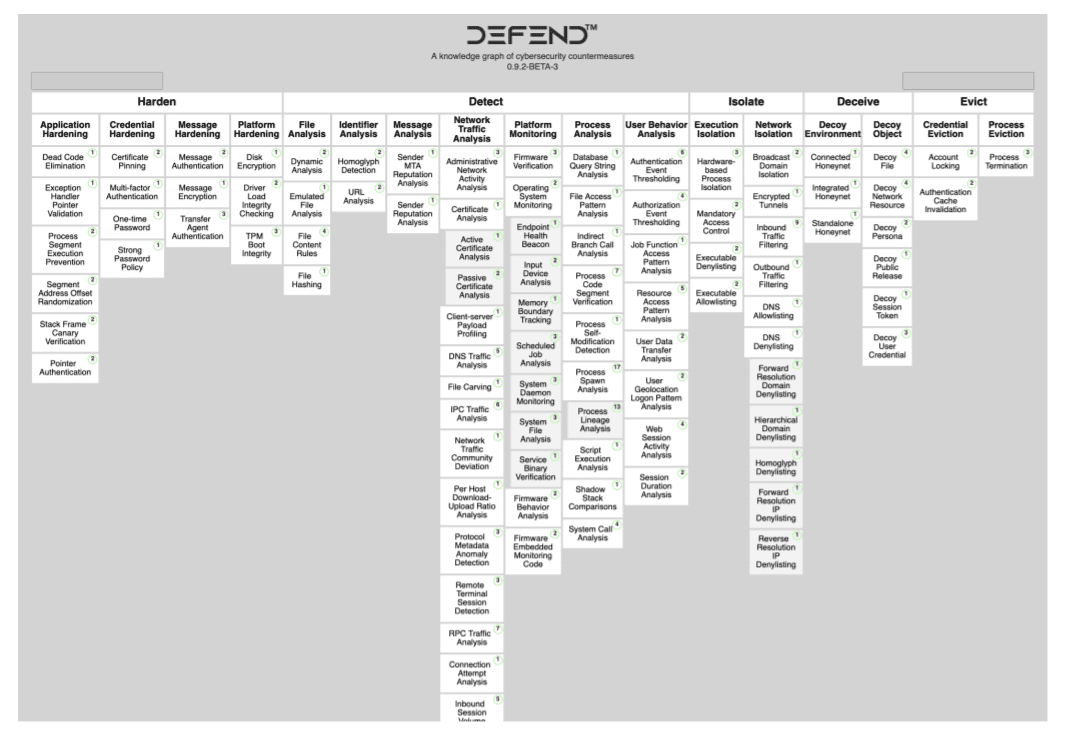
D3FEND is a new project promoted by MITRE Corporation aimed to add a knowledge graph of cybersecurity countermeasures to the ATT&CK Framework.

The project was announced this week by the U.S. National Security Agency (NSA), it proposes a standard approach for the description of defensive cybersecurity countermeasures for techniques used by threat actors.

“D3FEND is a knowledge base, but more specifically a knowledge graph, of cybersecurity countermeasure techniques. In the simplest sense, it is a catalog of defensive cybersecurity techniques and their relationships to offensive/adversary techniques.” reads the project page published by MITRE. “The primary goal of the initial D3FEND release is to help standardize the vocabulary used to describe defensive cybersecurity technology functionality.”

The NSA announced that the D3FEND project establishes terminology of computer network defensive techniques and shed the light previously unspecified relationships between defensive and offensive methods. 

The US intelligence agency initially funded the project to improve the cybersecurity of National Security Systems, the Department of Defense, and the Defense Industrial Base.

“D3FEND establishes terminology of computer network defensive techniques and illuminates previously-unspecified relationships between defensive and offensive methods. This framework illustrates the complex interplay between computer network architectures, threats, and cyber countermeasures.” states the NSA.

“MITRE released D3FEND as a complement to its existing ATT&CK framework, a free, globally-accessible knowledge base of cyber adversary tactics and techniques based on real-world observations. Industry and government use ATT&CK as a foundation to develop specific cyber threat models and methodologies.”

D3FEND

The NSA believes that D3FEND will drive more effective design, deployment, and defense of networked systems.

MITRE experts also published a research paper that describes their study and development
toward a precise, unambiguous, and information-dense knowledge graph of cybersecurity countermeasures.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, D3FEND)

[adrotate banner=”5″]

[adrotate banner=”13″]


