
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

MongoDB investigates a cyberattack, customer data exposed

MongoDB on Saturday announced it is investigating a cyberattack that exposed customer account metadata and contact information. MongoDB on Saturday disclosed it is investigating a cyber attack against certain corporate systems. MongoDB is a US company that developed the popular open-source NoSQL database management system. The cyber attack was discovered on December 13, 2023, and […]

MongoDB

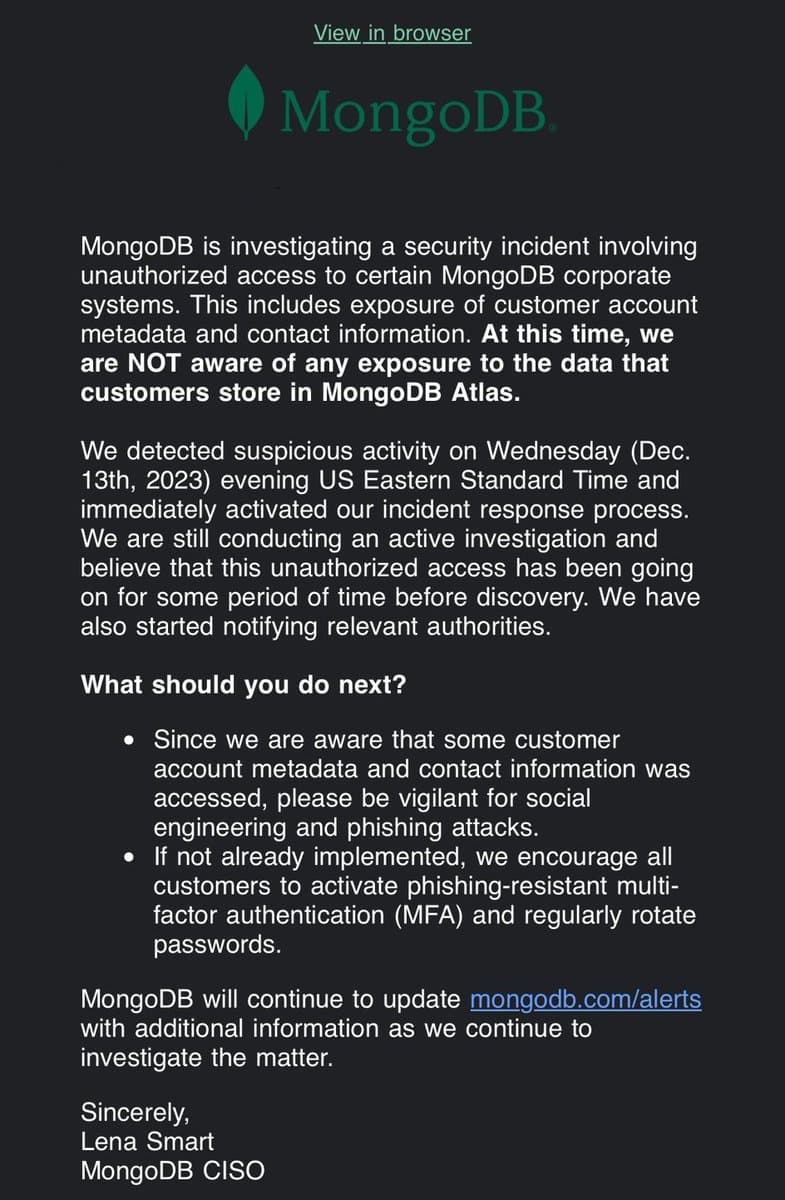
MongoDB on Saturday announced it is investigating a cyberattack that exposed customer account metadata and contact information.

MongoDB on Saturday disclosed it is investigating a cyber attack against certain corporate systems.

MongoDB is a US company that developed the popular open-source NoSQL database management system.

The cyber attack was discovered on December 13, 2023, and led to the exposure of customer account metadata and contact information. The American company promptly started its incident response plan and pointed out that it is not aware of any data exposure.

“MongoDB is actively investigating a security incident involving unauthorized access to certain MongoDB corporate systems, which includes exposure of customer account metadata and contact information. We detected suspicious activity on Wednesday (Dec. 13th, 2023) evening US Eastern Standard Time, immediately activated our incident response process, and believe that this unauthorized access has been going on for some period of time before discovery.” reads the alert published by the company.” At this time, we are not aware of any exposure to the data that customers store in MongoDB Atlas.” 

The US firm urges customers to be vigilant for social engineering and phishing attacks. The company also recommends active multi-factor authentication (MFA), and regularly rotate their MongoDB Atlas passwords.

At this time it is still unclear how long threat actors maintained access to the compromised systems.

In an update provided by the company on December 16, MongoDB disclosed it is experiencing a spike in login attempts resulting in issues for customers attempting to log in to Atlas and our Support Portal. However, the company states that the activity is not related to the security incident.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, data breach)


