
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

MonitorMinor, the outstanding stalkerware can track Gmail, WhatsApp, Instagram, and Facebook

Security experts spotted a new stalkerware, dubbed MonitorMinor, that can track Gmail, WhatsApp, Instagram, and Facebook user activity. Security experts from Kaspersky Lab spotted a new stalkerware, dubbed MonitorMinor (Monitor.AndroidOS.MonitorMinor.c), that can track Gmail, WhatsApp, Instagram, and Facebook user activity. Stalkerware is commercial monitoring software or spyware that is used for stalking, it is usually […]

monitorminor super-stalker-1

Security experts spotted a new stalkerware, dubbed MonitorMinor, that can track Gmail, WhatsApp, Instagram, and Facebook user activity.

Security experts from Kaspersky Lab spotted a new stalkerware, dubbed MonitorMinor (Monitor.AndroidOS.MonitorMinor.c), that can track Gmail, WhatsApp, Instagram, and Facebook user activity.

Stalkerware is commercial monitoring software or spyware that is used for stalking, it is usually used to secretly spy on family members or colleagues.

According to the experts, MonitorMinor is more powerful than all existing software of its family.

Stalkerware are able to gather the victim’s current geolocation, to intercept SMS and call data, and sometimes implements geofencing features,

MonitorMinor outstands because it also allows spying on other communication channels such as instant messaging applications.

The sample we found (assigned the verdict Monitor.AndroidOS.MonitorMinor.c) is a rare piece of stalkerware that can do this.

Experts discovered that the author of the stalkerware leverage the presence of the SuperUser-type app (SU utility) which grants root access to the system.

“In a “clean” Android operating system, direct communication between apps is prevented by the sandbox, so stalkerware cannot simply turn up and gain access to, say, WhatsApp messages. This access model is called DAC (Discretionary Access Control).” reads the report published by Kaspersky.

“The situation changes if a SuperUser-type app (SU utility) is installed, which grants root access to the system.” “It is the presence of this utility that the creators of MonitorMinor are counting on.”

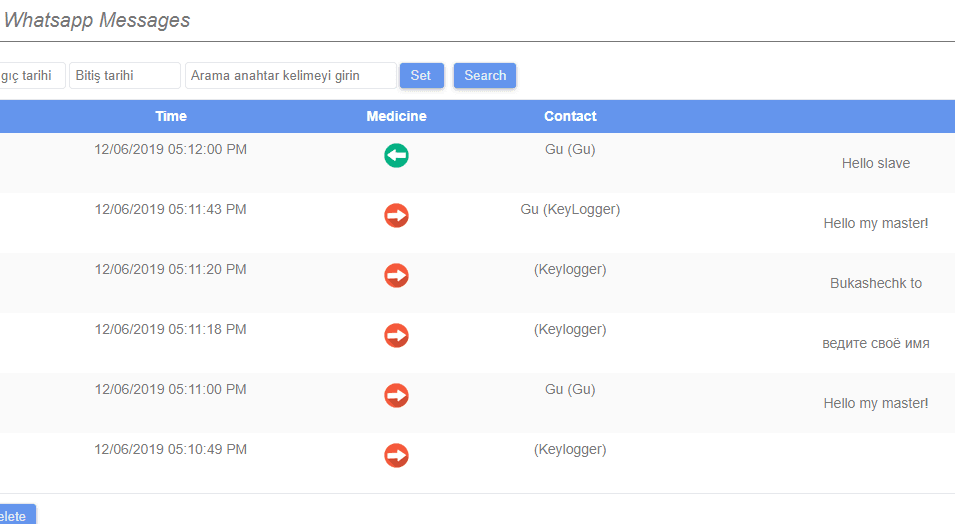
Once escalated privileges by running the SU utility, the malware gains full access to data in the following apps:

  • LINE: Free Calls & Messages
  • Gmail
  • Zalo – Video Call
  • Instagram
  • Facebook
  • Kik
  • Hangouts
  • Viber
  • Hike News & Content
  • Skype
  • Snapchat
  • JusTalk
  • BOTIM

MonitorMinor is also able to extract the file /data/system/gesture.key from the device, which contains the hash sum for the screen unlock pattern or the password. MonitorMinor operator could use it to unlock the device, this is the first stalkerware that implements such a function.

The persistence mechanism implemented by the malware is very efficient and leverages the root access. The stalkerware remounts the system partition from read-only to read/write mode, then copies itself to it, deletes itself from the user partition, and remounts it back to read-only mode.

Victims will not able to remove the spying software using regular OS tools.

MonitorMinor leverages the Accessibility Services API to intercept events in the controlled apps, even without root access it is able to operate effectively on all devices with this API.

The malware also implements a keylogger through this API, it also allows operators to monitor the clipboard and forwards the contents.

The stalkerware also allows its owner to:

  • Control the device using SMS commands
  • View real-time video from the device’s cameras
  • Record sound from the device’s microphone
  • View browsing history in Chrome
  • View usage statistics for certain apps
  • View the contents of the device’s internal storage
  • View the contacts list
  • View the system log

According to Kaspersky most of the installs of this stalkerware are in India (14.71%), followed by Mexico (11.76%), Germany, Saudi Arabia, and the UK (5.88%). Experts also noticed the presence of a Gmail account with an Indian name is into the body of MonitorMinor, a circumstance that suggests it was developed by an Indian developer.

“MonitorMinor is superior to other stalkerware in many aspects. It implements all kinds of tracking features, some of which are unique, and is almost impossible to detect on the victim’s device.” concludes Kaspersky. “If the device has root access, its operator has even more options available.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – MonitorMinor, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


