
The ICS-CERT has published two security advisories to describe a number of flaws in surveillance products from Moxa and Vanderbilt firms.
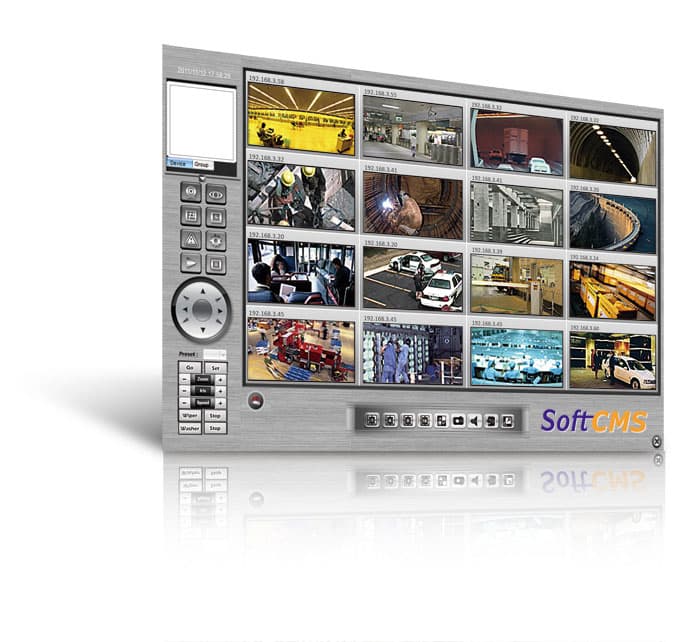
Surveillance systems produced by Moxa SoftCMS and IP cameras manufactured by Vanderbilt are affected by serious vulnerabilities that can be exploited by remote attackers to obtain full control of flawed systems.
The ICS-CERT has published a security advisory to describe three serious vulnerabilities in the central management software Moxa SoftCMS Webserver Application.

Zhou Yu working with Trend Micro’s Zero Day Initiative and Gu Ziqiang from Huawei Weiran Labs been credited for finding the security vulnerabilities in the Moxa SoftCMS.
One of the flaw was rated with a 9.8 CVSS score, it is a SQL injection flaw tracked as CVE-2016-9333 that can be exploited by a remote attacker to access SoftCMS with administrator privileges.
“The SoftCMS Application does not properly sanitize input that may allow a remote attacker access to SoftCMS with administrator’s privilege through specially crafted input.” reads the advisory.
A second vulnerability, tracked as CVE-2016-8360, is a double free condition that could be exploited to cause a denial-of-service (DoS) and in some cases even execute arbitrary code.
“A specially crafted URL request sent to the SoftCMS ASP Webserver can cause a double free condition on the server allowing an attacker to modify memory locations and possibly cause a denial of service or the execution of arbitrary code.” continues the advisory.
The third vulnerability, tracked as CVE-2016-9332, is an improper input validation issue that can lead to a crash of the application.
“Moxa SoftCMS Webserver does not properly validate input. An attacker could provide unexpected values and cause the program to crash or excessive consumption of resources could result in a denial-of-service condition.” states the advisory.
According to the ICS-CERT, Moxa fixed all the vulnerabilities in the latest SoftCMS 1.6 release, but the release notes suggest that only the SQL Injection has been fixed.
Similar problems also for the CCTV IP cameras manufactured by Vanderbilt.
According to the ICS-CERT, a vulnerability (CVE-2016-9155) in the IP cameras could be exploited by attackers with network access to obtain administrative credentials using specially crafted requests.
“An attacker with network access to the web server could obtain administrative credentials by sending certain requests.” reads the ICS-CERT advisory.
Vanderbilt has already released security updates for all the affected products.
[adrotate banner=”9″]
(Security Affairs – Moxa SoftCMS, Vanderbilt)


