
Multinational IT corporation MSI (Micro-Star International) confirms security breach after Money Message ransomware gang claimed the hack.
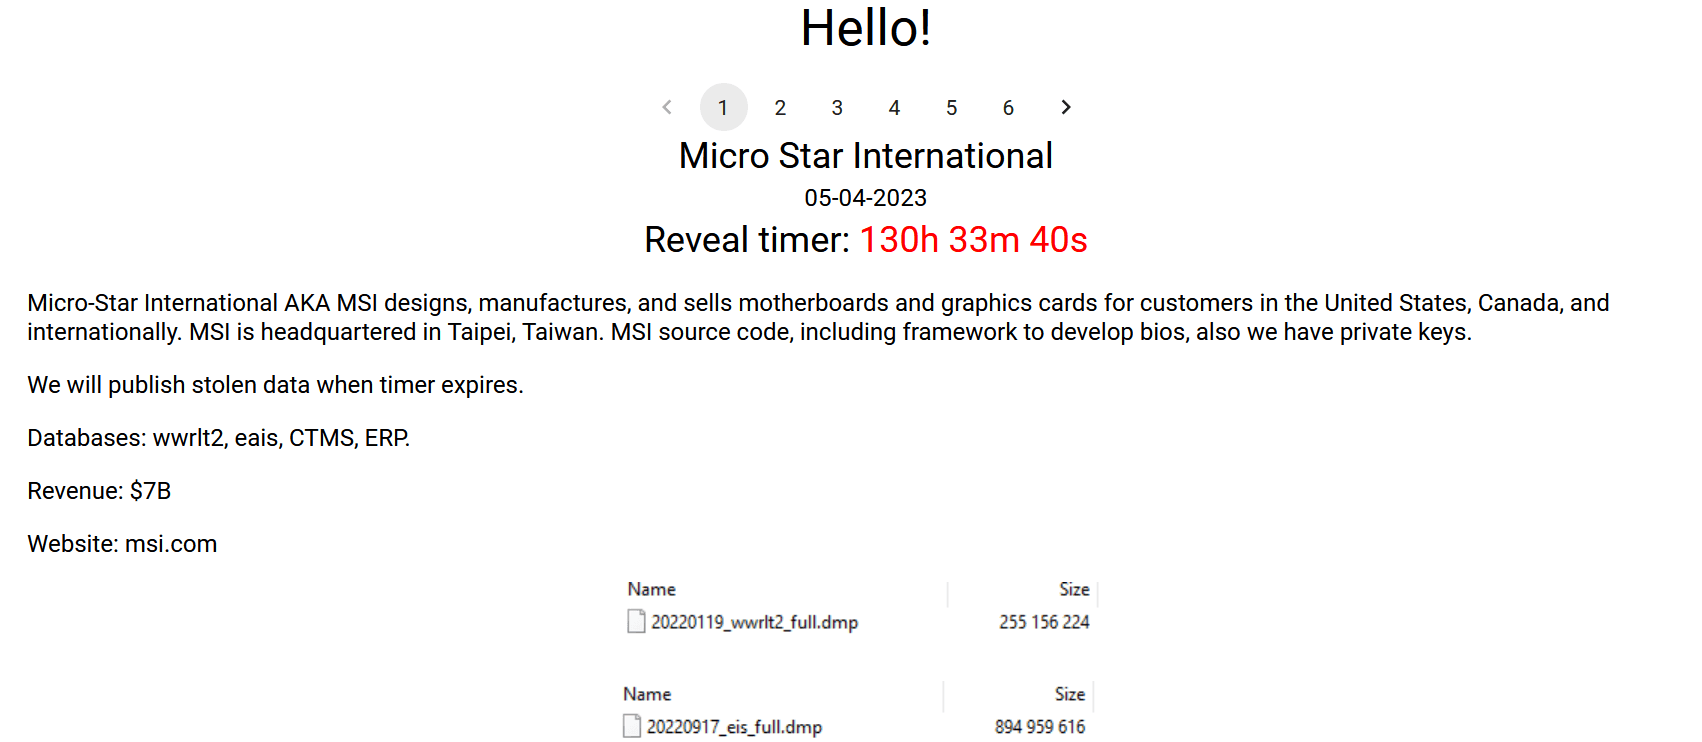
This week the ransomware gang Money Message announced to have hacked the Taiwanese multinational IT corporation MSI (Micro-Star International). Micro-Star International AKA MSI designs, manufactures, and sells motherboards and graphics cards for customers in the United States, Canada, and internationally. MSI is headquartered in Taipei, Taiwan.
The ransomware group added the company to the list of victims on its Tor leak site, it claims to have stolen the source code from the company, including a framework to develop bios, and private keys.

The group published a series of screenshots of the company’s CTMS and ERP databases
The Money Message group threatens to publish the stolen files by Wednesday, April 12, 2023, if the company will not pay the ransom.
Today MSI confirmed the security breach, it confirmed that threat actors had access to some of its information service systems.
“MSI recently suffered a cyberattack on part of its information systems. Upon detecting network anomalies, the information department promptly activated relevant defense mechanisms and carried out recovery measures, and reported the incident to government law enforcement agencies and cybersecurity units.” reads a statement published by the company. “Currently, the affected systems have gradually resumed normal operations, with no significant impact on financial business.”
The company reported the security breach to the relevant authorities, and it downplayed the incident, saying that the attack had no significant financial and operational impact.
In response to the incident, the company announced it is enhancing the information security control measures of its network and infrastructure.
MSI is urging users to obtain firmware/BIOS updates only from its official website fearing that threat actors could circulate malware-laced versions of the company’s BIOS.
BleepingComputer first reported that the ransomware gang claimed the theft of 1.5TB of internal files and has demanded a ransom payment of $4,000,000.
Please vote for Security Affairs (https://securityaffairs.com/) as the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections:
- The Teacher – Most Educational Blog
- The Entertainer – Most Entertaining Blog
- The Tech Whizz – Best Technical Blog
- Best Social Media Account to Follow (@securityaffairs)
Please nominate Security Affairs as your favorite blog.
Nominate here: https://docs.google.com/forms/d/e/1FAIpQLSfaFMkrMlrLhOBsRPKdv56Y4HgC88Bcji4V7OCxCm_OmyPoLw/viewform
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, MSI)


