
Experts spotted a previously undetected backdoor, dubbed Msupedge, that was employed in an attack against a university in Taiwan.
Broadcom Symantec researchers discovered a previously undetected backdoor, called Msupedge, that was employed in an attack targeting an unnamed university in Taiwan.
The most notable feature of the backdoor is that it relies on DNS tunnelling to communicate with a C2 server.

“Msupedge is a backdoor in the form of a dynamic link library (DLL).” reads the report published by Symantec. “It has been found installed in the following file paths:
- csidl_drive_fixed\xampp\wuplog.dll
- csidl_system\wbem\wmiclnt.dll
While wuplog.dll is loaded by Apache (httpd.exe), the parent process for wmiclnt.dll is unknown.”
The code used by Msupedge for the DNS tunneling tool is based on the publicly available dnscat2 tool.
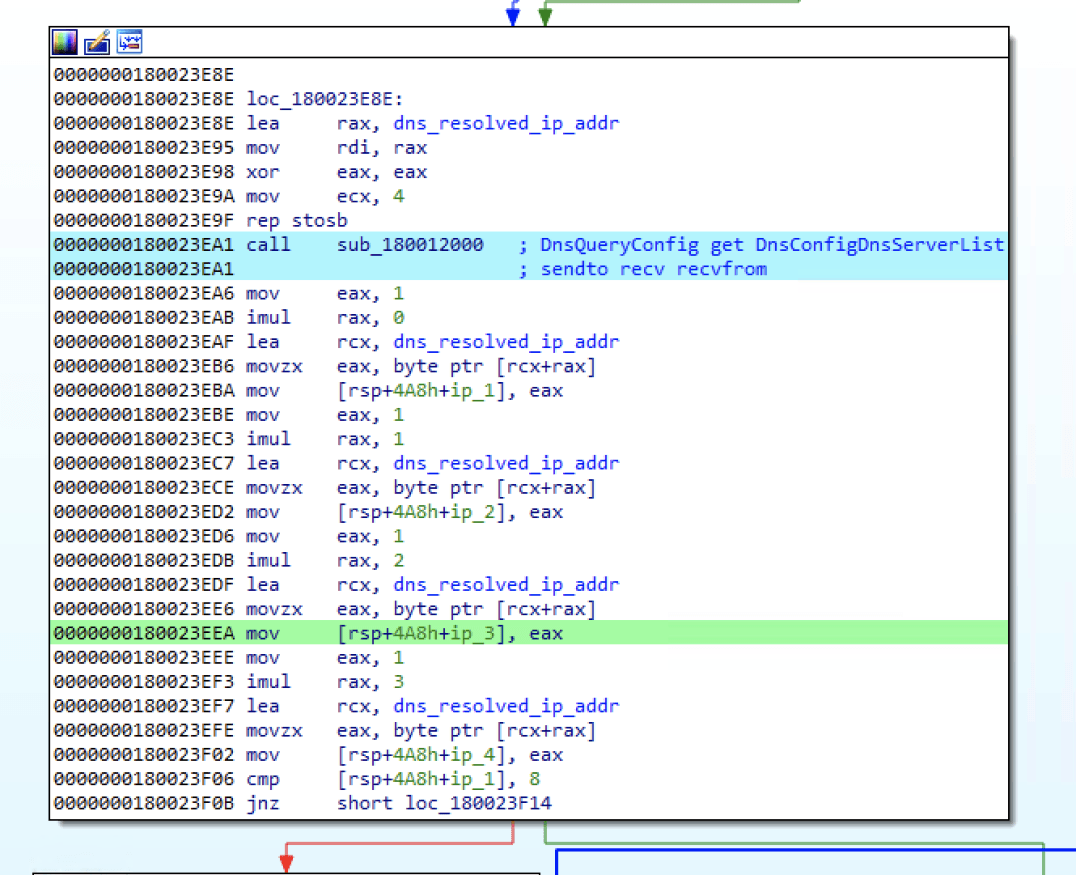
The backdoor receives and executes commands by resolving specially structured host names. The results of these commands are encoded and sent back as a fifth-level domain. Additionally, the backdoor interprets the third octet of the resolved IP address of the C&C server as a command switch, adjusting its behavior based on this value. Error notifications for memory allocation, command decompression, and execution are also sent through this method.
Threat actors were observed exploiting a critical vulnerability in PHP, tracked as CVE-2024-4577 (CVSS score of 9.8), to deploy the Msupedge backdoor. Attackers exploited this flaw to achieve remote code execution and gain initial access to the target network.
The backdoor supports the following commands:
- Case 0x8a : Create process. The command is receive via DNS TXT record.
- Case 0x75 : Download file. The download URL is received via DNS TXT record.
- Case 0x24 : Sleep (ip_4 * 86400 * 1000 ms).
- Case 0x66 : Sleep (ip_4 * 3600 * 1000 ms).
- Case 0x38 : Create %temp%\1e5bf625-1678-zzcv-90b1-199aa47c345.tmp. The purpose of this file is unknown.
- Case 0x3c: Remove %temp%\1e5bf625-1678-zzcv-90b1-199aa47c345.tmp.
Symantec did not attribute the attack to a specific threat actors and has yet to determine the motive behind the attack.
“Symantec has seen multiple threat actors scanning for vulnerable systems in recent weeks. To date, we have found no evidence allowing us to attribute this threat and the motive behind the attack remains unknown.” concludes the report that includes Indicators of Compromise.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware)


