
Experts spotted a new signed Mac adware dubbed MUGHTHESEC that hijacks victim’s browser for profit and can be removed only reinstalling the OS.
According to the expert Patrick Wardle, Director of Research at Synack, a new strain of Mac adware is threatening Mac users, once infected a machine the only way to remove it is to reinstall the macOS.
The researcher and Mac expert Thomas Reed, speculate the new family of Mac adware dubbed Mughthesec is an improved version of the well known OperatorMac family.
Thanks, Patrick sent me the hash too. Looks like a new variant of something we call OperatorMac (though that may be a bad name).
— Thomas Reed (@thomasareed) August 8, 2017
The Mac Malware has been improved across the months, new features were implemented such as an MAC-address-based anti-VM detection system and components of Mughthesec are signed with a legitimate Apple developer certificate allowing it to bypass the Gatekeeper protection that normally prevents the installation of unsigned applications.
“In a nutshell, I think the issue isn’t that anything here is incredible new or exciting; more that existing security/mitigation strategies are rather failing miserably,” Wardle explained. “So we’ve got Gatekeeper that’s designed to block unsigned code from the internet to prevent users from getting tricked into installing malware (e.g. fake flash updaters)….which is a great idea. But now most Mac adware/malware is just signed with certs. So gatekeeper is basically a moot point. Normal-everyday users are still going to go around infecting themselves…and things designed to protect them; Gatekeeper/AV etc, really don’t offer any help.”
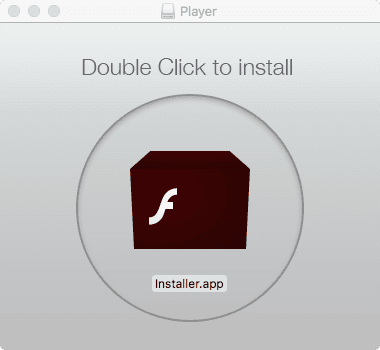
The adware is currently delivered as a file called Player.dmg that installs a legitimate version of the Adobe Flash Player for Mac, but also an unwanted app named Advanced Mac Cleaner, and two Safari extensions named Safe Finder and Booking.com.
“The PUPs are in my opinion, rather shady. I mean they automatically install browser plugins circumventing Apple’s security mechanisms in Safari,” Wardle said. “So sure, they ask for user permission to be installed during install, but then do things that generally the user probably doesn’t want. It’s that gray area between legit code and malware.”

Patrick Wardle believes the malware is spread via malvertising campaigns or via malicious ads and popups on shady websites. “Either way, user-interaction is likely required [for both the download and installation],” says Wardle.
Speaking of infection, due to the fact that the installer is masquerading as Flash Player installer, it’s likely that this adware is relying on common infection techniques to gain new victims. If I had to guess its infection vector is likely one (or all?) of the following:
- fake popups on ‘shady’ websites
- malicious ads, perhaps on legit websites.
Either way, user-interaction is likely required. “
The malware, once installed, hijacks the victim’s browser for profit.
“A common tactic of adware is to hijack the victim’s browser (homepage, inject ads, etc) for financial gain,” Wardle said. “Mughthesec (which is installed when the user ‘agrees’ to install ‘Safe Finder’) appears to conform to goal.”
“If we open Safari; indeed the home page has been hijacked–though in a seemingly innocuous way,” Wardle said, adding that he did not test the sample on Google’s Chrome browser. “It simply displays a rather ‘clean’ search page—though looking at the source, we can see the inclusion of several scripts ‘Safe Finder’ scripts.”
Wardle highlighted that other files dropped by the adware on infected hosts allow the malware operator to drop other malicious payloads.
The presence of the Mughthesec infection must alert Mac users that will never know if other malware has been installed by crooks along with the adware, and for this reason, they should reinstall their Mac.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Mac malware, Mughthesec )
[adrotate banner=”13″]


