
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Nemty ransomware operators launch their data leak site

The operators behind the Nemty ransomware set up a data leak site to publish the data of the victims who refuse to pay ransoms. Nemty ransomware first appeared on the threat landscape in August 2019, the name of the malware comes after the extension it adds to the encrypted file names. The ransomware deletes shadow copies of encrypted files […]

Nemty ransomware

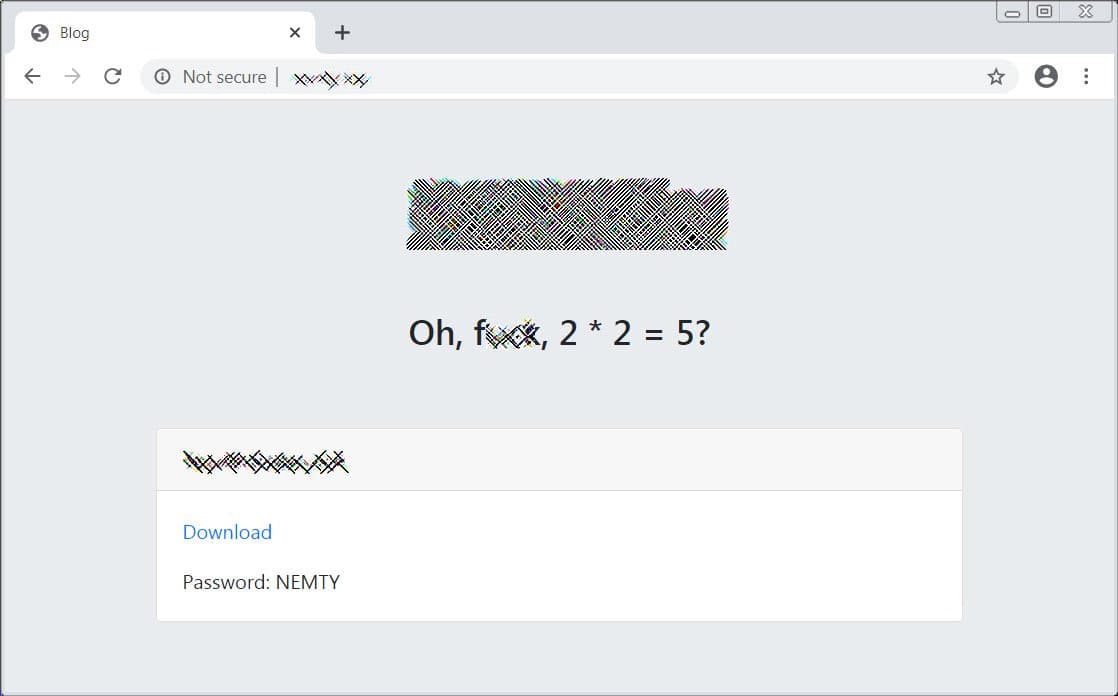
The operators behind the Nemty ransomware set up a data leak site to publish the data of the victims who refuse to pay ransoms.

Nemty ransomware first appeared on the threat landscape in August 2019, the name of the malware comes after the extension it adds to the encrypted file names. The ransomware deletes shadow copies of encrypted files to make in impossible any recovery procedure.

In October 2019, researchers from the security firm Tesorion developed a decryptor tool that works on Nemty versions 1.4 and 1.6, they also announced a working tool for version 1.5.

In February, Nemty ransomware operators announced that they will set up a website to leak the data stolen from ransomware victims who refused to pay the ransom.

The operators behind the Nemty ransomware have maintained their promise and set up the data leak site following the dangerous trend begun at the end of 2019 by the Maze ransomware gang.

BleepingComputer first reported the news citing the malware analyst Damien as source.

Nemty ransomware

This web site currently only includes links to 3.5 Gigabytes of data allegedly stolen from an American footwear company.

Other cyber crime gangs adopted the same strategy to force victims to pay the ransom, including DoppelPaymer and Sodinokibi crews.

A few days ago, the operators behind Sodinokibi Ransomware have published the download links to archives containing data allegedly stolen from the US firm Kenneth Cole Productions.

The Sodinokibi ransomware operators claim to have stolen over 70,000 documents with financial and work data, and more than 60,000 records of company customers.

The Sodinokibi gang requested the payment of a ransom and threatens to leak online the full dump containing stolen data in case the company will decide to not meet the request.

The news was first reported by the Under the Breach research group.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Nemty ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


