
A Mexican threat actor that goes online with the moniker Neo_Net is behind an Android malware campaign targeting banks worldwide.
A joint study conducted by vx-underground and SentinelOne recently revealed that a Mexican threat actor that goes online with the moniker Neo_Net is behind an Android malware campaign targeting financial institutions worldwide.
The case was reported by security researcher Pol Thill.
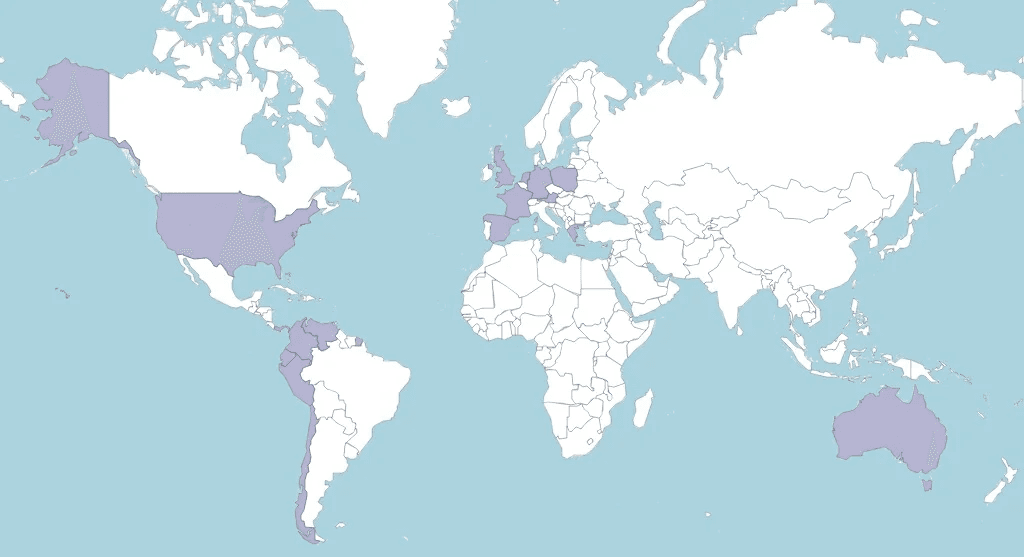
Neo_Net’s eCrime campaign was reportedly targeting clients of banks globally, with a focus on Spanish and Chilean banks, from June 2021 to April 2023. The threat actor uses relatively unsophisticated tools, but experts speculate that the reason behind the success of this campaign is the capability of tailoring the attack infrastructure to specific targets.
It has been estimated that the threat actor has stolen over 350,000 EUR from victims’ bank accounts and compromised Personally Identifiable Information (PII) of thousands of victims.
“The campaign employs a multi-stage attack strategy, starting with targeted SMS phishing messages distributed across Spain and other countries, using Sender IDs (SIDs) to create an illusion of authenticity and mimicking reputable financial institutions to deceive victims.” Thill explained.
“Neo_Net has established and rented out a wide-ranging infrastructure, including phishing panels and Android trojans, to multiple affiliates, sold compromised victim data to third parties, and launched a successful Smishing-as-a-Service offering targeting various countries worldwide.”
30 out of 50 targeted financial institutions are located in Spain or Chile, the list of targets includes Santander, BBVA and CaixaBank. The threat actor also targeted banks in other regions, including Deutsche Bank, Crédit Agricole and ING.
Neo_Net has set up and rented out a wide-ranging infrastructure, including phishing panels, Smishing software, and Android trojans to its network of affiliates. The criminal also sold stolen victim data and has launched a successful Smishing-as-a-Service named Ankarex. The Ankarex platform was launched in May 2022 and has about 1,700 subscribers. The threat actor advertises the Smishing-as-a-Service platform on Telegram.

The campaign employed a sophisticated multi-stage attack chain that commenced with SMS phishing messages distributed across Spain using Ankarex. The messages were crafted using Sender IDs (SIDs) to trick recipients into believing that they are authentic, and mimicking reputable financial institutions.
“The phishing pages were meticulously set up using Neo_Net’s panels, PRIV8, and implemented multiple defense measures, including blocking requests from non-mobile user agents and concealing the pages from bots and network scanners. These pages were designed to closely resemble genuine banking applications, complete with animations to create a convincing façade” continues the report.

The threat actor employed various techniques to circumvent the Multi-Factor Authentication (MFA), including social engineering to trick victims into installing a purported security application for their bank account on their Android devices.
The malicious apps are used to capture SMSs containing authorization codes.
“The success of their campaigns can be attributed to the highly targeted nature of their operations, often focusing on a single bank, and copying their communications to impersonate bank agents. Furthermore, due to the simplicity of SMS spyware, it can be difficult to detect, as it only requires permission to send and view SMS messages.” concludes the report that also provides indicators of compromise (IoCs) for this campaign.
“Neo_Net has also been observed reusing compromised PII for further profit.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, cybercrime)


