
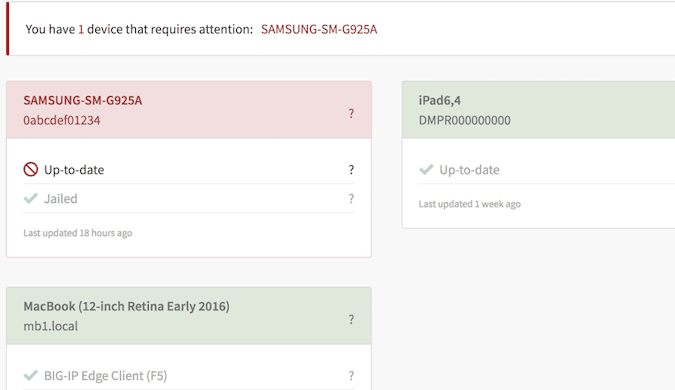
Netflix has released the Stethoscope open source web application that provides recommendations for securing their devices.
Netflix has released Stethoscope, an open source web application that provides recommendations for securing computers, smartphones, and tablets.
Netflix intends to follow a “user focused security” approach that aims to provide employees information to improve their security posture, rather than relying on the enforcement of mandatory policies.
The vast majority of attacks against business targets corporate users causing security incidents and data breaches. The humans are the weakest link in the security chain, for this reason, Netflix decided to focus its approach on the users considering “the true context of people’s work”.
The company believes that productivity could be improved if employees don’t have to deal with too many rules and processes. That is why the Netflix Stethoscope scans their devices and provides recommendations on security measures that should be taken, but allows them to perform the tasks on their own time.
The tool doesn’t apply any corrective directly but allows employees to perform the necessary action to secure their systems.
“Stethoscope is a web application that collects information for a given user’s devices and gives them clear and specific recommendations for securing their systems.” reads the description of the tool. “By providing personalized, actionable information–and not relying on automatic enforcement–Stethoscope respects people’s time, attention, and autonomy, while improving our company’s security outcomes.”
Stethoscope analyzes several aspects of employee’s device, including the presence of security software (firewall), disk encryption, automatic updates, operating system and software updates, screen lock, and jailbreaking or rooting.
This information is elaborated by the Stethoscope tool that rates them based on the criticality of the tasks to complete.

Netflix Stethoscope is a Python-based tool with a user interface developed with the React framework. The tool does not have its own data store, data sources are implemented as plugins, making the application scalable and allowing users to add new dataset and new security checks.
“The various data sources are implemented as plugins, so it should be relatively straightforward to add new inputs. We currently support LANDESK (for Windows), JAMF (for Macs), and Google MDM (for mobile devices).” continues the description from Netflix.
Netflix Stethoscope will likely include also Facebook’s Osquery is the list of future data sources.
The tool is an open project, everyone can contribute, the Stethoscope source code is available on GitHub.
[adrotate banner=”9″]
(Security Affairs – NetFlix Stethoscope, hacking)


