
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

New LinkedIn breach exposes data of 700 Million users

A new massive LinkedIn breach made the headlines, the leak reportedly exposes the data of 700M users, more than 92% of the total 756M users. A new massive LinkedIn breach made the headlines, a database containing data of 700M users, more than 92% of the total 756M users, is available for sale on forums on […]

LinkedIn 700m RECORDS

A new massive LinkedIn breach made the headlines, the leak reportedly exposes the data of 700M users, more than 92% of the total 756M users.

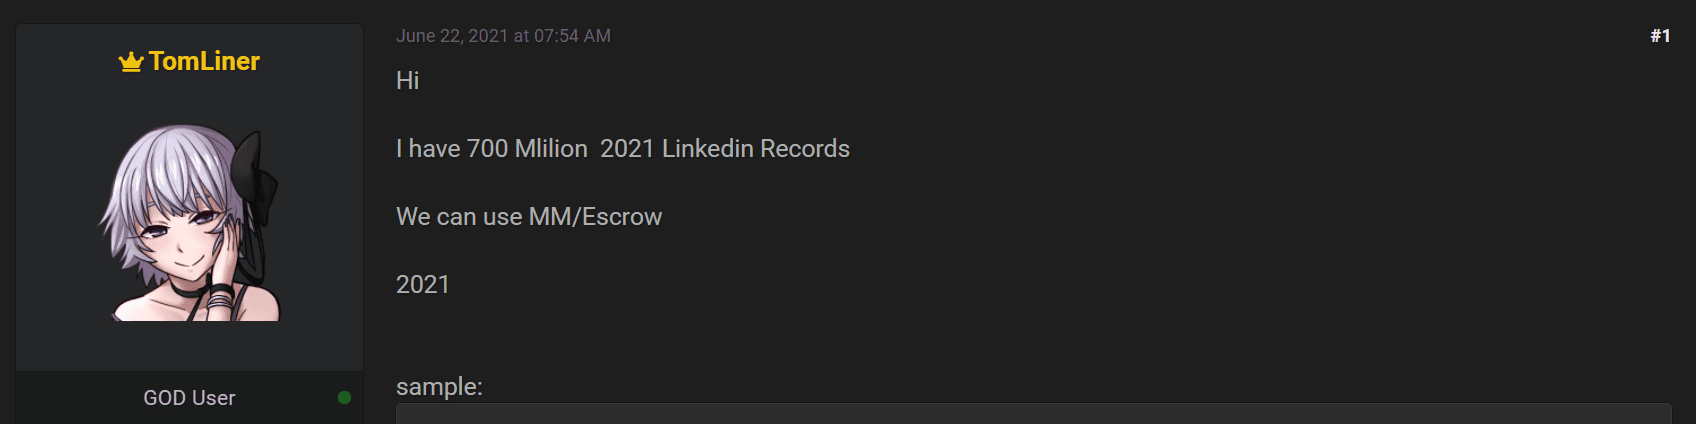
A new massive LinkedIn breach made the headlines, a database containing data of 700M users, more than 92% of the total 756M users, is available for sale on forums on the dark web.

LinkedIn 700m RECORDS

The exposed records include email addresses full names, phone numbers, physical addresses, geolocation records, LinkedIn username and profile URL, personal and professional experience/background, genders, and other social media accounts and usernames. Passwords are not included in the archive.

The threat actor that is offering for sale the data shared a sample of 1M records as proof of the authenticity of the archive. According to media that analyzed the data were able to confirm that they are genuine and up-to-date.

According to the RestorePrivacy website, the threat actor abused the official LinkedIn API to download the data

“We reached out directly to the user who is posting the data up for sale on the hacking forum. He claims the data was obtained by exploiting the LinkedIn API to harvest information that people upload to the site.” reported RestorePrivacy.

Data available for sale exposes 700+ million people at risk of cybercriminal activities, including identity theft, phishing and social engineering attacks, and account hijacking.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, LinkedIn)

[adrotate banner=”5″]

[adrotate banner=”13″]


