
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts from CloudFlare spotted a new dangerous botnet

Security experts from CloudFlare observed a new botnet that emerged in the wild and it could be dangerous as its predecessor Mirai. Which is the most dreaded botnet in the current threat landscape? The Mirai botnet of course, it was used by threat actors in the wild to power massive DDoS attack, such as the […]

botnet CVE-2024-11120 GeoVision

Security experts from CloudFlare observed a new botnet that emerged in the wild and it could be dangerous as its predecessor Mirai.

Which is the most dreaded botnet in the current threat landscape? The Mirai botnet of course, it was used by threat actors in the wild to power massive DDoS attack, such as the one that hit the Dyn DNS service.

Now, security experts observed a new botnet is emerging in the wild and it could be dangerous as its predecessor Mirai.

The botnet was first spotted on November 23 by researchers at the content delivery network CloudFlare.

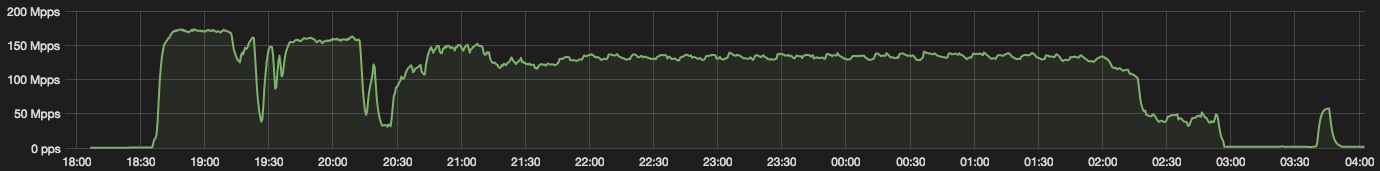
The DDoS attacks lasted 8.5 hours, attackers launched the offensive for six days at roughly the same time. The attacks were peaking at 400Gbps and hitting 320Gbps for hours on end.

“On November 23, the day before US Thanksgiving, our systems detected and mitigated an attack that peaked at 172Mpps and 400Gbps.” states the report published  CloudFlare. “The attack started at 1830 UTC and lasted non-stop for almost exactly 8.5 hours stopping at 0300 UTC. It felt as if an attacker ‘worked’ a day and then went home.”
ddos-attack-new-iot-botnet

The new string of cyber attacks are not powerful such as the ones launched through the Mirai malware, but anyway, they reached a significant volume.


Researchers discovered that the attacks are not powered from the Mirai botnet because they are launched from a differed software and are very large Layer3 and Layer4 DDoS attacks.

The researchers observed that the attacks were concentrated in a small number of locations mostly on the US west coast.

CloudFlare did not disclose further details of the DDoS attacks, it is not clear if the botnet is composed of IoT devices such as Mirai.

The new botnet will likely continue to grow and most experts fear it could be combined with other malicious infrastructure powering unprecedented DDoS attacks.
