
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts discovered a new variant of Shadow BTCware Ransomware Variant

The security expert Michael Gillespie discovered a new variant of the Shadow BTCware Ransomware which is manually installed on unsecured systems. The security expert Michael Gillespie discovered a new variant of the BTCWare ransomware, the malicious code was spread by hacking into poorly protected remote desktop services and manually installed by crooks. The new Shadow BTCware Ransomware variant appends the .[email]-id-id.shadow extension to the encrypted files, […]

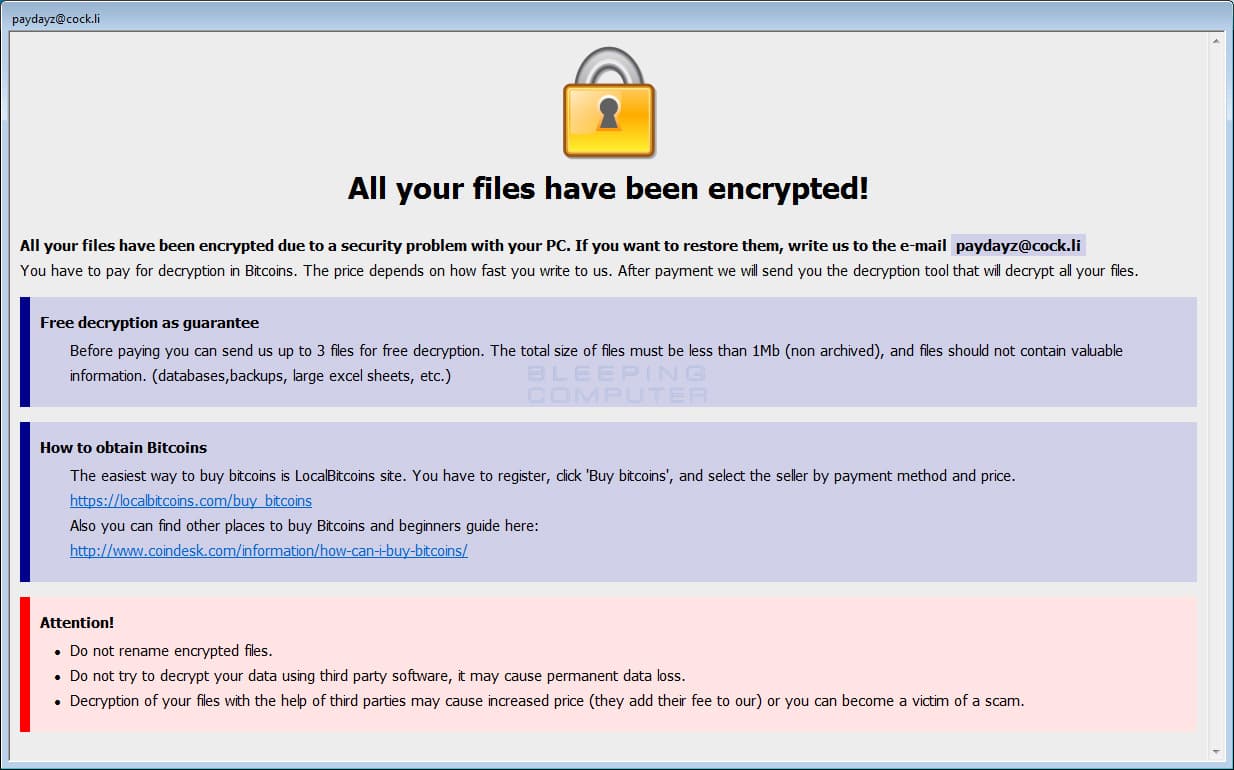
Shadow Ransomware (BTCWare) Ransom Note

The security expert Michael Gillespie discovered a new variant of the Shadow BTCware Ransomware which is manually installed on unsecured systems.

The security expert Michael Gillespie discovered a new variant of the BTCWare ransomware, the malicious code was spread by hacking into poorly protected remote desktop services and manually installed by crooks.

The new Shadow BTCware Ransomware variant appends the .[email]-id-id.shadow extension to the encrypted files, compared to previous versions it uses new email addresses a victim should contact to receive the instructions to pay the ransomware.

In the last version analyzed by the expert and reported by Bleeping Computer,  the contact email address used by crooks is paydayz@cock.li.

Shadow BTCware Ransomware Ransom Note

The extension appended to encrypted files is also changed, the Shadow BTCware Ransomware variant appends the .[email]-id-[id].shadow extension to encrypted file’s name.  (i.e. The file test.jpg is renamed to test.jpg.[paydayz@cock.li]-id-C0C.shadow).

“All your files have been encrypted! 

All your files have been encrypted due to a security problem with your PC. If you want to restore them, write us to the e-mail paydayz@cock.li
You have to pay for decryption in Bitcoins. The price depends on how fast you write to us. After payment we will send you the decryption tool that will decrypt all your files.
Free decryption as guarantee
Before paying you can send us up to 3 files for free decryption. The total size of files must be less than 1Mb (non archived), and files should not contain valuable information. (databases,backups, large excel sheets, etc.)
How to obtain Bitcoins.” reads an excerpt of the ransom note

As usual, to protect your system you need a proper cybersecurity posture. You should have a reliable and tested backup of data and of course, you have to use behavioral detections security solutions.

As usual, let me suggest to do not open attachments coming with unsolicited email messages, malware scan attachments with security tools (i.e. VirusTotal), make sure the OS and all the software are up to date.

Use strong passwords to protect your web services and never reuse the same password at multiple sites.

Further details, including the IoCs, have been published by Bleeping Computer.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Shadow BTCware Ransomware, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


