
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

New supply chain attack hits npm registry, compromising 40+ packages

Researchers uncovered a new supply chain attack targeting the npm registry that impacted over 40 packages belonging to multiple maintainers. Security researchers at Socket uncovered a malicious update to @ctrl/tinycolor, a package with 2.2M weekly downloads on npm. While investigating the case, they discovered it was linked to a larger supply chain attack that compromised […]

axios npm Package Contagious Interview campaign NPM

Researchers uncovered a new supply chain attack targeting the npm registry that impacted over 40 packages belonging to multiple maintainers.

Security researchers at Socket uncovered a malicious update to @ctrl/tinycolor, a package with 2.2M weekly downloads on npm. While investigating the case, they discovered it was linked to a larger supply chain attack that compromised over 40 packages from multiple maintainers. The rogue code added a function that tampered with package.json, injected a local script, and republished altered tarballs, automatically trojanizing downstream projects.

The researcher Daniel dos Santos Pereira first spotted suspicious behavior, and Socket’s detection flagged dozens of related threats. Tinycolor drew attention due to its popularity, but it was only one target in a broad campaign still under investigation.
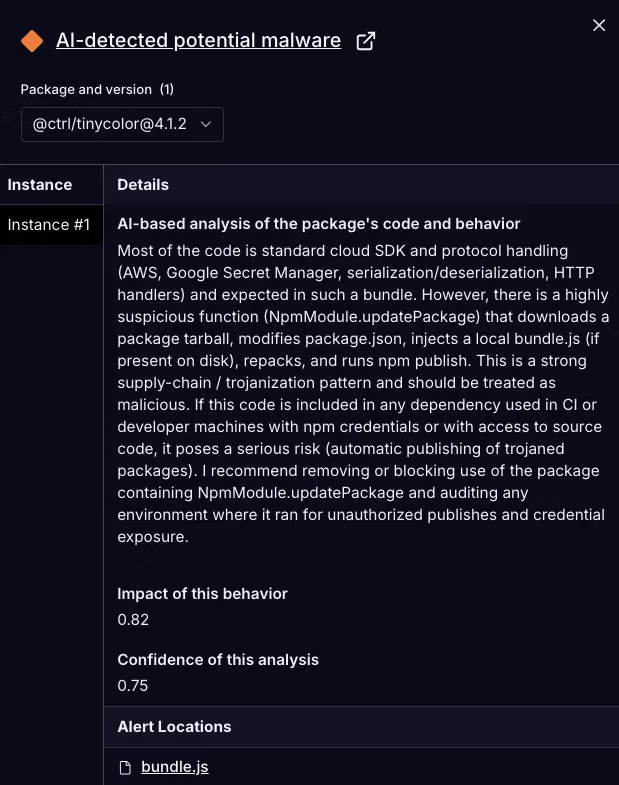
npm Package Compromised in Supply Chain Attack

Socket published the list of packages and versions compromised in the supply chain attack.

The malicious bundle.js downloads the legitimate secret scanner TruffleHog, profiles the host, and then scans files and repos for tokens and cloud credentials. It validates and reuses developer/cloud credentials, drops a GitHub Actions workflow using any available PAT, and exfiltrates findings (base64) to a hardcoded webhook. The script fetches platform-specific TruffleHog binaries, executes them locally, and automates secret theft and repository compromise.

The script scans hosts and repos for environment secrets (e.g., GITHUB_TOKEN, NPM_TOKEN, AWS keys). The malicious code verifies npm tokens via the whoami endpoint before calling GitHub APIs when a token exists. It probes cloud metadata endpoints (AWS/GCP) to harvest short-lived credentials from build agents. The malware also plants a GitHub Actions workflow in repositories, so future CI runs can exfiltrate secrets and artifacts.

“The workflow that it writes to repositories persists beyond the initial host. Once committed, any future CI run can trigger the exfiltration step from within the pipeline where sensitive secrets and artifacts are available by design.” concludes Socket’s report.

The researchers also published Indicators of Compromise for this attack.

Socket recommends developers uninstalling or pinning safe versions, auditing developer and CI/CD environments, rotating npm tokens and exposed secrets, and monitoring logs for unusual npm activity.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, supply chain attack)


