
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

US-CERT warns of New Zealand mosque shooting scams and malware campaigns

In the wake of the New Zealand mosque shooting, the CISA recommends users to remain vigilant on possible scams and malware attacks. Yesterday the horrible mass mosque shooting in New Zealand made the headlines, fifty people were killed. A gunman used GoPro to transmit a live stream of the massacre at a mosque. Despite social […]

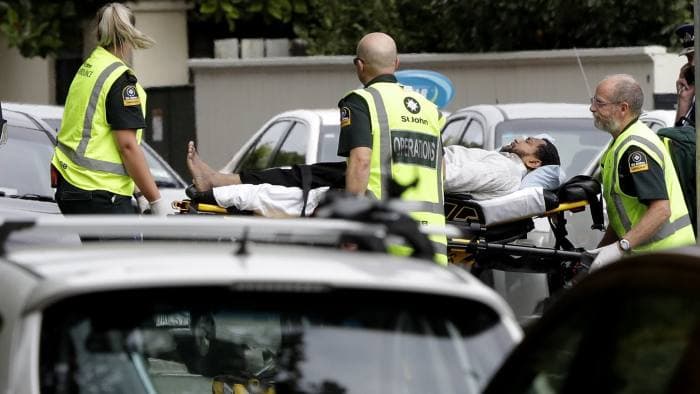
New Zealand mosque shooting

Source: The Financial times

In the wake of the New Zealand mosque shooting, the CISA recommends users to remain vigilant on possible scams and malware attacks.

Yesterday the horrible mass mosque shooting in New Zealand made the headlines, fifty people were killed. A gunman used GoPro to transmit a live stream of the massacre at a mosque.

New Zealand mosque shooting
Source: The Financial Times

Despite social media companies immediately removed the content from their platforms it is still possible to find multiple copies of the shooting videos online.

YouTube issued a statement condemning the snuff videos, confirming that it is removing them from its platform.

Unfortunately, curious people are searching for the video of the
New Zealand mosque shooting and crooks are aware of that and are attempting to exploit the interest in the cruel footage.

In the wake of the New Zealand mosque shooting, the Cybersecurity and Infrastructure Security Agency (CISA) recommends users to remain vigilant on possible scams and malware attacks.

Government experts are warning of spam campaigns using messages containing links pointing to malware or using malicious attachments.

“Users should exercise caution in handling emails related to the shooting, even if they appear to originate from trusted sources.” reads the security advisory published by the US-CERT. “Fraudulent emails often contain links or attachments that direct users to phishing or malware-infected websites.”

Experts believe attackers could use fake emails requesting donations from charitable organizations are, the US-CERT warns of fraudulent social media pleas, calls, texts, donation websites, and door-to-door solicitations relating to the event.

To avoid becoming a victim of malicious activity, users have to use caution when opening email attachments, even if the messages are sent from trusted sources. Another best practice consists of avoiding to click on links in unsolicited email messages.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – New Zealand mosque shooting, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


