
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Night Sky, a new ransomware operation in the threat landscape

Researchers warn of a new ransomware family, called ‘Night Sky,’ that uses a double-extortion model in attacks again businesses. Researchers from MalwareHunterteam first spotted a new ransomware family dubbed Night Sky that implements a double extortion model in attacks aimed at businesses. Once encrypted a file, the ransomware appends the ‘.nightsky‘ extension to encrypted file names. The […]

night sky ransomware 2

Researchers warn of a new ransomware family, called ‘Night Sky,’ that uses a double-extortion model in attacks again businesses.

Researchers from MalwareHunterteam first spotted a new ransomware family dubbed Night Sky that implements a double extortion model in attacks aimed at businesses. Once encrypted a file, the ransomware appends the ‘.nightsky‘ extension to encrypted file names.

The ransomware gang started its operations on December 27, 2021, and has already hacked the corporate networks of two organizations from Bangladesh and Japan respectively. The gang has also set up a leak site on the Tor network where it will publish files stolen to the victims that will not pay the ransom.

According to BleepingComputer, the group demanded one of its victims, the payment of an initial ransom of $800,000 to recover the encrypted data. The researchers noticed that the Night Sky ransomware doesn’t encrypt .dll or .exe files, it also doesn’t target the following list of files or folders:

AppData
Boot
Windows
Windows.old
Tor Browser
Internet Explorer
Google
Opera
Opera Software
Mozilla
Mozilla Firefox
$Recycle.Bin
ProgramData
All Users
autorun.inf
boot.ini
bootfont.bin
bootsect.bak
bootmgr
bootmgr.efi
bootmgfw.efi
desktop.ini
iconcache.db
ntldr
ntuser.dat
ntuser.dat.log
ntuser.ini
thumbs.db
Program Files
Program Files (x86)
#recycle

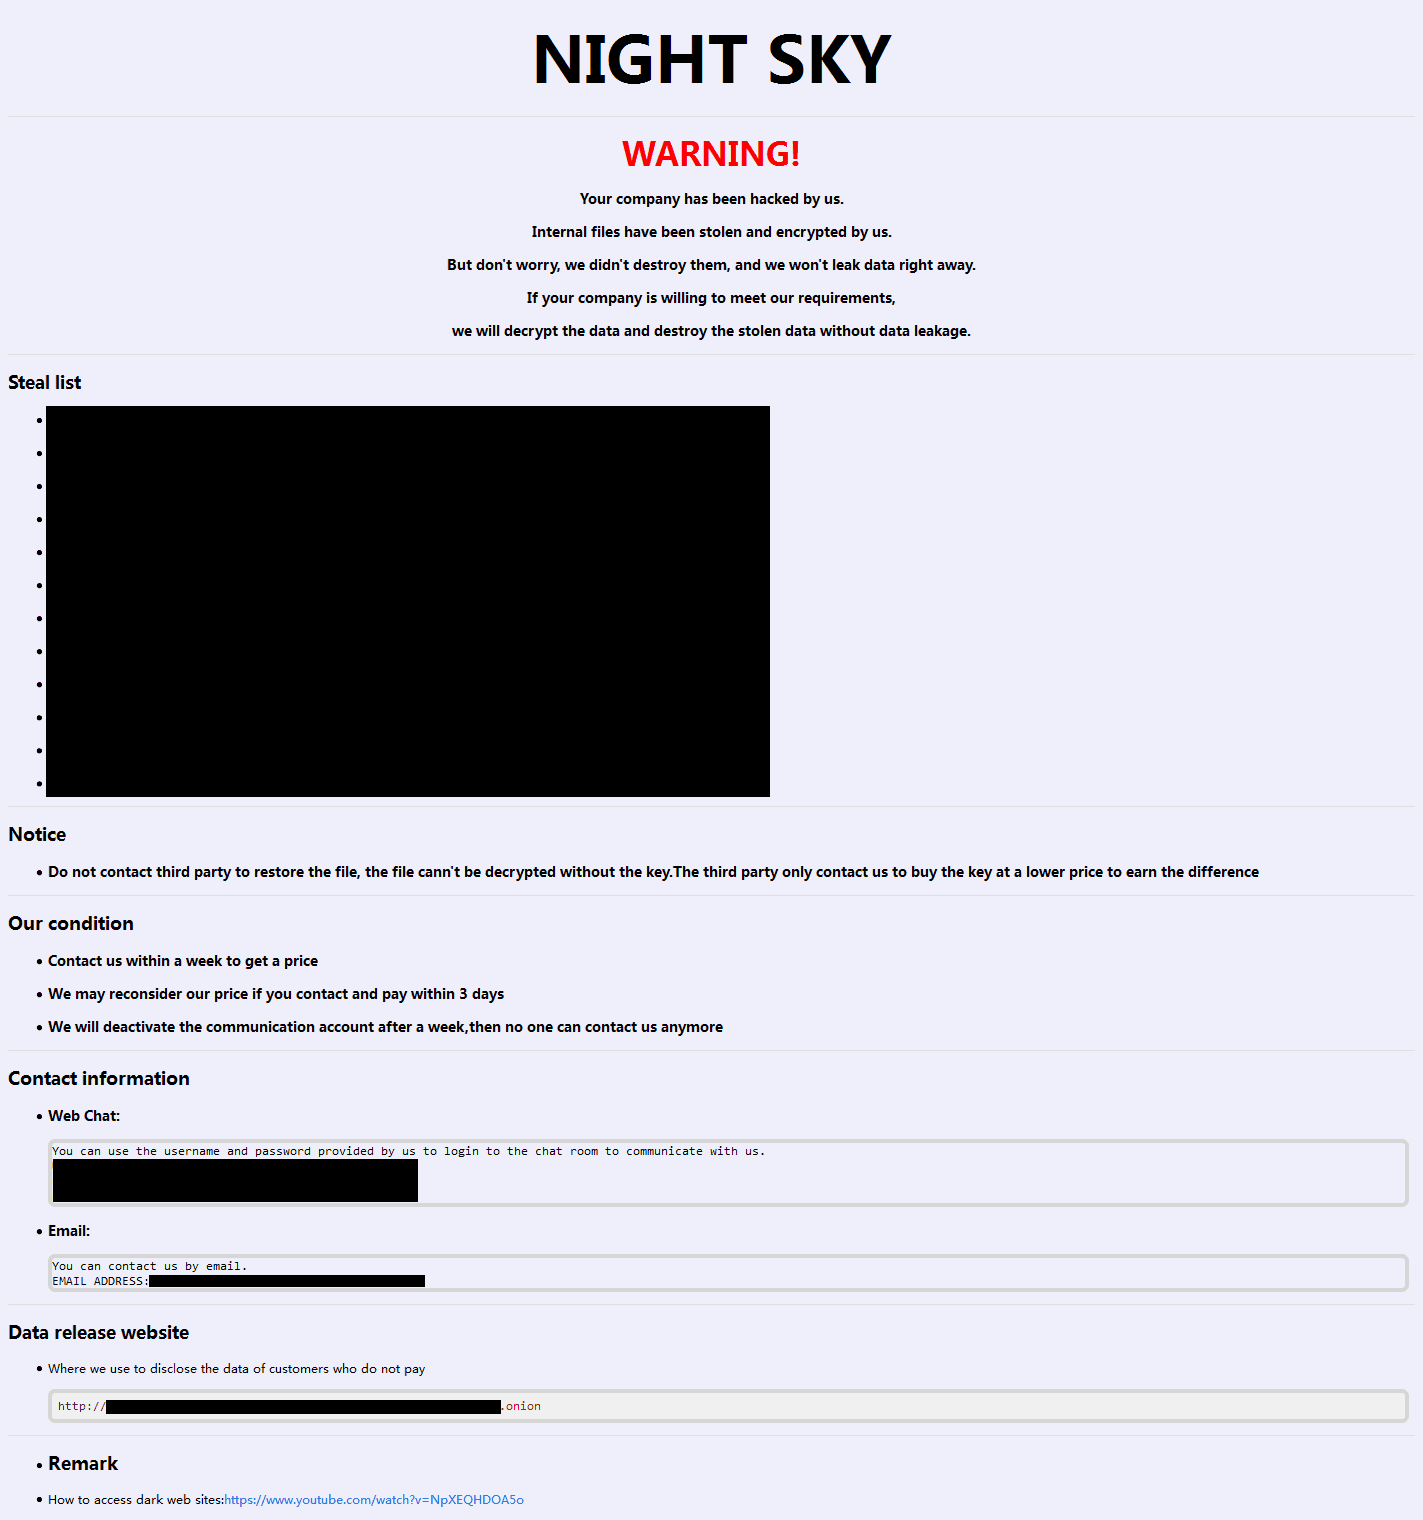
The ransomware drops a ransom note named NightSkyReadMe.hta in each folder, the file includes contact emails, and hardcoded credentials to the victim’s negotiation page along with the credentials to log in to the Rocket.Chat to contact the operators.

night sky ransomware 2
Source MalwareHunterTeam

Experts pointed out that the gang communicates with victims via email and a clear website running an instance of the Rocket.Chat.

Researchers believe that in the next months other organizations will be targeted by the Night Sky ransomware group.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


