
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Nitrokod crypto miner infected systems across 11 countries since 2019

Researchers spotted a Turkish-based crypto miner malware campaign, tracked as Nitrokod, which infected systems across 11 countries. Check Point researchers discovered a Turkish based crypto miner malware campaign, dubbed Nitrokod, which infected machines across 11 countries The threat actors dropped the malware from popular software available on dozens of free software websites, including Softpedia and […]

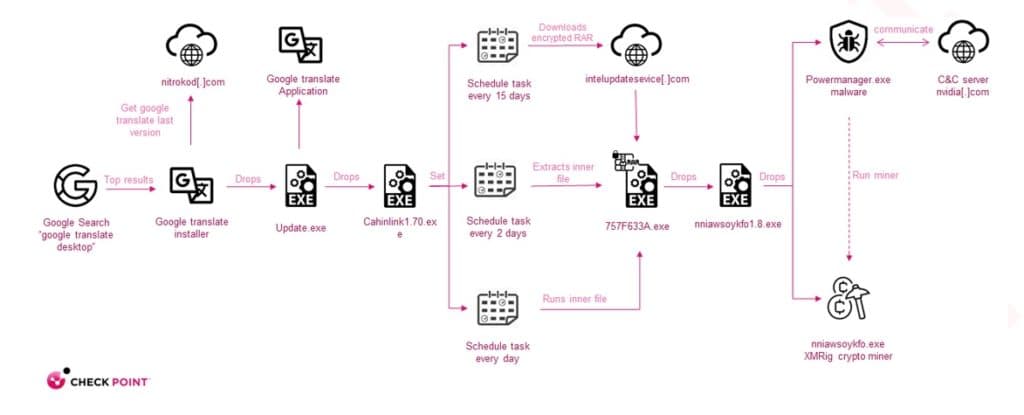
Nitrokod infection chain

Researchers spotted a Turkish-based crypto miner malware campaign, tracked as Nitrokod, which infected systems across 11 countries.

Check Point researchers discovered a Turkish based crypto miner malware campaign, dubbed Nitrokod, which infected machines across 11 countries

The threat actors dropped the malware from popular software available on dozens of free software websites, including Softpedia and uptodown. Experts noticed that the software can also be easily found through Google by searching “Google Translate Desktop download”.

The campaign operated under the radar for years because the operators adopted several tricks, such as implementing a delayed mechanism to unleash a long multi-stage infection.

“The software can also be easily found through Google when users search “Google Translate Desktop download”. While the applications boast a “100 CLEAN” banners on some site, the applications are in fact Trojanized, and contain a delayed mechanism to unleash a long multi-stage infection that ends with a cryptomining malware.” reads the analysis published by Check Point. “After the initial software installation, the attackers delayed the infection process for weeks and deleted traces from the original installation. This allowed the campaign to successfully operate under the radar for years.”

The malicious code is first executed almost a month after the Nitrokod software was installed on the victim’s system, the infection chain analyzed by the researcher is composed of 6 stages.

The attackers used a scheduled tacks mechanism to implement delays between each stage of the infection chain.

The infection chain starts with the installation of a tainted program downloaded from the Internet. Upon executing the software, an actual Google Translate application is installed and an updated file is dropped which starts a series of four droppers until the actual malware is dropped.
Once the malicious code is executed, the malware connects to the C2 server to get the XMRig crypto miner configuration and starts mining crypto currencies.

Nitrokod infection chain

In order to avoid detection, the stage 5 dropper performs some checks to determine if the malicious code is running in a VM or if some security programs are installed on the infected machine. If one of the security software is found, the malicious program exits.

Check Point shared Indicators of Compromise (IoCs) for this campaign.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Nitrokod)

[adrotate banner=”5″]

[adrotate banner=”13″]


