
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

BlackCat ransomware gang claims to have hacked US defense contractor NJVC

Another US defense contractor suffered a data breach, the BlackCat ransomware gang claims to have hacked NJVC. The ALPHV/BlackCat ransomware gang claims to have breached the IT firm NJVC, which supports the federal government and the United States Department of Defense. The company supports intelligence, defense, and geospatial organizations. The company has more than 1,200 employees in locations worldwide.  BlackCat added NJVC to […]

BlackCat ransomware NJVC

Another US defense contractor suffered a data breach, the BlackCat ransomware gang claims to have hacked NJVC.

The ALPHV/BlackCat ransomware gang claims to have breached the IT firm NJVC, which supports the federal government and the United States Department of Defense. The company supports intelligence, defense, and geospatial organizations. The company has more than 1,200 employees in locations worldwide. 


BlackCat added NJVC to the list of victims on its Tor leak site and is threatening to release the allegedly stolen data if the company will not pay the ransom.  

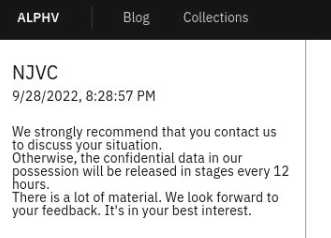
“We strongly recommend that you contact us to discuss your situation. Otherwise, the confidential data in our possession will be released in stages every 12 hours. There is a lot of material,” reads the ALPHV’s statement.

BlackCat ransomware NJVC

At the time of this writing, the ALPHV’s Tor leak site is not reachable and it is not clear if there is some link with the NJVC hack. Experts reported that the site was intermittently online, and someone noticed that the name of NJVC was removed from the site.

“Interestingly enough, BlackCat’s leak site on the dark web was accessible on 30 September, but NJVC was no longer posted among the gang’s victims. The latest current victim on the leak site was posted on 27 September, a day before the DoD contractor was initially posted.” reported CyberNews.

BlackCat has been operating since at least November 2021 and launched major attacks in January 2022 to disrupt OilTanking GmbH, a German fuel company, and in February 2022 against the aviation company, Swissport. The group is targeting high-profile businesses in critical industries including energy, financial institutions, legal services, and technology.

Blackcat ransomware is one of the fastest-growing Ransomware-as-a-Service (RaaS) underground groups practicing so called “quadruple extortion” by pressing victims to pay – leveraging encryption, data theft, denial of service (DoS) and harassment.

The BlackCat is also known as “ALPHV”, or “AlphaVM” and “AphaV”, a ransomware family created in the Rust programming language.

Recently another defense contractor disclosed a ransomware attack, threat actors breached Elbit Systems of America, a subsidiary of defense giant Elbit Systems.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, NJVC)

[adrotate banner=”5″]

[adrotate banner=”13″]


