
Microsoft discovered new custom malware, dubbed FoggyWeb, used by the Nobelium cyberespionage group to implant backdoor in Windows domains.
Microsoft Threat Intelligence Center (MSTIC) researchers have discovered a new custom malware, dubbed FoggyWeb used by the Nobelium APT group to deploy additional payloads and steal sensitive info from Active Directory Federation Services (AD FS) servers.
FoggyWeb is a post-exploitation backdoor used by the APT group to remotely exfiltrate the configuration database of compromised Active Directory Federation Services (AD FS) servers, decrypted token-signing certificate, and token-decryption certificate, it also allows threat actors to download and execute additional components.
“Once NOBELIUM obtains credentials and successfully compromises a server, the actor relies on that access to maintain persistence and deepen its infiltration using sophisticated malware and tools. NOBELIUM uses FoggyWeb to remotely exfiltrate the configuration database of compromised AD FS servers, decrypted token-signing certificate, and token-decryption certificate, as well as to download and execute additional components.” reads the analysis published by Microsoft. “Use of FoggyWeb has been observed in the wild as early as April 2021.”
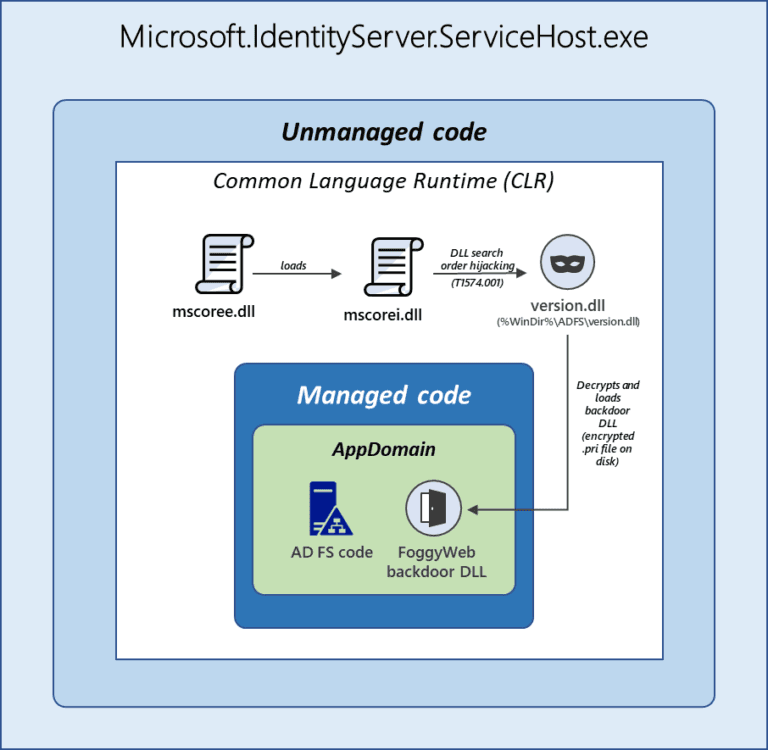
The attackers use the version.dll DLL to load FoggyWeb which is stored in the encrypted file Windows.Data.TimeZones.zh-PH.pri.
The AD FS service executable Microsoft.IdentityServer.ServiceHost.exe loads the version.dll via the DLL search order hijacking technique that involves the core Common Language Runtime (CLR) DLL files. The loader uses the custom Lightweight Encryption Algorithm (LEA) routine to decrypt the backdoor directly in the memory. The backdoor configures HTTP listeners for actor-defined URIs to intercept GET/POST requests sent to the AD FS server matching the custom URI patterns.

Researchers spotted the use of FoggyWeb since early April 2021.
Microsoft experts provided the following recommendations to organizations that have been compromised or that suspect to be under attacks by the group:
- Audit your on-premises and cloud infrastructure, including configuration, per-user and per-app settings, forwarding rules, and other changes the actor might have made to maintain their access
- Remove user and app access, review configurations for each, and re-issue new, strong credentials following documented industry best practices.
- Use a hardware security module (HSM) as described in securing AD FS servers to prevent the exfiltration of secrets by FoggyWeb.
The NOBELIUM APT is the threat actor that conducted supply chain attack against SolarWinds, which involved multiple families of implants, including the SUNBURST backdoor, TEARDROP malware, GoldMax malware, Sibot, and GoldFinder backdoors.
NOBELIUM focuses on government organizations, non-government organizations (NGOs), think tanks, military, IT service providers, health technology and research, and telecommunications providers.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, backdoor)
[adrotate banner=”5″]
[adrotate banner=”13″]


