
North Korea-linked threat actors are using the OtterCookie backdoor to target software developers with fake job offers.
North Korea-linked threat actors were spotted using new malware called OtterCookie as part of the Contagious Interview campaign that targets software developer community with fake job offers.
The Contagious Interview campaign was first detailed by Palo Alto Networks researchers in November 2023, however it has been active since at least December 2022. The attacks appear to be financially motivated and are not targeted. Since November 2024, threat actors employed the malware OtterCookie, alongside BeaverTail and InvisibleFerret, in the campaign.
“Since around November 2024, SOC has observed the execution of malware other than BeaverTail and InvisibleFerret in the Contagious Interview campaign.” reads the report published by NTT. “We call the newly observed malware OtterCookie and have investigated it. In this article, we will introduce OtterCookie, its execution flow and detailed behavior.”
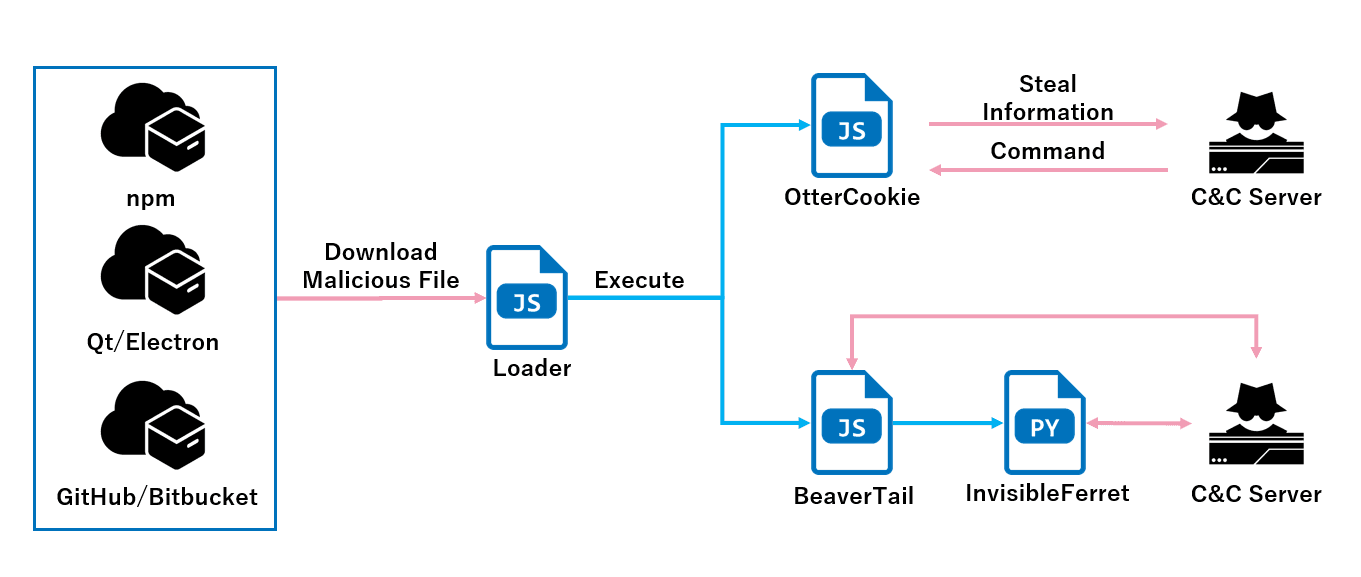
The attack chain starts with malicious Node.js projects or npm packages downloaded from GitHub or Bitbucket. Attackers recently also used applications created using Qt or Electron, suggesting that threat actors are actively experimenting.

Loaders for OtterCookie download JSON data from a remote source and execute the cookie property as JavaScript code. Attackers may also directly download and execute JavaScript, with control passing to a catch block when an HTTP 500 status code occurs. The loader primarily executes BeaverTail but has occasionally been observed running OtterCookie or both simultaneously.
OtterCookie was first observed in November 2024, however, experts believe it may have been active since September 2024, with minor implementation differences. The November version communicates via Socket.IO and can execute remote commands through the socketServer function, including executing shell commands and stealing device information (whour). Threat actors used shell commands to search for cryptocurrency wallet keys in document, image, and cryptocurrency-related files, which were then sent to a remote source. Attackers used commands like ls and cat to examine the target environment.
“Contagious Interview is actively experimenting and continuing to update its attack methods, and attacks have also been observed in Japan, so caution is advised.” concludes the report, which includes Indicators of Compromise (IoCs).
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, OtterCookie)


