
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Office of the Comptroller of the Currency reported a former employee stolen data from office

A former employee of the Office of the Comptroller of the Currency downloaded 10,000 records onto thumb drives before his retirement in November 2015. On Friday, the US banking regulator told Congress about a potential “major information security incident” after it discovered that a former employee has downloaded a large number of files onto thumb drives […]

Office of the Comptroller of the Currency reported a former employee stolen data from office

A former employee of the Office of the Comptroller of the Currency downloaded 10,000 records onto thumb drives before his retirement in November 2015.

On Friday, the US banking regulator told Congress about a potential “major information security incident” after it discovered that a former employee has downloaded a large number of files onto thumb drives before his retirement in November 2015.

According to the Office of the Comptroller of the Currency, there was no evidence that suggests that the former employee has publicly disclosed the data neither he has misused it.

The Office of the Comptroller is tasked with protecting consumers and the regular activity on financial markets.

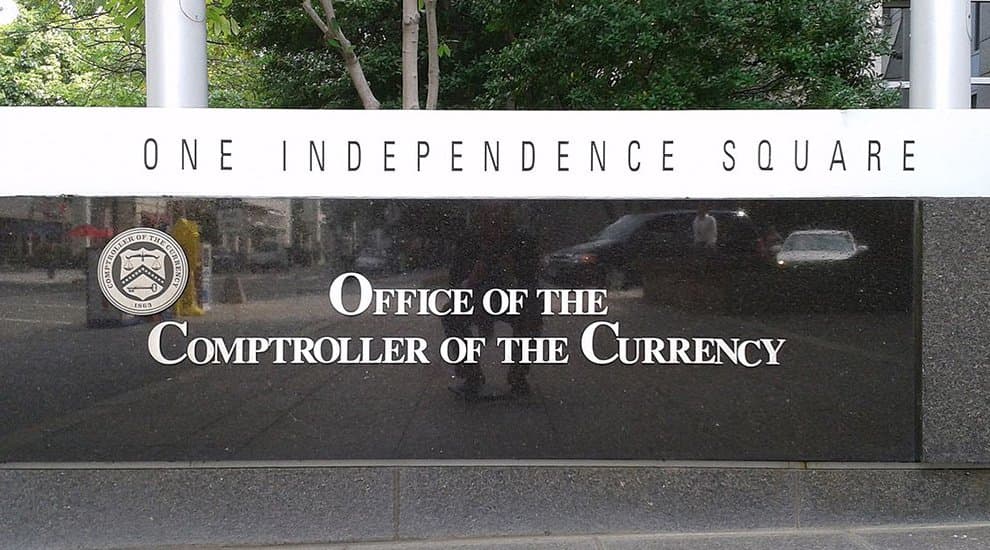
office-of-the-comptroller-of-the-currency-breach

The banking regulator confirmed the former employee downloaded a large number of files onto two removable thumb drives, the stolen information was encrypted.  According to the Office of the Comptroller of the Currency, the security breach was only detected last month after a routine security assessment.

The OCC reported that when the former employee was contacted by the Agency, he “was unable to locate or return the thumb drives to the agency.”

“The OCC has deemed the breach a “major incident” because the devices containing the information are not recoverable and more than 10,000 records were removed, the agency said.” reported the Reuters. 

“An official familiar with the investigation declined to comment on a possible motive. The official, who was not authorized to discuss the case, noted that a large batch of unclassified personnel records were among the cache.”

Experts have downplayed the risks for the users arguing that the information was not released to unauthorized sources.It is quite frequent that employees or consultants report missing thumb drives containing sensitive data.

It is quite frequent that employees or consultants report missing thumb drives containing sensitive data.

Recently the National Security Agency went in the headlines again after a contractor was accused of having harvested high-confidential information from the Agency systems.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Office of the Comptroller of the Currency, security breach)


