
A new hacking campaign, tracked as ‘OiVaVoii’, is targeting company executives with malicious OAuth apps.
Researchers from Proofpoint have uncovered a new campaign named ‘OiVaVoii’ that is targeting company executives, former board members, Presidents and managers with bogus OAuth apps and cleverly-crafted lures sent from compromised Office 365 accounts.
Microsoft has blocked many of the apps, but according to the researchers, the campaign is still ongoing. Once the attackers have compromised the executive accounts, they can carry out a broad range of malicious activities, from insider phishing to human-operated ransomware attacks.
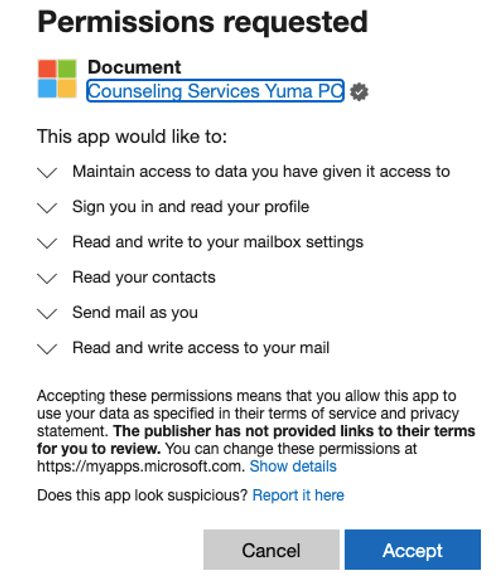
The researchers uncovered five malicious OAuth applications employed in this campaign, some of them created by a “verified” organization (‘Yuma Counseling Services’).
| App name | App id | Published Type | Creation Date | Status |
| Upgrade | 01d33e0a-83c1-4e5c-98be-096bc270eabf | Verified | 16/11/21 | Blocked |
| Upgrade | f9b75e84-5235-48d3-b745-37c99c056b64 | Verified | 23/1/22 | Blocked |
| Document | c517e6b9-a1d5-4f7e-8081-dfb2142c056a | Verified | 26/1/22 | Blocked |
| Shared | b2710450-6cec-4e4f-989f-c16f3041620a | Unverified | 27/1/22 | Available |
| UserInfo | 32fc064d-d4ea-43f9-ae7f-e90da936053f | Unknown | 27/1/22 | Blocked |
At least three of the rogue third-party apps were created by two different “verified publishers,”a circumstance that suggests the attackers have compromised admin user-account within a legitimate Office tenant.
“Once these apps were created, authorization requests were then sent, via email, to numerous targeted users, including high-level executives. The seemingly benign identity of the publishing organization was a substantial advantage, causing multiple unsuspecting victims to authorize these applications. ” reads the analysis published by Proofpoint. “This enables the attackers to generate OAuth tokens on the compromised user’s behalf and complete the account takeover.”
The threat actors used the apps to send out authorization requests to the victims and upon accepting them, threat actors could use the token to send emails from their accounts to other employees within the same organization

In order to prevent victims from canceling the request by clicking “Cancel”, attackers manipulate the Reply URL to redirect back to the consent screen autonomously.
“apps potentially use MITM proxy attacks. This means that credential theft could take place as part of the attack flow, greatly increasing the risk of a complete account takeover and prolonged persistency.” continues the report.
Experts pointed out that all the detected apps requested similar permissions, mainly related to mailbox access (read & write).
“As we monitor the threat, we expect to see new apps being created and proliferated.” concludes ProofPoint. “Therefore, we advise taking immediate prevention measures, such as limiting app authorization by users’ and using layered defense solutions for early detection and remediation. In case of confirmed impact, we advise immediate revocation and deletion of malicious apps, along with suspicious mailbox rules, hosted files, and messages.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, OiVaVoii campaign)
[adrotate banner=”5″]
[adrotate banner=”13″]


