
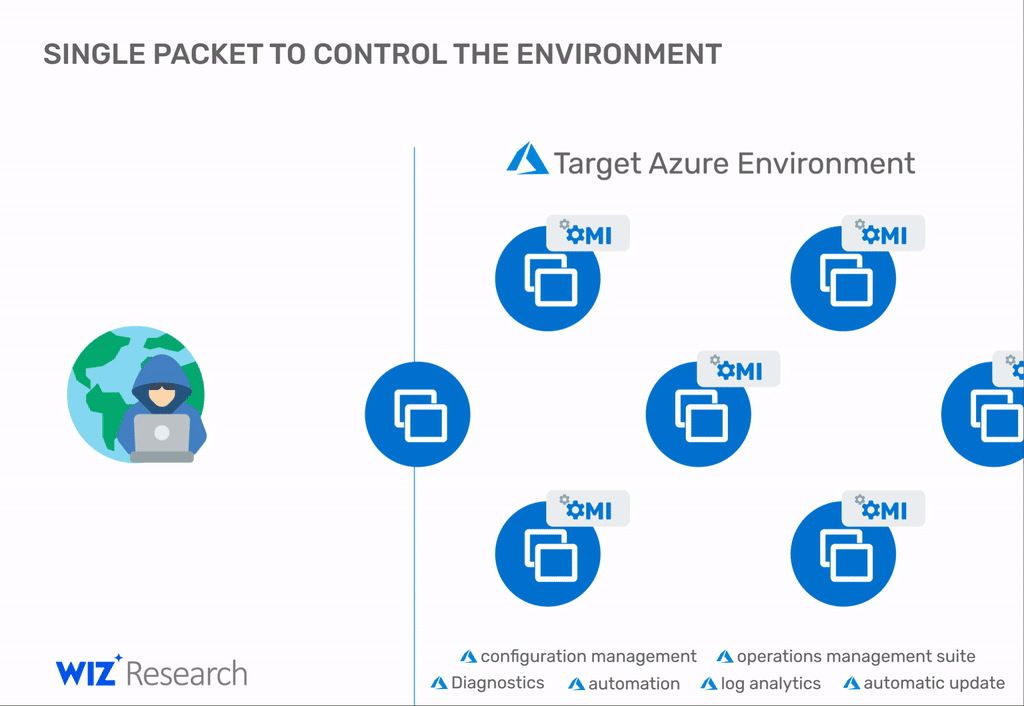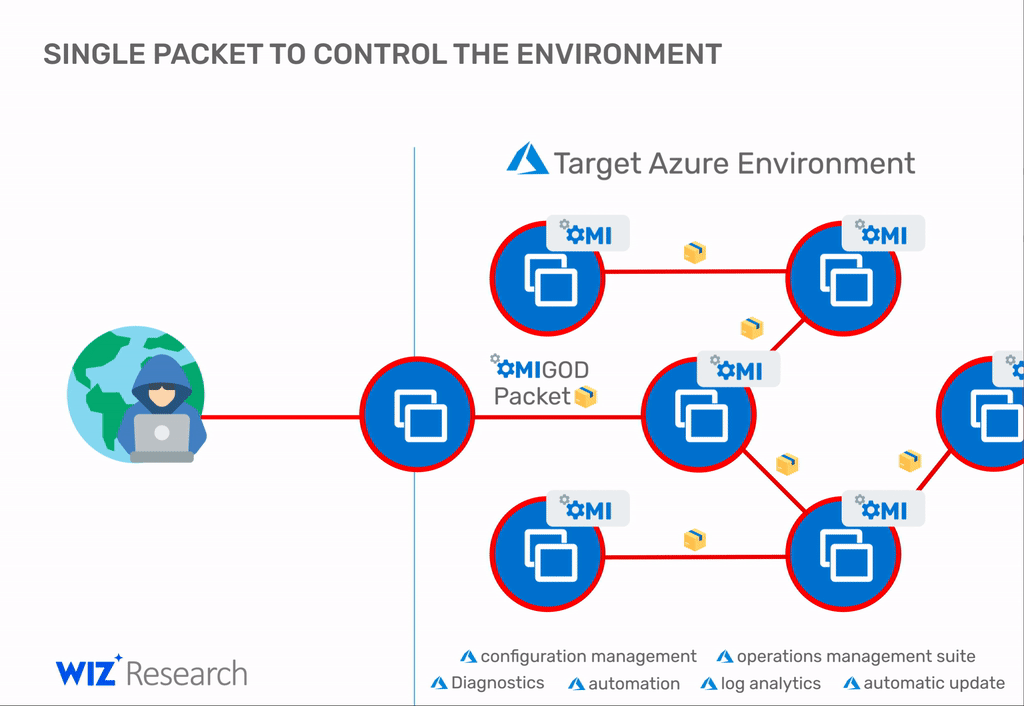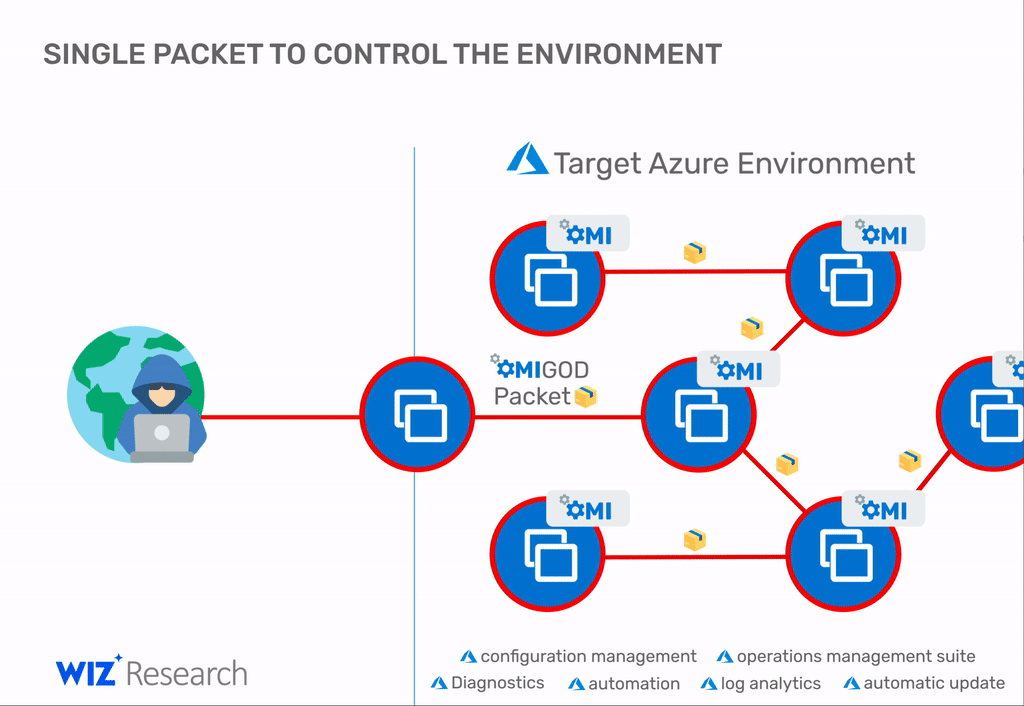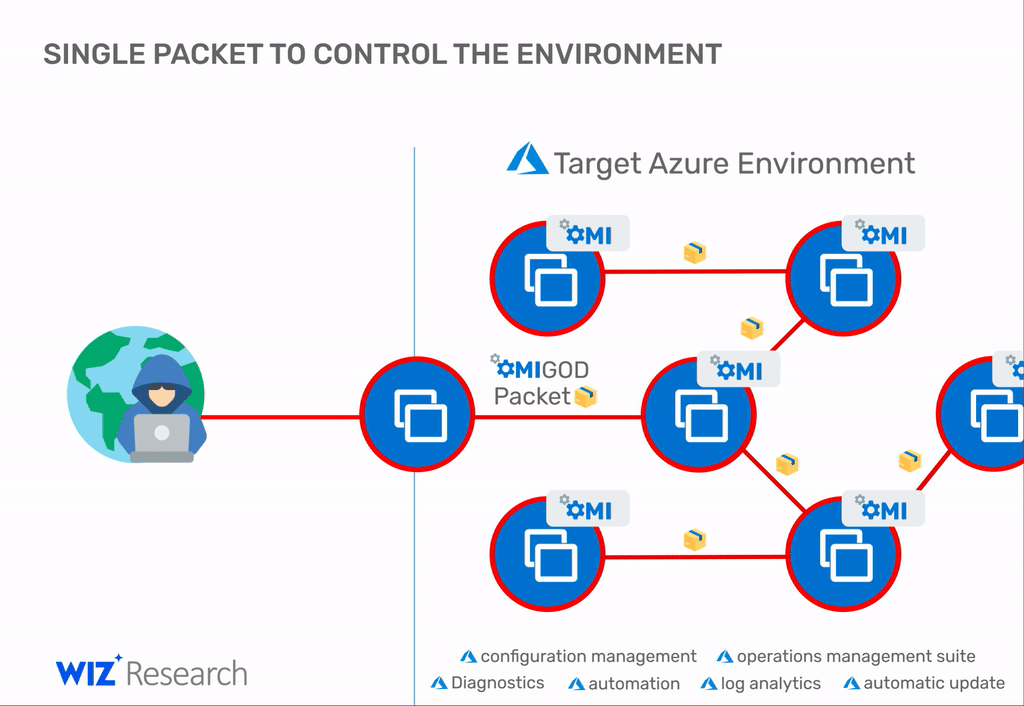
The Mirai botnet starts exploiting the recently disclosed OMIGOD vulnerability to compromise vulnerable systems exposed online.
Threat actors behind a Mirai botnet starts exploiting a critical Azure OMIGOD vulnerability, tracked as CVE-2021-38647, a few days after Microsoft disclosed them.
Recently released September 2021 Patch Tuesday security updates have addressed four severe vulnerabilities, collectively tracked as OMIGOD, in the Open Management Infrastructure (OMI) software agent that exposes Azure users to attack. Below is the list of the OMIGOD flaws:
- CVE-2021-38647 – Unauthenticated RCE as root (Severity: 9.8)
- CVE-2021-38648 – Privilege Escalation vulnerability (Severity: 7.8)
- CVE-2021-38645 – Privilege Escalation vulnerability (Severity: 7.8)
- CVE-2021-38649 – Privilege Escalation vulnerability (Severity: 7.0)
The vulnerabilities were reported by Wiz’s research team, an attacker could exploit OMIGOD vulnerabilities to execute code remotely or elevate privileges on vulnerable Linux virtual machines running on Azure.
Researchers estimate that thousands of Azure customers and millions of endpoints are potentially at risk of attack.
Threat actors immediately started scanning the Internet for vulnerable installs as confirmed by independent researchers and security firms. The popular expert Kevin Beaumont reported that a Mirai botnet is attempting to compromise vulnerable systems and that it also closes port 5896 (OMI SSL port) to prevent other threat actors to infect them.
Microsoft released a guidance that urges customers to update vulnerable extensions for their Cloud and On-Premises deployments as the updates become available per a schedule shared by the Microsoft Security Response Center team.
“New VMs in these regions will be protected from these vulnerabilities post the availability of updated extensions.” reads a Microsoft.
“Updates are already available for DSC and SCOM to address the remote execution vulnerability (RCE). While updates are being rolled out using safe deployment practices, customers can protect against the RCE vulnerability by ensuring VMs are deployed within a Network Security Group (NSG) or behind a perimeter firewall and restrict access to Linux systems that expose the OMI ports (TCP 5985, 5986, and 1270). Note that ports 5985 and 5986 are also used for PowerShell Remoting on Windows and are not impacted by these vulnerabilities. “
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Mirai)
[adrotate banner=”5″]
[adrotate banner=”13″]


