
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

OnePoint Patient Care data breach impacted 795916 individuals

US hospice pharmacy OnePoint Patient Care suffered a data breach that exposed the personal info of approximately 800,000 individuals. OnePoint Patient Care is a U.S.-based pharmacy specializing in hospice and palliative care services, providing customized medications and support for patients with advanced illnesses. It partners with healthcare providers to manage and deliver complex medication regimens […]

OnePoint Patient Care

US hospice pharmacy OnePoint Patient Care suffered a data breach that exposed the personal info of approximately 800,000 individuals.

OnePoint Patient Care is a U.S.-based pharmacy specializing in hospice and palliative care services, providing customized medications and support for patients with advanced illnesses. It partners with healthcare providers to manage and deliver complex medication regimens directly to patients’ homes or care facilities.

The company suffered a data breach that exposed the personal info of approximately 800,000 individuals. OPPC reported to the US Department of Health and Human Services that the security incident impacted 795916 individuals. 

The organization observed suspicious activity on its network on August 8, 2024 and promptly initiated an internal investigation. The company started its incident response procedure to contain the incident with the help of a forensic security firm.

“On August 8, 2024, OPPC detected suspicious activity on its computer network. Upon identifying the issue, OPPC promptly initiated an internal investigation, took steps to contain the incident, and engaged a forensic security firm to further investigate. OPPC also notified law enforcement.” reads the notice of Data Security Incident published by the company on its website. “The incident had no impact on OPPC’s operations but, on August 15, 2024, OPPC learned that, between August 6 and 8, 2024, someone obtained some individuals’ personal information from OPPC’s systems without authorization.”

OnePoint Patient Care (OPPC) discovered the data breach on August 15, 2024, an unauthorized party has access to personal information between August 6 and 8, 2024.

The compromised data includes names, residence information, medical records, diagnosis, prescription details, and, for some, Social Security numbers.

OPPC recommends that impacted individuals monitor credit reports and statements for suspicious activity and report any fraud to law enforcement.

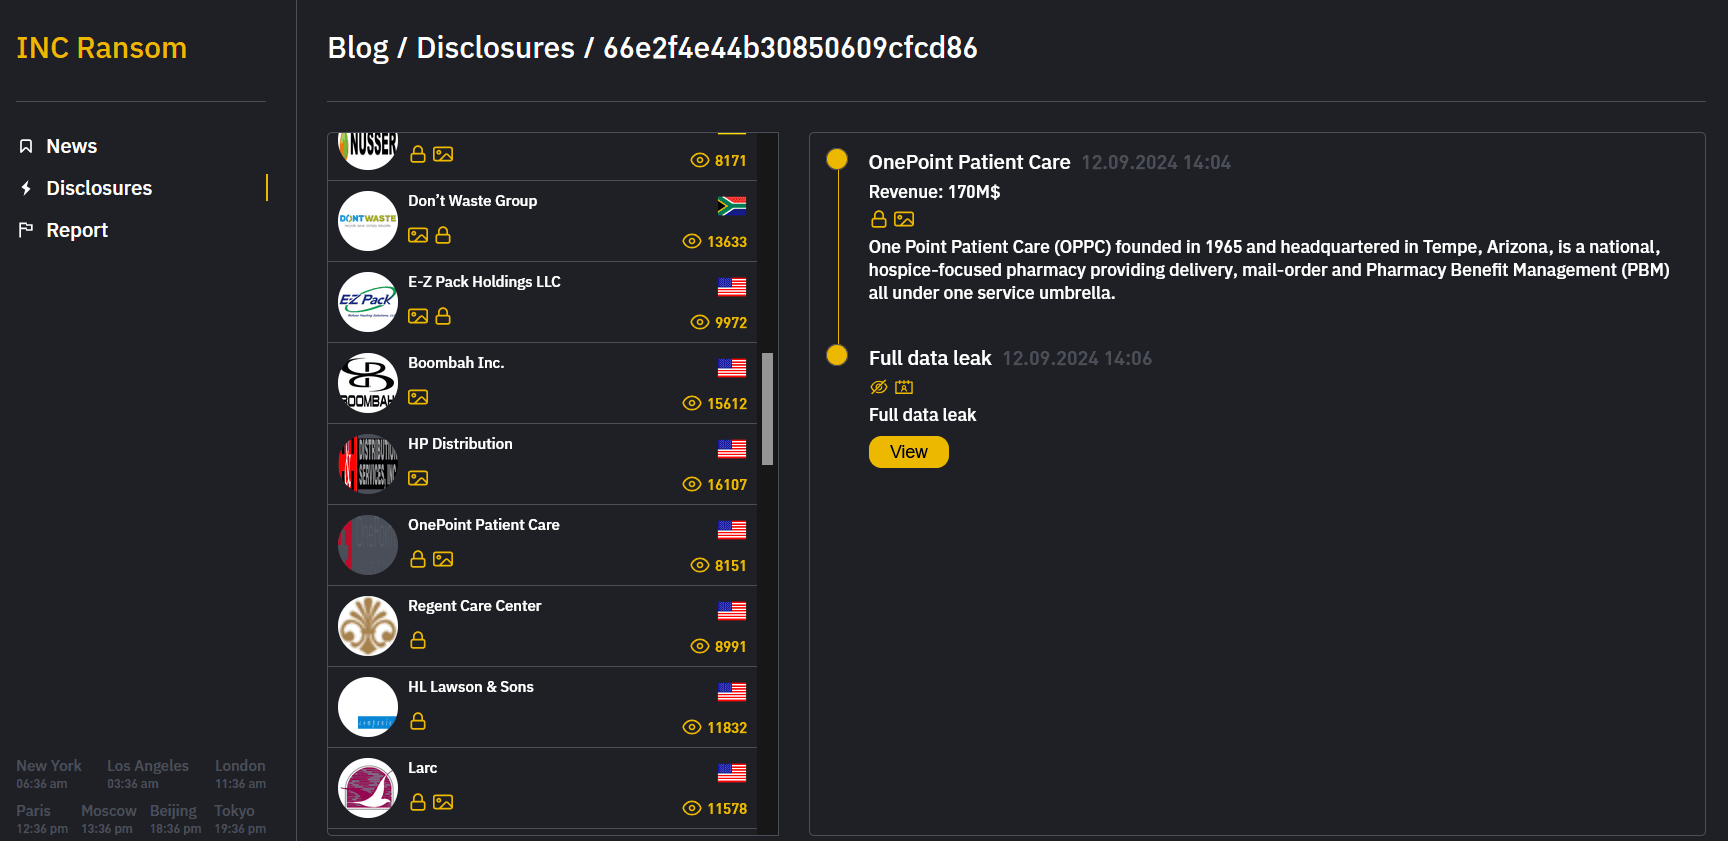
In September, the Inc Ransom ransomware group added healthcare organizations to the list of victims on its Tor leak site. The company did not pay the ransom and Inc Ransom group leaked data allegedly stolen from the organization.

The INC RANSOM has been active since 2023, it claimed responsibility for the breach of at least 65 organizations to date.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, OnePoint Patient Care)


