
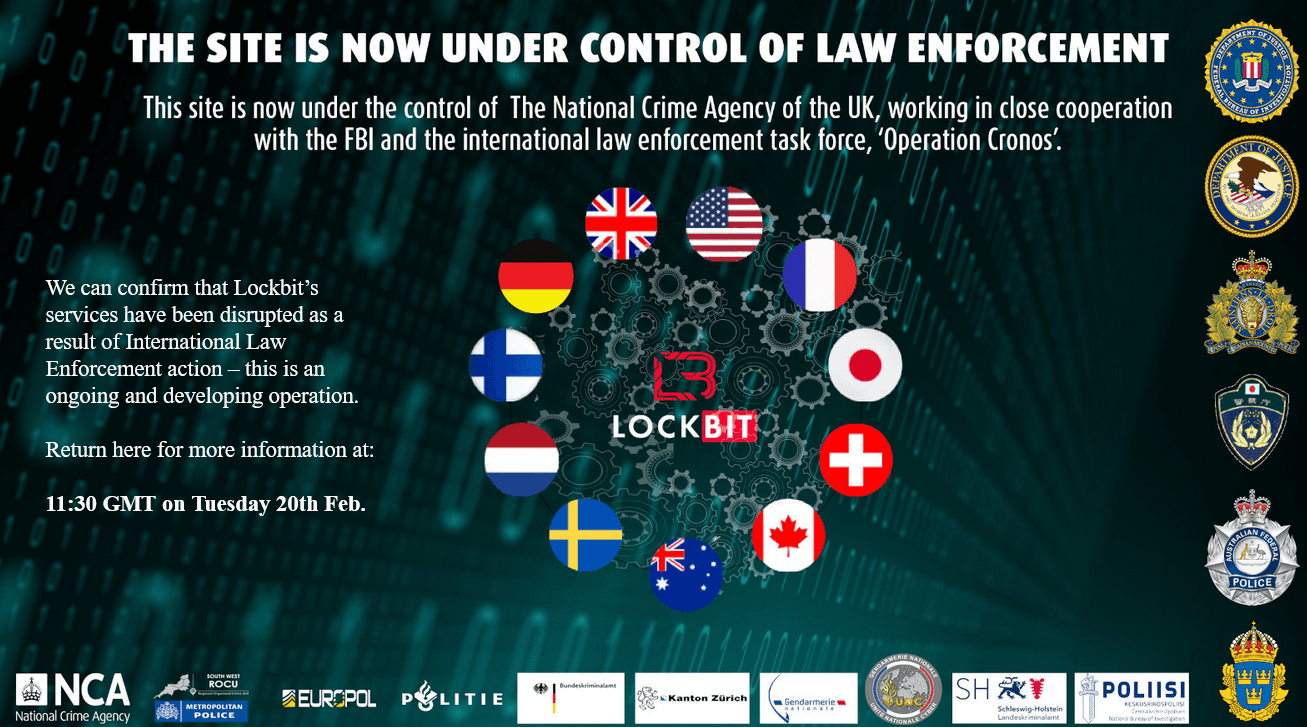
An international law enforcement operation codenamed ‘Operation Cronos’ led to the disruption of the LockBit ransomware operation.
A joint law enforcement action, code-named Operation Cronos, conducted by law enforcement agencies from 11 countries has disrupted the LockBit ransomware operation.
Below is the image of the Tor leak site of the Lockbit ransomware gang that was seized by the UK National Crime Agency (NCA).
“The site is now under the control of law enforcement. This site is now under the control of The National Crime Agency of the UK, working in close cooperation with the FBI and the international law enforcement task force, ‘Operation Cronos’,” reads the banner.
“We can confirm that Lockbit’s services have been disrupted as a result of International Law Enforcement action – this is an ongoing and developing operation. Return here for more information at: 11:30 GMT on Tuesday 20th Feb”
The Operation Cronos operation is still ongoing and NCA’s announced that more information will be published tomorrow, February 20, 2024.

“The site is now under the control of law enforcement. This site is now under the control of The National Crime Agency of the UK, Working in close cooperation with the FBI and the international law enforcement task force, Operation Cronos,” the banner reads.
“We can confirm that Lockbit’s services have been disrupted as a result of International Law Enforcement action – this is an ongoing and developing operation.”
vx-underground researchers contacted the administrators of the gang who confirmed that their infrastructure was seized by the FBI.
LockBit is a prominent ransomware operation that first emerged in September 2019. In 2022, LockBit was one of the most active ransomware groups, and its prevalence continued into 2023. Since January 2020, affiliates utilizing LockBit have targeted organizations of diverse sizes spanning critical infrastructure sectors such as financial services, food and agriculture, education, energy, government and emergency services, healthcare, manufacturing, and transportation. The LockBit ransomware operation operated under a Ransomware-as-a-Service (RaaS) model, recruiting affiliates to carry out ransomware attacks through the utilization of LockBit ransomware tools and infrastructure.
According to a joint report published by US authorities and international peers, the total of U.S. ransoms paid to LockBit is approximately $91M since LockBit activity was first observed in the U.S. on January 5, 2020.
Follow me on Twitter: @securityaffairs and Facebook
(SecurityAffairs – hacking, ransomware)


