
Chinese Iron Tiger APT is back, the new campaign, dubbed by Operation PZChao is targeting government, technology, education, and telecommunications organizations in Asia and the US.
Malware researchers from Bitdefender have discovered and monitored for several months the activity of a custom-built backdoor capable of password-stealing, bitcoin-mining, and of course to gain full control of the victim’s machine.
The campaign, dubbed by Bitdefender, Operation PZChao is targeting government, technology, education, and telecommunications organizations in Asia and the US.
“This is also the case of a custom-built piece of malware that we have been monitoring for several months as it wrought havoc in Asia. Our threat intelligence systems picked up the first indicators of compromise in July last year, and we have kept an eye on the threat ever since.” states the report published by BitDefender.
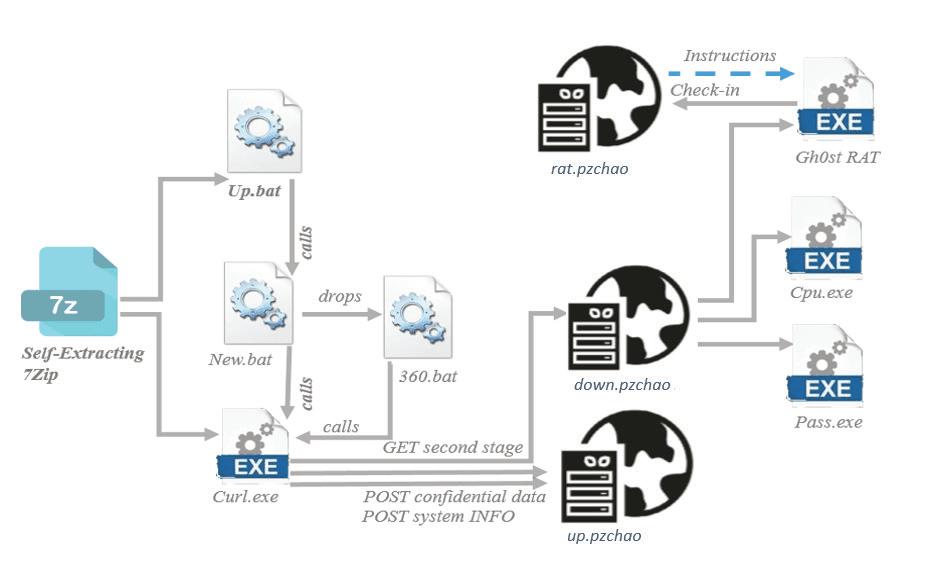
“An interesting feature of this threat, which drew our team to the challenge of analyzing it, is that it features a network of malicious subdomains, each one used for a specific task (download, upload, RAT related actions, malware DLL delivery). The payloads are diversified and include capabilities to download and execute additional binary files, collect private information and remotely execute commands on the system.”
It is interesting to notice that the malware features a network of malicious subdomains, each one used for a specific task (download, upload, RAT related actions, malware DLL delivery).
The experts who analyzed the command and control infrastructure and malicious codes used by the hackers (i.e. Gh0st RAT) speculate the return of the Iron Tiger APT group.
The Iron Tiger APT (aka Panda Emissary or TG-3390) is active at least since 2010 and targeted organization in APAC, but since 2013 it is attacking high-technology targets in the US.
The experts found many similarities between the Gh0stRat samples used in the Operation PZChao and the ones used in past campaigns associated with the Iron Tiger APT.
Attackers behind the Operation PZChao targeted victims with spear-phishing messages using a malicious VBS file attachment that once executed will download the malicious payloads to Windows systems from a distribution server. The researchers determined the IP address of the server, it is “125.7.152.55” in South Korea and hosts the “down.pzchao.com”.
Experts highlighted that new components are downloaded and executed on the target system in every stage of the attack.

The experts discovered that the first payload dropped onto compromised systems is a bitcoin miner.
The miner is disguised as a ‘java.exe’ file and used every three weeks at 3 am to avoid being noticed while mining cryptocurrency likely to fund the campaign.
But don’t forget that the main goal of the Operation PZChao is cyber espionage, the malicious code leverages two versions of the Mimikatz tool to gather credentials from the infected host.
The most important component in the arsenal of the attacker remains the powerful Gh0sT RAT malware that allows controlling every aspect of the infected system.
“this remote access Torjan’s espionage capabilities and extensive intelligence harvesting from victims turns it into an extremely powerful tool that is very difficult to identify,” concluded Bitdefender. “The C&C rotation during the Trojan’s lifecycle also helps evade detection at the network level, while the impersonation of legitimate, known applications takes care of the rest.”
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Iron Tiger APT, Operation PZChao)
[adrotate banner=”5″]
[adrotate banner=”13″]


