
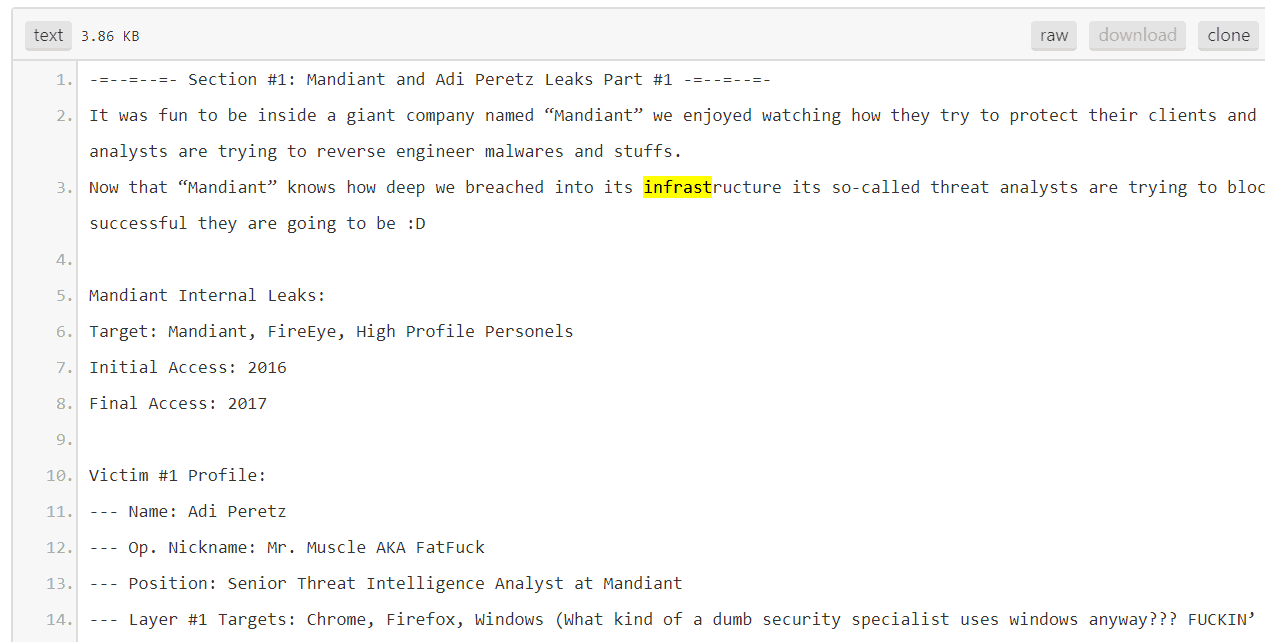
Late Sunday evening, hackers leaked details alleged stolen from a compromised system maintained by Adi Peretz, a Senior Analyst at Mandiant.
Late Sunday evening, hackers have posted details alleged stolen from a system belonging to Adi Peretz, a Senior Threat Intelligence Analyst at security firm FireEye/Mandiant.
The leaked archive is a 337MB PST file containing the expert’s emails. Leaked archive also includes images of its accounts, including One Drive, Live, LinkedIn, geo-tracking of personal devices for at least a year, billing records and PayPal receipts.

“In addition to that are images detailing the compromise of their One Drive account, Live account, LinkedIn account, geo-tracking of personal devices for at least a year, billing records and PayPal receipts, credentials for an engineering portal at FireEye, WebEx and JIRA portals, as well as Live and Amazon accounts. There are also records related to an alleged customer, Bank Hapoalim, and internal documentation and presentations, including one for the IDF (Israel Defense Forces) from 2016.” reported Salted Hash.
The security firm has denied any intrusion in its systems.
The hackers who published the alleged Mandiant Internal Leaks claims it is part of the ongoing campaign #OpLeakTheAnalyst.
“It was fun to be inside a giant company named “Mandiant” we enjoyed watching how they try to protect their clients and how their dumb analysts are trying to reverse engineer malwares and stuffs.
Now that “Mandiant” knows how deep we breached into its infrastructure its so-called threat analysts are trying to block us. Let’s see how successful they are going to be :D” reads the message published on PasteBit.
Independent analysts who visioned the leaked material believe there is no evidence of any compromise.
Only one workstations seems to be infected during #leakTheAnalyst . Dump does not show any damage to core assets of #Mandiant
— Ido Naor (@IdoNaor1) July 31, 2017
The security researcher Hanan Natan also believes the overall Mandiant networks weren’t breached:
Mandiant Leak https://t.co/sEyr73tQA7
Personal data and some internal docs, apparently only on one workstation #LeakTheAnalyst— Unsame Consequences (@DragonMcNuggets) July 31, 2017
Below the response issued by FireEye:
“We are aware of reports that a Mandiant employee’s social media accounts were compromised. We immediately began investigating this situation, and took steps to limit further exposure. Our investigation continues, but thus far, we have found no evidence FireEye or Mandiant systems were compromised.”
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – FireEye, OpLeakTheAnalyst)
[adrotate banner=”5″]
[adrotate banner=”13″]


