Security experts from ERPScan discovered a new flaw in Oracle MICROS PoS terminals that could be exploited by an attacker to read sensitive data from devices.
Security experts from ERPScan discovered a new directory traversal vulnerability in Oracle MICROS Point-of-Sale terminals, tracked as CVE-2018-2636, which could be exploited by an attacker to read sensitive data from devices without authentication from a vulnerable workstation.
“CVE-2018-2636 states for a directory traversal vulnerability in Oracle MICROS EGateway Application Service. In case an insider has access to the vulnerable URL, he or she can pilfer numerous files from the MICROS workstation including services logs and read files like SimphonyInstall.xml or Dbconfix.xml that contain usernames and encrypted passwords to connect to DB, get information about ServiceHost, etc.” reads the analysis published by ERPScan.
“So, the attacker can snatch DB usernames and password hashes, brute them and gain full access to the DB with all business data. There are several ways of its exploitation, leading to the whole MICROS system compromise.”
Oracle’s MICROS has more than 330,000 cash registers worldwide, it is widely adopted in food and beverage outlets (200,000+) and hotels (30,000).
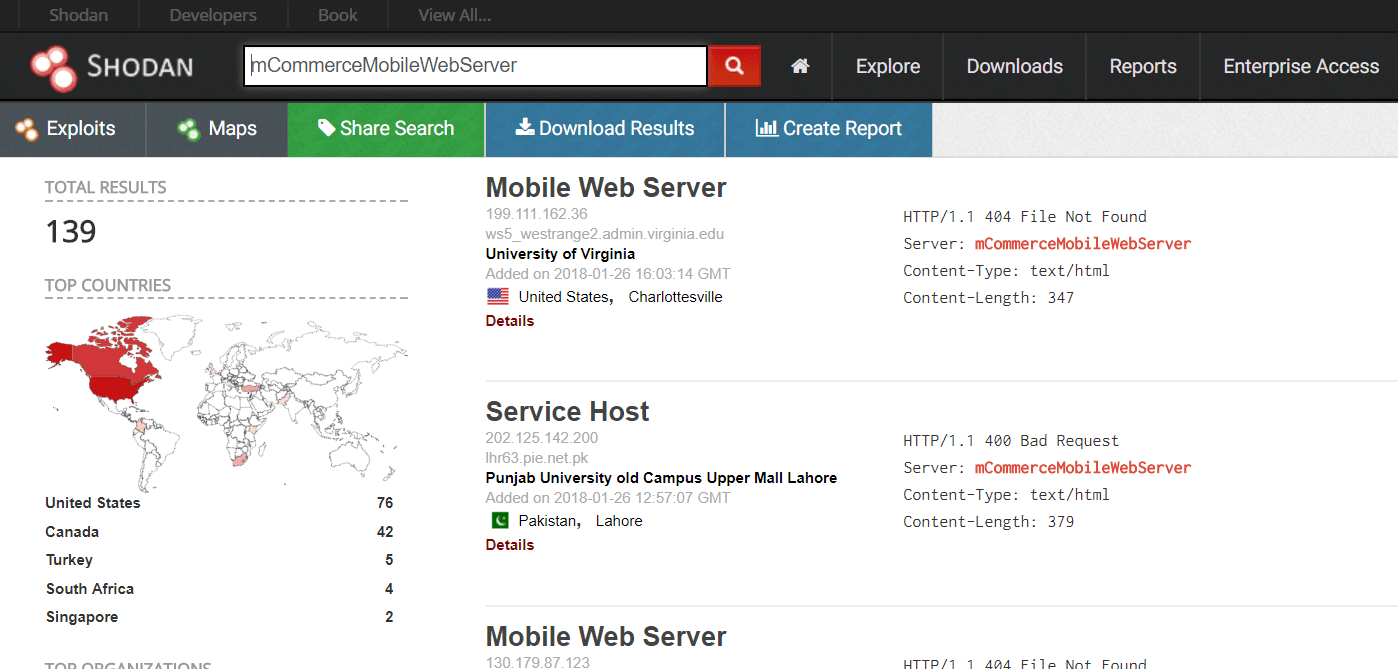
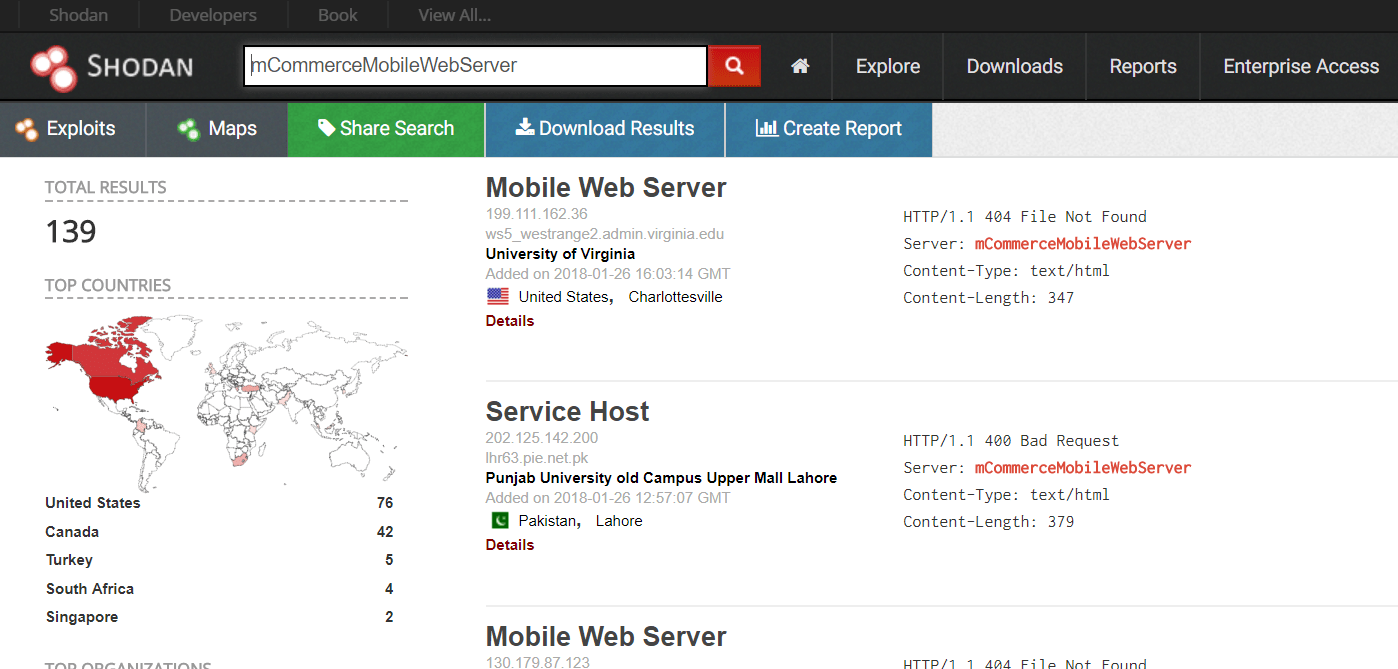
The researchers explained that it could be easy for a local attacker to access a MICRO POS URL, for example, he can find a digital scales or other devices that use RJ45 in the outlet and connect it to Raspberry PI, then scan the internal network. Another option is to locate such kind of devices exposed on the Internet, at the time of writing, there are 139 MICROS POS systems exposed online, most of them located in US and Canada.
This is not the first time when MICROS security is touched. In 2016, there was an incident where hackers attacked MICROS through the Customer Support Portal.
The vulnerability received the 8.1 CVSS v3 score.
“If you want to secure your system from cyberattacks, you have to persistently implement all security patches provided by your vendor. In our case, refer to Oracle CPU January 2018.” concluded the post.
This isn’t the first time that we approach the security of Oracle MICROS PoS systems, on August 2016, the systems of the Oracle MICROS payment terminals division were infected with a malware.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – hacking, Oracle MICROS PoS)
[adrotate banner=”5″]
[adrotate banner=”13″]