
Researchers at the Italian CERT warns of new Android malware dubbed Oscorp that abuses accessibility services for malicious purposes.
Researchers from security firm AddressIntel spotted a new Android malware dubbed Oscorp, its name comes from the title of the login page of its command-and-control server.
Like other Android malware, the Oscorp malware trick users into granting them access to the Android Accessibility Service, this means they will be able to read the text on the phone screen, determine an app installation prompt, scroll through the permission list and press the install button on the behalf of the user.
“not being able to access the private files of other applications, the actions of these malicious apps are “limited” to the theft of credentials through phishing pages (called, in the jargon of malware, injections), to blocking the device (intended as screen lock) and possibly to the capture of audio and video.” read the advisory published by Italy’s CERT-AGID (Italian language).
A few days ago, AddressIntel experts identified a domain called “supportoapp [.] Com” that was serving the file “Client assistance.apk”.
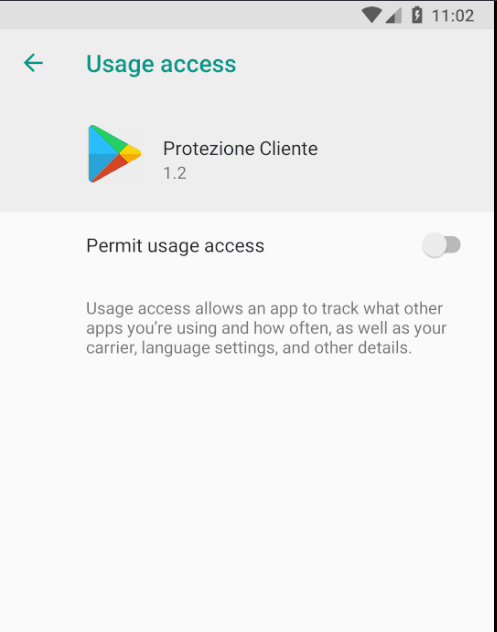
Once the app is installed, which is presented with the name “Customer Protection”, it asks users to enable the accessibility service.

The malware uses the Geny2 service to induce the user to enable the accessibility service and, once activated, automatically enable some permissions.
The malicious code reopens the Settings screen every eight seconds to force the user into granting the requested permissions for accessibility and device usage statistics.
Enabling accessibility service makes it possible to:
- Enable keylogger functionality.
- Automatically obtain the permissions and capabilities required by the malware.
- Uninstall app.
- Make calls.
- Send SMS.
- Stealing cryptocurrency.
- Stealing the PIN for Google’s 2FA
At the time of the analysis, the wallet used by the malware had $584.
The CERT’s report provides technical details about the malware, such as the description of the services such as the PJService used to collect info on the device. The malware communicates with the C2 via HTTP POST requests.
When the user opens one of the apps targeted by Oscorp, the malicious code will display a phishing page that asks him to provide a username and password.
The style of this screen is different for each app and it’s designed to trick the victim into providing the information.
“Android protections prevent malware from doing any kind of damage until the user enables accessibility service,” concludes the CERT-AGID’s advisory. “Once enabled, however, a ‘dam’ opens up. In fact, Android has always had a very permissive policy towards app developers, leaving the ultimate decision to trust an app or not to the end user.”
If you want to receive the weekly Security Affairs Newsletter for free subscribe here.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Intel)
[adrotate banner=”5″]
[adrotate banner=”13″]


