
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

APT

The fire in the OVH datacenter also impacted APTs and cybercrime groups

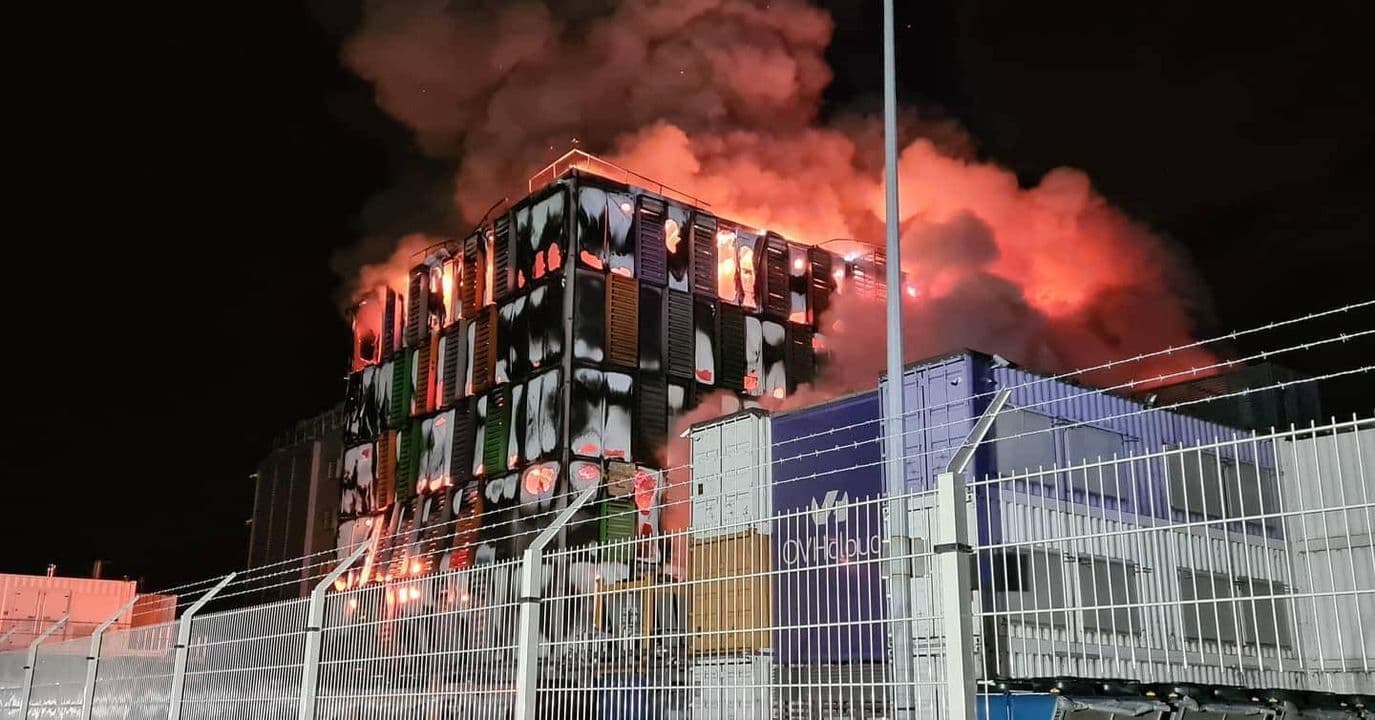
The fire at the OVH datacenter in Strasbourg also impacted the command and control infrastructure used by several nation-state APT groups and cybercrime gangs. OVH, one of the largest hosting providers in the world, has suffered this week a terrible fire that destroyed its data centers located in Strasbourg. The French plant in Strasbourg includes 4 […]

OVH fire

The fire at the OVH datacenter in Strasbourg also impacted the command and control infrastructure used by several nation-state APT groups and cybercrime gangs.

OVH, one of the largest hosting providers in the world, has suffered this week a terrible fire that destroyed its data centers located in Strasbourg. The French plant in Strasbourg includes 4 data centers, SBG1, SBG2, SBG3, and SBG4 that were shut down due to the incident, and the fire started in SBG2 one.

The fire impacted the services of a large number of OVHs’ customers, for this reason the company urged them to implement their disaster recovery plans. 

Nation-state groups were also impacted by the incident, Costin Raiu, the Director of the Global Research and Analysis Team (GReAT) at Kaspersky Lab, revealed that 36% of 140 OVH servers used by various threat actors as C2 servers went offline. The servers were used by cybercrime gangs and APT groups, including Iran-linked Charming Kitten and APT39 groups, the Bahamut cybercrime group, and the Vietnam-linked OceanLotus APT.

Of course, the incident only impacted a small portion of the command and control infrastructure used by multiple threat actors in the wild, almost any group leverages on multiple service providers and bulletproof hosting to increase the resilience of their C2 infrastructure to takedown operated by law enforcement agencies with the help of security firms.

“In the top of ISPs hosting Command and control infrastructure, OVH is in the 9th position, according to our tracking data. Overall, they are hosting less than 2% of all the C2s used by APTs and sophisticated crime groups, way behind other hosts such as, CHOOPA.” Raiu told to The Reg.

“I believe this unfortunate incident will have a minimal impact on these groups operations; I’m also taking into account that most sophisticated malware has several C2s configured, especially to avoid take-downs and other risks. We’re happy to see nobody was hurt in the fire and hope OVH and their customers manage to recover quickly from the disaster.”

If you want to receive the weekly Security Affairs Newsletter for free subscribe here.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, APT)

[adrotate banner=”5″]

[adrotate banner=”13″]


