Security Affairs
U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|Google fixes the eighth actively exploited Chrome zero-day of 2026|Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|Google fixes the eighth actively exploited Chrome zero-day of 2026|Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Threat actors started exploiting critical ownCloud flaw CVE-2023-49103

Threat actors started exploiting a critical ownCloud vulnerability (CVE-2023-49103) that can lead to sensitive information disclosure. ownCloud is an open-source software platform designed for file synchronization and sharing. It allows individuals and organizations to create their own private cloud storage services, giving them control over their data while facilitating collaboration and file access across multiple […]

ownCloud

Threat actors started exploiting a critical ownCloud vulnerability (CVE-2023-49103) that can lead to sensitive information disclosure.

ownCloud is an open-source software platform designed for file synchronization and sharing. It allows individuals and organizations to create their own private cloud storage services, giving them control over their data while facilitating collaboration and file access across multiple devices.

The vulnerability, tracked as CVE-2023-49103, resides in the Graphapi app, which relies on a third-party GetPhpInfo.php library that provides a URL. When this URL is accessed, it reveals the configuration details of the PHP environment (phpinfo).

Exposed information includes all the environment variables of the webserver. According to the advisory, in containerized deployments, these environment variables may include sensitive data such as the ownCloud admin password, mail server credentials, and license key.

The vulnerability impacts ownCloud owncloud/graphapi 0.2.x before 0.2.1 and 0.3.x before 0.3.1.

Multiple cybersecurity firms reported that threat actors are already exploiting the vulnerability.

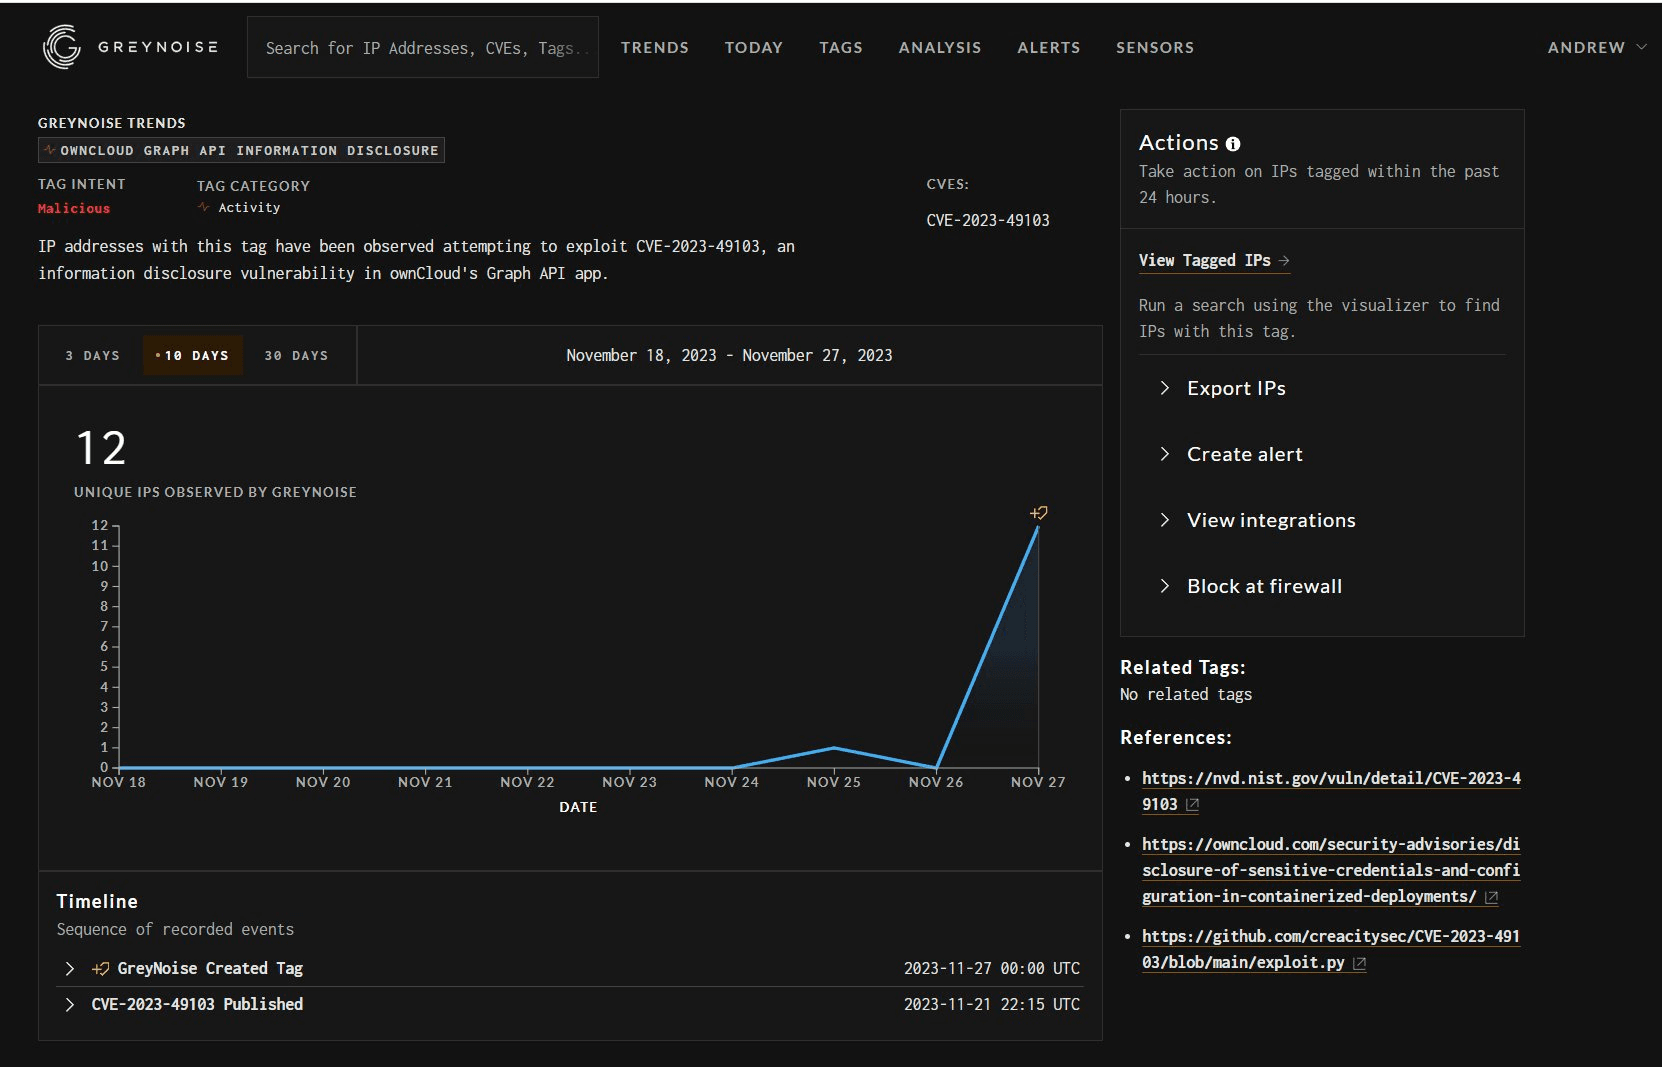
Cybersecurity firm GreyNoise observed the quick exploit in the wild of the issue.

“GreyNoise has observed mass exploitation of this vulnerability in the wild as early as November 25, 2023.” reported the company.

ownCloud

Researchers from Nonprofit cybersecurity organization Shadowserver Foundation have identified over 11,000 ownCloud instances that are exposed to the internet.

Most of the exposed instances are in Germany (2K), followed by the US (1,4K), and France (1,3K).

Cybersecurity firm Onyphe downplayed the impact of the attack, it reported that there are only 675 IP addresses exposing phpinfo() out of 19,453 IP addresses exposed.

Researchers recommend administrators perform the actions described in the ownCloud’s advisory.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ownCloud)