
Security Affairs
Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Data belonging 44 Million Pakistani mobile users leaked online

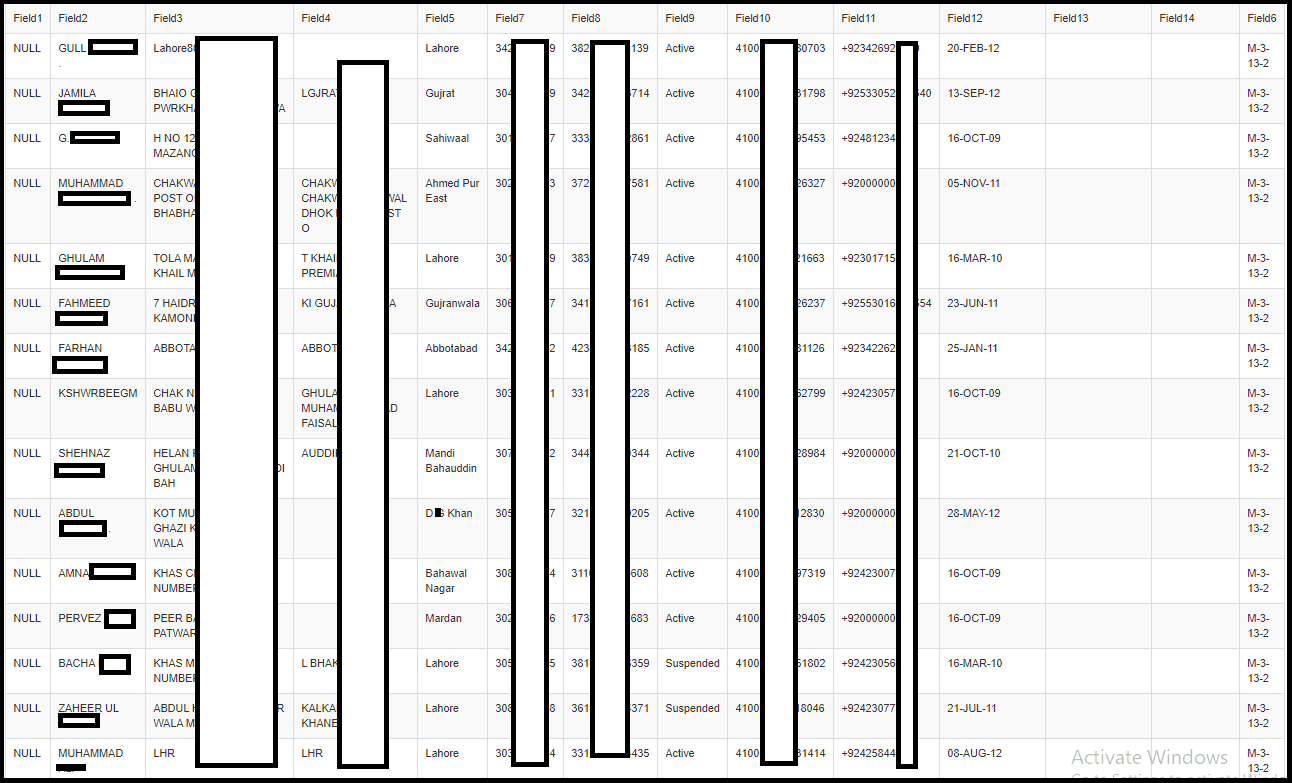
A threat actor is offering a database apparently belonging to Pakistan’s leading telecom service, it includes data of 44 Million Pakistani mobile users. The threat actor is leaking the database of Pakistan’s leading telecom service Mobilink’s (now @jazzpk). The database contains personally-identifiable and subscription information for 44,000,000 Pakistanis, including customer full names, home addresses (city, […]

Pakistani mobile users

A threat actor is offering a database apparently belonging to Pakistan’s leading telecom service, it includes data of 44 Million Pakistani mobile users.

The threat actor is leaking the database of Pakistan’s leading telecom service Mobilink’s (now @jazzpk).

The database contains personally-identifiable and subscription information for 44,000,000 Pakistanis, including customer full names, home addresses (city, region, street name), National identification (CNIC) numbers, mobile phone numbers, landline numbers, and dates of subscription.

It seems that the huge trove of data was the result of a data breach that took place in 2017, the oldest entries are dated back as 2013.

https://twitter.com/underthebreach/status/1257676922546503683

Last month, a hacker offered for sale a dump containing 115 Million Pakistani mobile user records for over $2 million worth of bitcoin.

The dump was discovered by a Dubai-based cybersecurity firm Rewterz (@rewterz) that confirmed its authenticity and the Pakistan Telecommunication Authority (PTA) is investigating the matter.

Experts at ZDNet have obtained a copy of the dump containing 44 Million records determined that it is part of 115 Million data dump.

The dump also includes information for Pakistani companies.

At the time it is not possible to determine if the dump has been stolen from Jazz servers, it is possible that hackers breached the systems of one of its business partners or a government organization.

Please vote Security Affairs for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Pakistani mobile users, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


