
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

PayPal fixed a flaw that allowed attackers to deliver malicious images

PayPal has fixed a vulnerability that could have been exploited by attackers to deliver malicious images through the payment pages of the website. The Security researcher Aditya K Sood discovered a vulnerability that could have been exploited by attackers to deliver malicious image through the payment pages of the PayPal website. The expert noticed that the […]

PayPal fixed a flaw that allowed attackers to deliver malicious images

PayPal has fixed a vulnerability that could have been exploited by attackers to deliver malicious images through the payment pages of the website.

The Security researcher Aditya K Sood discovered a vulnerability that could have been exploited by attackers to deliver malicious image through the payment pages of the PayPal website.

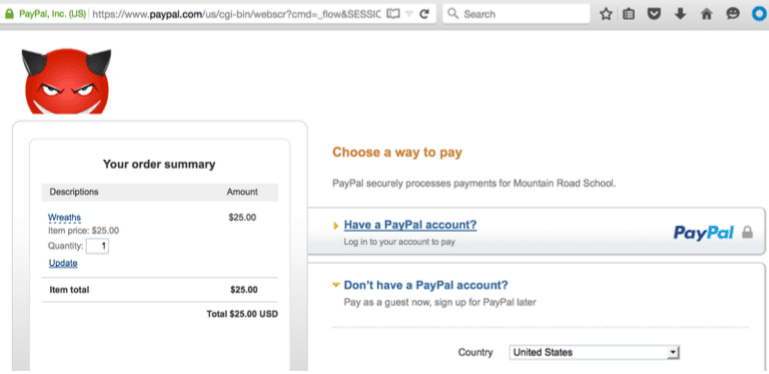
The expert noticed that the URL of payment pages set up by PayPal users included a parameter called “image_url,” then he tried to manipulate it. Sood discovered that it was possible to assign to the value of the parameter a URL pointing to an image hosted on a remote server.

This behavior could have been exploited by attackers to use a third-party vendor’s PayPal payment page to deliver malicious images.

The experts demonstrated the security flaw by delivering an image on a vendor’s payment page, obviously, the attacker could have delivered a malware or an exploit hidden in the image.

“This is an insecure design as PayPal allows remote users to inject images owned by them into the PayPal components used for transactions by the customers,” Sood explained to SecurityWeek. “That being said, the question is — can you deliver malware or an exploit through images? The answer is yes. Exploit techniques such as Stegosploit can be used to achieve that.”

The attack scenario is simple, the attacker needs to trick an unauthenticated user to click on a specially crafted link. The victims will see a URL belonging to PayPal.com, so he will likely trust the link clicking on it.

PayPal told to Sood that the attack scenario he hypothesized it unlikely because an attacker could use different methods to serve a malware. PayPal experts also added that the payment processor actively scan for malicious content.

PayPal flaw deliver malicious image


The vulnerability was reported to PayPal in January, but the IT giant fixed it only this month, Sood was rewarded with $1,000 for his discovery.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – PayPal, hacking)


