
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Mexican state-owned oil company Pemex hit by ransomware

On Sunday, the Mexican state-owned oil company Petróleos Mexicanos (Pemex) was infected with the DoppelPaymer ransomware. On Sunday, a piece of the DoppelPaymer ransomware infected systems of the Mexican state-owned oil company Petróleos Mexicanos (Pemex) taking down part of its network. According to the company, less than 5% of the computers in its network were […]

PEMEX

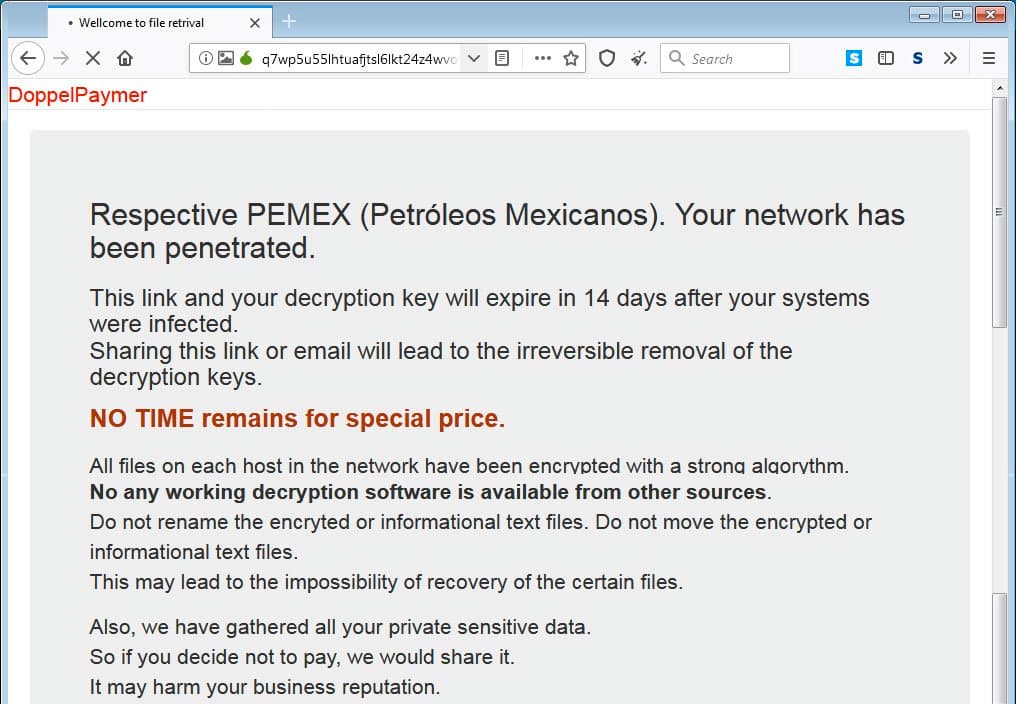
On Sunday, the Mexican state-owned oil company Petróleos Mexicanos (Pemex) was infected with the DoppelPaymer ransomware.

On Sunday, a piece of the DoppelPaymer ransomware infected systems of the Mexican state-owned oil company Petróleos Mexicanos (Pemex) taking down part of its network.

According to the company, less than 5% of the computers in its network were infected with ransomware.

Threat actors demanded a $4.9 million (565 BTC) ransom in order to decrypt their files, they are also threatening to leak sensitive data stolen by the company.

“Pemex’s internal network, like all major national and international government and financial companies and institutions, frequently receives threats and cyber attacks that have not prospered today.” reads a security notice published by the company. “Yesterday, Sunday, November 10, the State productive company received attempts at cyber attacks that were timely neutralized, affecting the operation of less than 5% of personal computer equipment. Notwithstanding the foregoing, Pemex reiterates that the production, supply and inventories of fuel are guaranteed.”

The Petróleos Mexicanos claims that it has quickly neutralized the attack, it also highlighted that operation and production systems were not impacted.  

Pemex confirmed that its infrastructure, like all major national and international government and financial organizations, is under unceasing targeted attacks, for this reason, it is continuing to improve its security measures.

The DoppelPaymer ransomware is a forked version of the BitPaymer ransomware likely developed by some members of the cybercrime gang tracked as TA505.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – ransomware, Petróleos Mexicanos (Pemex))

[adrotate banner=”5″]

[adrotate banner=”13″]


