
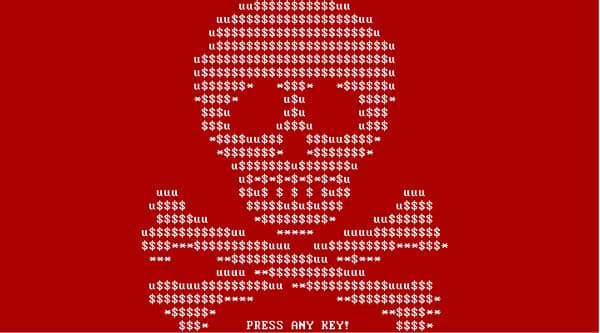
The Petya ransomware causes a blue screen of death (BSoD) by overwriting the MBR and leaves a ransom note at system startup.
Ransomware is one of the most dangerous threats of this first part of the year, recently experts at TrendMicro has spotted a new malicious code dubbed Petya (RANSOM_PETYA.A) that overwrites MBR to lock users out of the infected machines.
The Petya ransomware causes a blue screen of death (BSoD) by overwriting the MBR and leaves a ransom note at system startup.
Petya overwrites the MBR of the hard drive causing Windows to crash. When the victim tries to reboot the PC, it will impossible to load the OS, even in Safe Mode.
Users turning on the computer are displayed a flashing red and white screen with a skull-and-crossbones instead.

“As if encrypting files and holding them hostage is not enough, cybercriminals who create and spread crypto-ransomware are now resorting to causing blue screen of death (BSoD) and putting their ransom notes at system startup—as in, even before the operating system loads.” states the post published by Trend Micro.
“Imagine turning on your computer and instead of the usual Windows icon loading, you get a flashing red and white screen with a skull-and-crossbones instead.”
Another interesting aspect of the Petya is the delivery mechanism used by crooks that relies on legitimate cloud storage services like Dropbox.
“this is the first time (in a long time) that leads to crypto-ransomware infection. It is also a departure from the typical infection chain, wherein the malicious files are attached to emails or hosted in malicious sites and delivered by exploit kits.” continues the post.
Victims would receive an email that appears to be from an applicant seeking a position in a company, it includes a link to a Dropbox folder that contains its alleged CV.
The experts explained that one of the samples they analyzed, the Dropbox folder was containing contains two files, a self-extracting executable file that purports to be the CV, and a photo of the applicant.
The researcher discovered that the photo is a stock image.
The self-extracting executable is used to serve a Trojan onto the victim’s machine, the malware first disable any antivirus programs installed, then downloads and executes the Petya Ransomware.
In the following image are reported the instructions provided by the Petya ransomware to the victims in order to pay the ransom and restore the encrypted files.
The instruction includes a link to the Tor Project and how to download the Tor Browser to visit a page where purchase the decryption key to restore the data.

The crooks behind the Petya ransomware request the payment of 0.99 Bitcoins (nearly US$430), but the price would be doubled if the payment is not completed within a deadline.
(Security Affairs – Petya ransomware , cybercrime)


