
Experts from Proofpoint discovered a new phishing campaign designed to steal banking data leveraging tactics associated with malware distribution.
Security experts from Proofpoint have discovered a new phishing campaign that presents many similarities with campaigns used to spread the Cerber ransomware and the Ursnif banking Trojan.
Cyber criminals adopted a technique that leverages on the distribution of password-protected .zip archive containing a malicious document. The email messages sent by the crooks have the .zip file attached and the message content includes the password to open the archive.
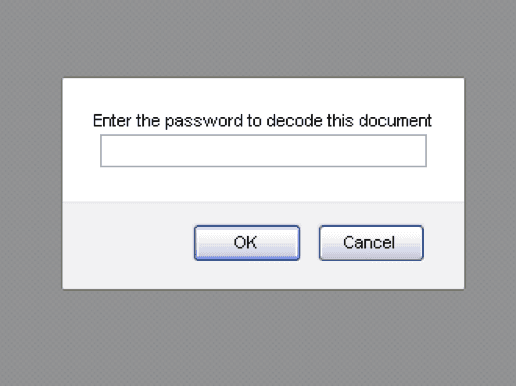
The phishing campaign aims to steal credit card data from the victims, the criminals sent them an HTML attachment that has been password-protected.

The email represents the first digits of the victim’s credit card account number aiming to create a sense of legitimacy without requiring actual knowledge of a potential victim’s actual card number.
The email attempts to trick the victim into giving away their credit card data, they have a sense of urgency requesting recipients to update their security information for their “new chip card.”
“The email sample that we analyzed was personalized with the recipient’s name and what appear to be the starting digits of their credit card account number. The starting digits for credit cards are standardized, though, so this just adds to the apparent legitimacy of the carefully crafted emails without requiring actual knowledge of the recipient’s’ card number.” states the report published by Proofpoint. “The emails also use stolen branding and social engineering to create a sense of urgency encouraging the recipient to update security information for their “new chip card””

The HTML file attachment used in this campaign was XOR-encoded to make harder the dynamic analysis.
Researchers noticed that HTML attachment uses JavaScript to implement the password protection instead using the password-protection feature in Microsoft Word.
When the victim enters the password the HTML attachment is decrypted and a typical credit card phishing template complete with stolen branding is displayed.
“Credential and credit card phishing are nearly as old as cybercrime itself. This hasn’t stopped phishing actors from innovating, exploring new approaches to convincing users to divulge personal, banking, and financial information. In this case, we observed threat actors taking a cue from malware distributors, using password protected document attachments to bypass anti-malware technologies and give recipients a false sense of security,” added Proofpoint.
[adrotate banner=”9″]
(Security Affairs – phishing campaign, cybercrime)


