
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

PlugX Trojan disguised as a legitimate Windows open-source tool in recent attacks

Researchers detailed a new wave of attacks distributing the PlugX RAT disguised as a legitimate Windows debugger tool. Trend Micro uncovered a new wave of attacks aimed at distributing the PlugX remote access trojan masqueraded as an open-source Windows debugger tool called x32dbg. The legitimate tool allows to examine kernel-mode and user-mode code, crash dumps, or CPU […]

PlugX

Researchers detailed a new wave of attacks distributing the PlugX RAT disguised as a legitimate Windows debugger tool.

Trend Micro uncovered a new wave of attacks aimed at distributing the PlugX remote access trojan masqueraded as an open-source Windows debugger tool called x32dbg. The legitimate tool allows to examine kernel-mode and user-mode code, crash dumps, or CPU registers. 

The x32dbg.exe analyzed by the researchers has a valid digital signature for this reason it is considered safe by some security tools. Its use allows threat actors to avoid detection, maintain persistence, escalate privileges, and bypass file execution restrictions.

PlugX

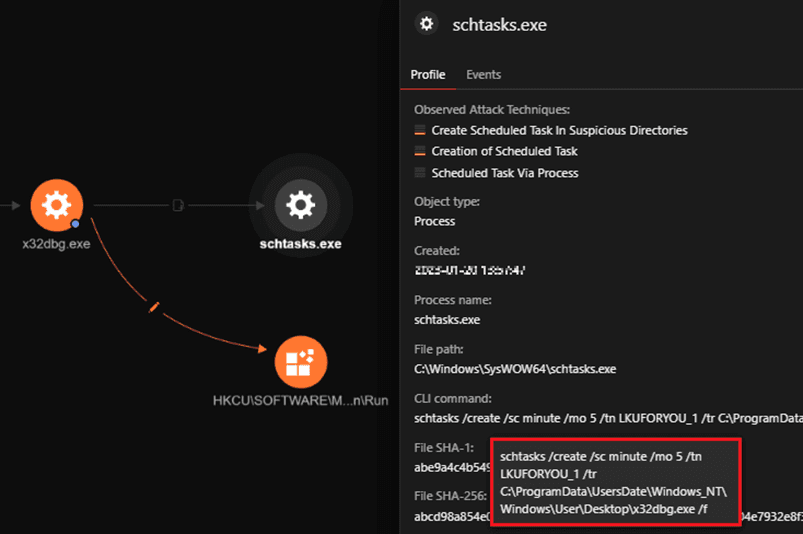
The RAT uses DLL side-loading to load its own malicious payload malicious DLL when a digitally signed software application, such as the x32dbg debugging tool (x32dbg.exe), is executed.

Attackers achieved persistence by modifying registry entries and creating scheduled tasks to maintain access even when the system is restarted.

Experts reported that the x32dbg.exe was used to drop a backdoor, a UDP shell client that collects system information, collects host information, and creates a thread to continuously wait for C2 commands, and decrypts C&C communication using the hardcoded key “Happiness is a way station between too much and too little.”

“Despite advances in security technology, attackers continue to use this technique since it exploits a fundamental trust in legitimate applications.” concludes the report that also provides Indicators of Compromise (IoCs). “This technique will remain viable for attackers to deliver malware and gain access to sensitive information as long as systems and applications continue to trust and load dynamic libraries.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Moshen Dragon)


