
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

ShinyHunters hacked Pluto TV service, 3.2M accounts exposed

A hacker has shared 3.2 million Pluto TV user accounts on a hacking forum for free, he claims they were stolen by ShinyHunters threat actor. Pluto TV is an American internet television service, it is an advertiser-supported video on demand (AVOD) service that primarily offers a selection of programming content through digital linear channels designed to emulate the experience of […]

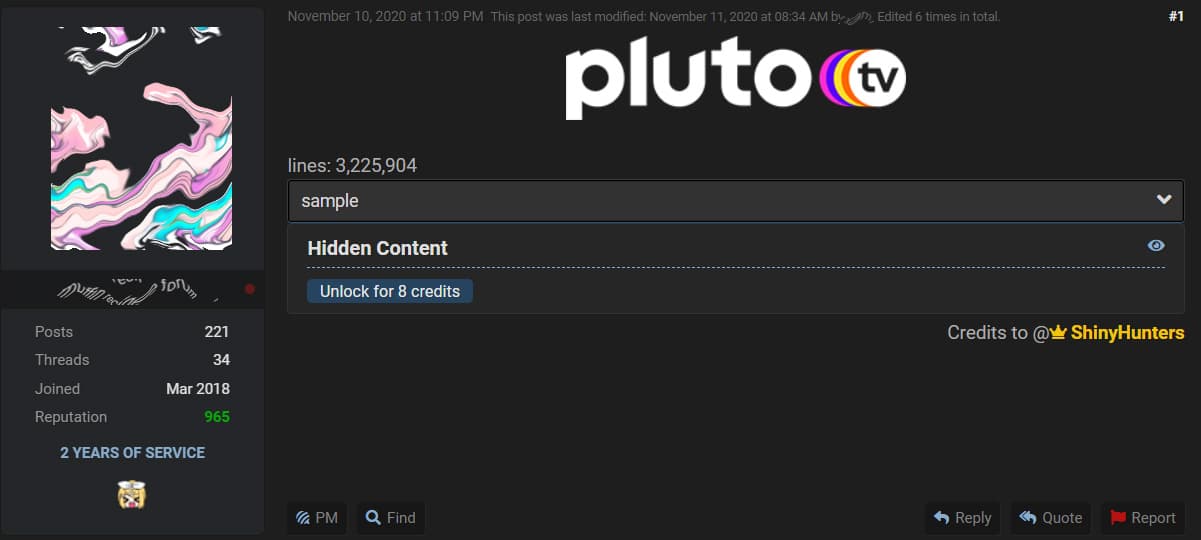
Shiny unters PLUTO TV

Source BleepingComputer

A hacker has shared 3.2 million Pluto TV user accounts on a hacking forum for free, he claims they were stolen by ShinyHunters threat actor.

Pluto TV is an American internet television service, it is an advertiser-supported video on demand (AVOD) service that primarily offers a selection of programming content through digital linear channels designed to emulate the experience of traditional broadcast programming. 

The service has over 28 million members.

The data breach appears to be the work of a well-known threat actor named ShinyHunters, who is behind many other security breaches, including the hacks of Microsoft’s private GitHub repository, the popular digital banking app Dave.com, and Animal Jam.

This week, a threat actor shared a database containing 3.2 million Pluto TV user records, he also added that the service was hacked by ShinyHunters.

Shiny unters PLUTO TV
Source Bleeping Computer

The dump includes PLUTO TV’s display name, email address, bcrypt hashed password, birthday, device platform, and IP address.

Bleeping Computer, which has validated the authenticity of the archive, reported that the latest record in the database was created on October 12th, 2018.

Pluto TV users are urged to immediately change their passwords, in case they share the same password at other sites, it is recommended that they change them too.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, ShinyHunters)

[adrotate banner=”5″]

[adrotate banner=”13″]


